-->
#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

The Hacker News | #1 Trusted Source for Cybersecurity News — Index Page

US-based website covering China's Bo Xilai scandal hacked

US-based website covering China's Bo Xilai scandal hacked

Apr 21, 2012
US-based website covering China's Bo Xilai scandal hacked A US-based website that has reported extensively on the Bo Xilai scandal in Chongqing says it has been crippled by a concerted hacker attack. The site was rendered inaccessible for much of Thursday, depriving readers of coverage of the latest developments in the downfall of Chinese Communist Party official Bo Xilai, said Watson Meng, 47, who runs the Chinese-language site from Durham, North Carolina. Watson Meng, the manager of the Boxun.com website, said it was out of action for several hours after a denial of service attack, in which several hackers overload a website with enquiries.The site was set up in 2000 to report on the pro-democracy movement and has been attacked before. The scandal has deeply embarrassed party leaders. Six years ago, when Shanghai powerful party chief Chen Liangyu was sacked in a corruption purge, Chinese social media was in its infancy and months went by with no word on the case against hi...
Hackers Launch DDoS Attack on D.C. Government Websites

Hackers Launch DDoS Attack on D.C. Government Websites

Apr 21, 2012
Hackers Launch DDoS Attack on D.C. Government Websites Hackers launched a DoS denial of service attack on D.C. government websites today, clogging the system with a flurry of requests so that it operates extremely slow or is impossible to load. “ The District government has detected an attempted intrusion into it’s technology infrastructure system, ” the D.C. Department of Homeland Security and Emergency Management said in an email to specified recipients around noon. “ Customers may experience intermittent difficulties in accessing the District’s web site as we attempt to address the issue. We are aggressively working to resolve this matter. ” In January the group launched a similar attack against the UFC for its support of the controversial Stop Online Piracy Act that was debated by Congress earlier this year. DDoS attacks have been launched by a variety of groups such as Anonymous and LulzSec against federal government websites and servers, including the FBI and CIA.
Specialized Trojan can stealing credit card details from hotel

Specialized Trojan can stealing credit card details from hotel

Apr 21, 2012
Specialized Trojan can stealing credit card details from hotel The next time you check in to a hotel, a cybercriminal could be checking you out. A remote access computer Trojan (RAT) designed to steal credit card details from hotel point-of-sale (PoS) applications is being sold on the underground forums, according to researchers from security firm Trusteer. Trusteer, the world’s leading provider of secure web access services, detected these schemes and says hotel poaching is a virile trade in underground and tech forums. Attack codes can be purchased in Visa underground forums for $280 and the spyware cannot be detected by anti-virus software. The package even includes a manual loaded with tips on how the poacher can trick the desk clerk into loading the spyware for them. Malware writers often repackage their malicious installers with new algorithms in order to evade signature-based antivirus detection, said Bogdan Botezatu, a senior e-threat analyst at antivirus vendor BitDef...
cyber security

Do You Need to Protect AI, Use AI, or Govern AI? SANS has Mapped All Three.

websiteSANS InstituteAI in Cybersecurity
Free frameworks, guidelines, and role-based AI security training, gathered in one place.
cyber security

Mikko Hyppönen and Enterprise CISOs on What AI-Speed Attacks Actually Change

websitePicus SecurityAI Security / Threat Detection
Join the summit where leading security teams lay out how they prepare for attackers with AI on their side.
Anonymous Hackers target F1 website in Bahrain GP protest

Anonymous Hackers target F1 website in Bahrain GP protest

Apr 20, 2012
Anonymous Hackers target F1 website in Bahrain GP protest Anonymous a collective who have hacked or taken down websites for social comment purposes, have turned their attention to the official Formula 1 website Formula1.com , taking it offline on Friday. The group also attacked F1-racers.net where it posted a message saying the " Formula 1 racing authority was well-aware of the Human Rights situation in Bahrain and still chose to contribute to the regime's oppression of civilians and will be punished. " According to  Statements: "Anonymous has watched with growing alarm the incredible human rights abuses of the Bahrain regime, We have watched this tyrannical government tear gas it's own people literally to death, with over 30 fatalities so far. The occasion of Anonymous re-launching Operation Bahrain will be this despicable Grand Prix Formula One race to be held in Bahrain tomorrow through the 22nd of April." "Beginning tomorrow, and lasting for...
Pastebin Censored ! Anonymous launches AnonPaste - Uncensored

Pastebin Censored ! Anonymous launches AnonPaste - Uncensored

Apr 20, 2012
Pastebin Censored ! Anonymous launches AnonPaste -  Uncensored Anonymous and the People’s Liberation Front have launched a “totally secure and safe alternative” to Pastebin, the site used by the hacktivist collective to dump data recovered from hacks.  AnonPaste  for people to post uncensored documents and files without compromising their identities. Shared content can be set to expire after 10 minutes, an hour, a day, a month, a year, or never. In addition, the site promises to remain advertising-free and unmoderated, maintain no connection logs, and store only encrypted data. The two groups said AnonPaste offers 256-bit AES encryption at the browser layer. AnonPaste supports a URL shortening feature and allows users to post up to 2MB of text snippets at a time. Users can specify how long they want the text to remain available on the site. AnonPaste , which accepts donations via WePay and BitCoins, was built using the open source ZeroBin software, which doesn...
zDefender - Enterprise smartphone IDS/IPS released by Zimperium

zDefender - Enterprise smartphone IDS/IPS released by Zimperium

Apr 20, 2012
zDefender - Enterprise smartphone IDS/IPS released by Zimperium Do you recall the security firm Zimperium which came out with ANTI , the killer Android app that allowed even the clueless to hack and pwn like a pentester? Zimperium, an Israeli security start up founded by Zuk Avraham, a world-renowned hacker and security researcher, has debuted its latest product, the zDefender at DEMO in Santa Clara, California. Called zDefender , this product can detect malicious attacks and take proactive measures to reduce threats via automatic preventive traffic filters and a remote management console. With the onslaught of mobile malware, everyone should have antivirus up and running immediately after purchasing a smartphone. You’d think you were protected from various attacks like man in the middle (MITM) attacks ? At DEMO Spring 2012 , Zuk planted 2 Routers, providing 3 Access points, which have claimed about 3,000 mobile device victims so far. zDefender is able to do this by us...
winAUTOPWN v3.0 Released - System vulnerability exploitation Framework

winAUTOPWN v3.0 Released - System vulnerability exploitation Framework

Apr 18, 2012
winAUTOPWN v3.0 Released - System vulnerability exploitation Framework The improved GUI extension - WINAUTOPWN ACTIVE SYSTEMS TRANSGRESSOR GUI [ C4 - WAST ] is a Systems and Network Exploitation Framework built on the famous winAUTOPWN as a backend.  C4 - WAST gives users the freedom to select individual exploits and use them. BSDAUTOPWN has been compiled, like always for various flavours and has been upgraded to version 1.8 alongwith all applicable exploits which have been added in this release. Included this time is the bsd_install.sh, which will set chmod on all applicable BSD compiled binaries. WINAUTOPWN requires PERL,PHP,PYTHON,RUBY and its dependencies alongwith a few others' too for smooth working of exploits included in it. winAUTOPWN and bsdAUTOPWN are available at http://winautopwn.co.nr
Rootdabitch version 0.1 - Multithreaded Linux root password Bruteforcer

Rootdabitch version 0.1 - Multithreaded Linux root password Bruteforcer

Apr 18, 2012
Rootdabitch version 0.1 - Multithreaded Linux root password Bruteforcer r00tw0rm hacker " th3breacher! "  release   Rootdabitch v0.1  ,which is a Multithreaded Linux/UNIX tool to brute-force cracking local root through su using sucrack. sucrack is a multithreaded Linux/UNIX tool for brute-force cracking local user accounts via su. The main feature of the Rootdabitch is that It's local brute forcer, using 10 passwords in 3 seconds. and works in background so you can leave it , when root is cracked it will email the user using /bin/mail . All for this, you need to have a php shell/reverse shell/ssh access to the target to run thistool and run it as a normal user, Upload this script into it and give it the execution permission and execute the script like:  ~ ./rootdabitch youremail@address.com If the password is cracked you will have a mail with the root password and the password will be stored into password.txt . Try it ! Download Rootdabitch 0.1
Pro-Tibetan activists become victim of Spear Phishing

Pro-Tibetan activists become victim of Spear Phishing

Apr 18, 2012
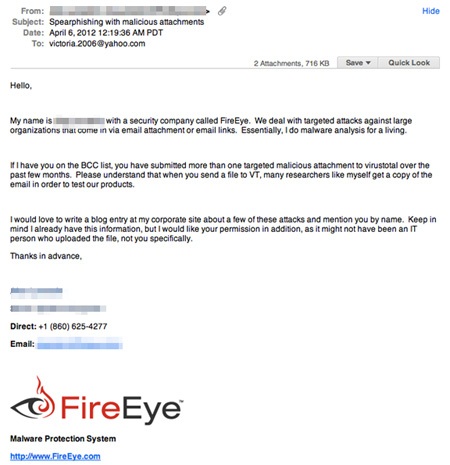
Pro-Tibetan activists become victim of Spear Phishing Hackers are ramping up their attacks against Tibetan activists and are using increasingly sophisticated techniques to deliver malware An interesting example of such a malicious email has recently been spotted by FireEye researcher Alex Lanstein, who is currently monitoring these spam campaigns. In the last few of months, several security vendors have reported targeted attacks that distributed malware designed to steal confidential information from people or organizations supporting the Tibetan cause. This tactic recently re-surfaced during our monitoring of Tibetan-leveraging malware campaigns. It came in the form of BKDR_RILER.SVR, a backdoor that arrives infected by PE_SALITY.AC. A simple Spear Phishing technique was used recently to trick Tibetan activists into opening malicious PDF email attachments, by quoting a legitimate email message sent by FireEye's Lanstein to people who submitted Tibet-related malware sampl...
Security Concern : Internet Enabled TV can be hacked !

Security Concern : Internet Enabled TV can be hacked !

Apr 18, 2012
Security Concern : Internet Enabled TV can be hacked ! Is your Internet TV vulnerable to hackers? Internet TVs could be the newest avenue for cybercriminals to infiltrate your home or business. Last year, Researchers at Mocana, a security technology company in San Francisco, recently discovered they could hack into a best-selling Internet-ready HDTV model with unsettling ease. According to a new report from researcher NPD In-Stat predicts that 100 million homes in North America and Western Europe will own television sets that blend traditional programs with Internet content by 2016. What exactly these Internet Enabled TV have ?  Its IP addresses, always-on network interfaces, CPUs, storage, memory, and operating systems the details that have offered hackers a bounty of attack choices for the last three decades. " Our goal was to see if we could hack into the set-top box, steal customer personal information, pirate services, and incur denial-of-service conditions. "...
Nikjju Mass injection campaign target more than 2 Millions Urls

Nikjju Mass injection campaign target more than 2 Millions Urls

Apr 18, 2012
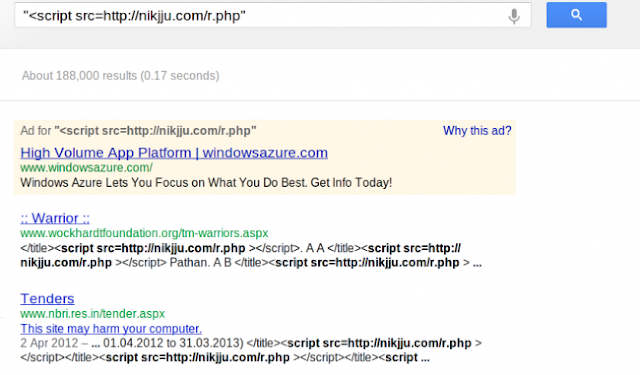
Nikjju Mass injection campaign target more than 2 Millions Urls Daniel Cid an open source developer and information security professional reported on Sucuri blog that their team tracked a new mass SQL injection campaign that started early this month and till now more than 180,000 URLs have been compromised.  Nikjju is a mass SQL injection campaign targeting ASP/ASP.net sites. At the time of writing Google has identified 361,000 pages infected with that javascript call, but the number is growing really fast. In this case it adds the following javascript to the compromised sites. One more interesting fact that researchers have noticed that  Nikjju.com domain was registered on April 1st 2012 and in 18 days more than 180,000 urls get infected. This mass Sql Injection also compromise some Government sites also , as listed below : jnd.xmchengdu.gov.cn study.dyny.gov.cn www.cnll.gov.cn www.bj.hzjcy.gov.cn www.mirpurkhas.gov.pk www.tdnyw....
Google Sent Hacked Notification Messages to Millions of Webmasters

Google Sent Hacked Notification Messages to Millions of Webmasters

Apr 18, 2012
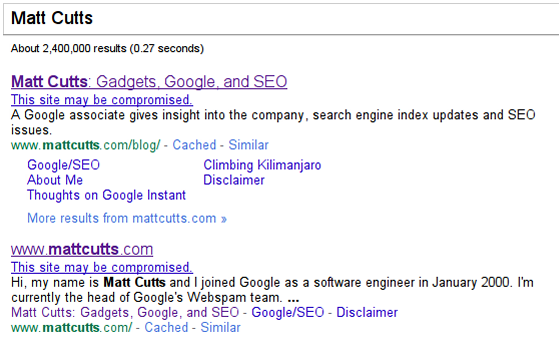
Google Sent Hacked Notification Messages to Millions of Webmasters Google’s head of the webspam team, Matt Cutts, announced on Twitter that they have sent out new message notifications to 20,000 web sites that are hacked. Specifically, Google sent these messages to sites doing “ weird redirects .” Weird redirects means the hack is where the hacker gains access to your HTACCESS and only redirects users who click from Google to your web site. Otherwise, if they type in the domain name directly, there will be no redirect. A year ago, Google began labeling hacked sites and sites with malware as sites that may compromised in the search results snippets. If a site has been hacked, it typically means that a third party has taken control of the site without the owner's permission, Hackers may change the content of a page, add new links on a page, or add new pages to the site. The intent can include Phishing to tricking users into sharing personal and credit card information or spam...
Julian Assange and Bradley Manning are Vested in Vision !

Julian Assange and Bradley Manning are Vested in Vision !

Apr 17, 2012
Julian Assange and Bradley Manning are Vested in Vision ! Two significant events will take place this week and cyber activists need to take note and pay attention. This will be your training on how to unfold the growing revolution that is spinning our world on a new and courageous path. First, Julian Assange has completed filming twelve episodes of his forthcoming show, “ The World Tomorrow ”. The first episode will be aired on RT and released online on Tuesday 17 April 2012, with other networks to follow. “ The World Tomorrow ” is a collection of twelve interviews featuring an eclectic range of guests, who are stamping their mark on the future: politicians, revolutionaries, intellectuals, artists and visionaries. The second event, Nobel Peace Prize nominee, and political prisoner Bradley Manning’s next appearance in court will take place April 24-26 at Ft. Meade, MD. Bradley Manning was arrested in May 2010 in Iraq on suspicion of having passed classified material to the whis...
Lebanese Government sites hacked by ‘Raise Your Voice’

Lebanese Government sites hacked by ‘Raise Your Voice’

Apr 17, 2012
Lebanese Government sites hacked by ‘ Raise Your Voice ’ A group calling itself ‘ Raise Your Voice ’ hacked on Tuesday around 15 Lebanese government websites to ask for an improvement in living standards, the day the parliament launches a three-day session to assess the cabinet’s performance. “ To our dear “beloved” Lebanese Government,We are RYV, short for Raise Your Voice, and we are simply a group of people who could not bare sitting in silence, watching all the crimes and injustice going on in Lebanon. We will not be silenced and brainwashed by your media. We will not stop until the Lebanese people mobilize, demand their rights, and earn them. We will not stop until the standards of living are raised to where they should be in Lebanon. We will not stop until this government’s self-made problems are solved, like the power shortage, water shortage, rise in gas prices and rise in food product prices. We are RYV, expect us to break the silence, whether in the streets or on the Int...
MI6, CIA and Department of Justice Tango Down !

MI6, CIA and Department of Justice Tango Down !

Apr 17, 2012
MI6, CIA and Department of Justice Tango Down ! Hacker group Anonymous claimed it took down the CIA website for the second time in two months following a new DDoS attack on the U.S. secret service which lasted 45 minutes.  Anonymous is reportedly on a DDoS rampage today, downing the CIA, Department of Justice, and two Mi6 websites. Members of the group claimed responsibility throughout Facebook and Twitter. Brazilian hacktivist Havittaja reportedly launched the initial offensive on the DoJ and CIA for “lulz” while other members jumped on board a short time later. The technique also known as a DDoS (distributed denial-of-service) attack, is a concentrated effort by multiple individuals to make a network busy to its intended users. The end result is server overload. Anonymous makes a freeware tool available to its members to carry out these attacks, which it calls the Low Orbit Ion Cannon. The collective targeted the department of justice in January as part of Operation M...
Banking System Vulnerability - 3 million bank accounts hacked in Iran

Banking System Vulnerability - 3 million bank accounts hacked in Iran

Apr 17, 2012
Banking System Vulnerability - 3 million bank accounts hacked in Iran Iran's Central Bank has announced that the electronic information of 3 million customers of 10 Iranian banks have been compromised. These banks now require their customers to change their ATM pin numbers before they can access their account. This has caused a rush to the ATM machines by the worried customers. The hacker was identified as Khosro Zare', a former bank-system specialist in Iran who recently left the country.Zare' claimed in a blog that he hacked the PIN codes to highlight the vulnerability of Iran's banking system. According to the report, the hacker had provided the managing directors of the targeted banks with information about the bank accounts of 1000 customers in the previous Iranian calendar year (ended on March 19) to warn them about the susceptibility of their computer systems and networks to cyber threats. But Central bank officials had earlier downplayed the reports, sayi...
Forensic FOCA - Power of Metadata in digital forensics

Forensic FOCA - Power of Metadata in digital forensics

Apr 16, 2012
Forensic FOCA - Power of Metadata in digital forensics Most of the e ort in today's digital forensics community lies in the retrieval and analysis of existing information from computing systems.  Metadata is data about data. Metadata plays a number of important roles in computer forensics. It can provide corroborating information about the document data itself. It can reveal information that someone tried to hide, delete, or obscure. It can be used to automatically correlate documents from different sources. More simply, electronic information about a file but not seen on a printed copy of the file. It is embedded and provides additional information, including when and by whom it was created, accessed, or modified. Informatica64  release Forensic FOCA (Fingerprinting Organizations with Collected Archives) , tool for forensic analysts focused on the use of metadata files to generate a forensic case. Several other metadata extraction tools exist but FOCA is co...
Phone Phreaking using Bluebox Demonstrated in India

Phone Phreaking using Bluebox Demonstrated in India

Apr 15, 2012
Phone Phreaking  using Bluebox   Demonstrated  in India Christy Philip Mathew , an Indian Information Security Instructor and Hacker demonstrated Phone Phreaking  using Bluebox in his lab. This time we have something really special that would remind us the phone phreaking. Actually Phone Phreaking reminds us about the life of Kevin Mitnick, Steve Wozniak and John Drapper, mean the olden times when they used to play around with the bluebox. What is Blue Box : This device is certainly one of the most unique pieces of electronic equipment that I have been able to collect so far. It is essentially a hacking tool disguised to look like a common 1970's Texas Instruments hand held electronic calculator. Basically a real calculator was sacrificed and modified to produce audio frequency signaling tones which allowed the user to freely (and illegally) access the Bell Telephone System long distance network. The origin of the name " blue box " was due to the f...
Android Video Malware found in Japanese Google Play Store

Android Video Malware found in Japanese Google Play Store

Apr 15, 2012
Android Video Malware found in Japanese Google Play Store A new Trojan has been found, and removed, from the Google Play/Android Market, McAfee reported on Friday afternoon. The post says applications carrying the Trojan promise, and in some cases deliver, trailers for upcoming video games or anime or adult-oriented clips, but they also request "read contact data" and "read phone state and identity" permissions before being downloaded. McAfee Mobile Security detects these threats as Android/DougaLeaker .A, the company said.McAfee said that the fifteen malicious applications of this sort had been found on Google Play, and that all had been removed from the market. The app gathers the Android ID not the IMEI code that can uniquely identify the device, but the 64-bit number that is randomly generated on the device's first boot and remains with it for the life of the device. The app also harvests the phone's phone number and contact list, along with every n...
Sabpab - Another Mac os Backdoor Trojan Discovered

Sabpab - Another Mac os Backdoor Trojan Discovered

Apr 14, 2012
Sabpab - Another Mac os Backdoor Trojan Discovered Security firm Sophos has discovered more malware for the Mac OS X platform called Sabpab . It uses the same Java vulnerability as Flashback to install itself as a “drive-by download.” Users of older versions of Java now have still more malware to worry about. It also doesn't require any user interaction to infect a system either just like Flashback all that needs to happen is for you to visit an infected webpage. Sabpab, according to Sophos, installs a backdoor that allows the hackers to capture screen snapshots, upload or download files and execute commands on infected Macs remotely. The Trojan creates the files /Users/ /Library/Preferences/com.apple.PubSabAgent.pfile /Users/ /Library/LaunchAgents/com.apple.PubSabAGent.plist Encrypted logs are sent back to the control server, so the hackers can monitor activity. Although one variant of Flashback installed a file in the LaunchAgents folder, not all tools for detectin...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources