-->
#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

The Hacker News | #1 Trusted Source for Cybersecurity News — Index Page

Android malware loaded with Linux kernel privilege escalation exploit

Android malware loaded with Linux kernel privilege escalation exploit

Jun 12, 2013
Malware authors are notorious for quickly leveraging new exploits in the public domain for nefarious purposes. A recently discovered Linux kernel Local privilege escalation exploit , which allows attackers to gain complete control of infected devices, has been ported to the Android smartphone platform. The Linux kernel 2.6.x, including Red Hat Enterprise Linux 6, Ubuntu 12.04 LTS, Debian 6 and Suse Enterprise Linux 11 are vulnerable to privilege escalation flaw with CVE-2013-2094 .  CVE-2013-2094 states, " The perf_swevent_init function in kernel/events/core.c in the Linux kernel before 3.8.9 uses an incorrect integer data type, which allows local users to gain privileges via a crafted perf_event_open system call. " Exploit for Linux machines is publically available here . Privilege escalation exploits are particularly dangerous as they can allow cybercriminals to gain complete control over the compromised device.  The exploit can be used to to access d...
FixMeStick's first to supports Windows 8 with Secure Boot ON

FixMeStick's first to supports Windows 8 with Secure Boot ON

Jun 12, 2013
Windows 8 PCs contain a new technology called Secure Boot that only boots devices that have been verified by Microsoft. Also Microsoft's own Offline Defender won't boot on Windows 8 PCs with Secure Boot on. Neither will Norton's Bootable Recovery Tool. We asked the guys at FixMeStick how their external hardware-based anti-malware device can boot on brand new Windows 8 hardware with Secure boot on, as well as 10 year old PCs with 32 processors running XP. Here's their answer: 1. It got a Master Boot Record. : In other words, it boots on BIOS-based PCs, essentially all PCs prior to Windows 8. 2. and it got UEFI boot partition : It also got a UEFI boot partition, so it will boot on PCs with the latest UEFI firmware too. 3. It's 32 bit : There's a 32 bit operating system on the stick so it will work with 32 bit microprocessors. Most rescue ISOs\disks are 32 bit only, so by default they work on 32 bit processors and 64 bit processors. 4. and it's 64...
Vulnerability in Whatsapp messenger media server

Vulnerability in Whatsapp messenger media server

Jun 12, 2013
If you own an iPhone or an Android device, then the chances are high that you're familiar with the extremely popular cross-platform messaging app, WhatsApp. According to a whitehat hacker Mohammed Saeed , Whatsapp media server ( media.whatsapp.com ) interface was vulnerable to Traversal local file inclusion. This vulnerability occurs when a page include is not properly sanitized, and allows directory traversal characters to be injected. Flaw allowed hacker to gather usernames via an " /etc/passwd " file and also another sensitive files like log files i.e   "/apache/logs/error.log" or " /apache/logs/access.log ". Flaw was reported by Mohammed with proof of conpect to Whatsapp security team on 27th May and was addressed this week. If you are also penetration tester and have something buggy that can help Whatsapp team to make there service more secure, feel free to contact them at  support@whatsapp.com .
cyber security

AI Security's Greatest Hits

websiteWizAI Security / Cheat Sheet
Get 7 of the most widely used AI security resources in one pack. Each asset provides practical tools for securing AI apps, models, and agents.
cyber security

Free Assessment: Identify Hidden Internal Risk

websiteBitdefenderAttack Surface / Threat Detection
Discover unnecessary user access to risky tools, shadow IT, based on real user behavior.
Anonymous Hacker outs wanted Edmonton men for child exploitation

Anonymous Hacker outs wanted Edmonton men for child exploitation

Jun 11, 2013
A YouTube video posted by a group calling themselves Anonymous is getting a lot of attention online, claims to have outed two men who allegedly tried to lure underaged girls over the internet. In a video posted on Friday, a member of Anonymous describes a sting operation in which two Edmonton-area men were allegedly caught trying to meet up with 13- and 14-year-old girls for sex. Bob Andrews, the head of ALERT’s Integrated Child Exploitation unit in Edmonton. “I think it’s really important to let the police do their jobs, and not judge someone in a public forum. ” Hacker also claims that they contacted Edmonton police about one meeting that was supposed to take place at West Edmonton Mall, but that police did nothing. “ There has been no reply. This is unacceptable. Together, we must act, and we must act swiftly to protect our children. For your benefit, we will begin to reveal the identities of the people that were identified ,” the video states. T...
New ZeuS Malware spreading automatically via USB Flash Drives

New ZeuS Malware spreading automatically via USB Flash Drives

Jun 11, 2013
The notorious Zeus Trojan , a family of banking malware known for stealing passwords and draining the accounts of its victims, has steadily increased in recent months. The malware family itself is frequently updated with mechanisms designed to evade detection by antivirus and network security appliances. Trend Micro experts spotted another new variant of  ZBOT Malware which is capable of spreading  itself automatically via USB Flash Drives or removable drives. According to report , this particular ZBOT variant arrives through a malicious PDF file disguised as a sales invoice document and when user opens this file using Adobe Reader, it triggers an exploit . Malware also has an auto update module, so that it can download and run an updated copy of itself. To self propagate, it creates a hidden folder with a copy of itself inside the USB drive with a shortcut pointing to the hidden ZBOT copy. Another variant of ZeuS #Malware spotted, with new feature of spread...
Edward Snowden, whistleblower behind the NSA surveillance Program leak

Edward Snowden, whistleblower behind the NSA surveillance Program leak

Jun 10, 2013
The individual responsible for one of the most significant leaks in US political history is Edward Snowden , a 29-year-old former technical assistant for the CIA and current employee of the defence contractor Booz Allen Hamilton . He's a high school dropout who worked his way into the most secretive computers in U.S. intelligence as a defense contractor and identify himself as the source of leaks about US surveillance programmes - PRISM . He is responsible for handing over material from one of the world's most secretive organisations the NSA. Verax was the name he chose for himself, “ truth teller ” in Latin. In an interview with The Guardian , Snowden publicly revealed himself as the source of documents outlining a massive effort by the U.S. National Security Agency to track cell phone calls and monitor the e-mail and Internet traffic of virtually all Americans.  Before his leak of U.S. intelligence, Snowden was living in paradise, working for a major U...
China Builds World's Fastest Supercomputer

China Builds World's Fastest Supercomputer

Jun 08, 2013
China has developed a new supercomputer known as Tianhe-2  which is twice as fast as US and Japanese systems has been measured at speeds of 30.65 petaflops or 74 percent faster than the current holder of the world's-fastest-supercomputer title. Titan, the U.S. Department of Energy's fastest supercomputer, has been clocked in at just 17.6 petaflops per second. Earlier reports said China is aiming for no lesser than a 100 Petaflops machine by 2015. China's National University of Defense Technology last week revealed about a massive machine in Changsha, that’s expected to come out next weekend during the International Supercomputing Conference. Tianhe-2 is built with Intel Ivy Bridge and Xeon Phi processors. The powerful system was assembled by Chinese company Inspur using tens of thousands of the latest multicore chips produced by Intel, with an addition of some home-made technology. In total, the supercomputer is said to contain over 3 million proces...
FBI raided Anonymous Hacker house, who exposed Steubenville Rapists

FBI raided Anonymous Hacker house, who exposed Steubenville Rapists

Jun 08, 2013
Another member of the hacker collective Anonymous has been unmasked this week. FBI raided the home of Deric Lostutter in April. Two laptops, flash drives, CD's, an external hard-drive, cell phones and an Xbox were reportedly seized during the raid. Deric Lostutter, a 26-year-old from Winchester, is also known as KYAnonymous , a member of the hacktivist collective Anonymous who leaked a video showing the young men who raped an unconscious teenaged girl in Steubenville , Ohio, bragging about what they did in a disgustingly proud manner. In March, football stars Trent Mays, 17, and Ma'lik Richmond, 16, were convicted of the rape. They were sentenced to a minimum of one year in a juvenile detention institution with a maximum stay until they are 21. Lostutter, a self-employed IT security consultant and self-described Anonymous member, said that he'd just returned from a turkey hunt when he noticed what appeared to be a FedEx truck in his driveway. " As I open the doo...
Pirate Bay co-founder 'Anakata' suspected of hacking Danish police databases

Pirate Bay co-founder 'Anakata' suspected of hacking Danish police databases

Jun 07, 2013
The Pirate Bay co-founder Gottfrid Svartholm Warg a.k.a  'Anakata' is suspected of being involved in one of Denmark's biggest hack attacks. Gottfrid was arrested in Cambodia in September 2012 and has been extradited from Cambodia to Sweden last year, charged with hacking the IBM mainframe of Logica, a Swedish IT firm that provided tax services to the Swedish government, and the IBM mainframe of the Swedish Nordea bank. Now he is suspected in another hacking case, where he and a 20-year-old Danish hacker are suspected to have obtained access to, among other things Danish social security numbers as well as business numbers. Danish suspect was arrested on Wednesday. In January, police in Sweden told colleagues in Denmark about a Danish IP address they had found during an investigation into hacker attacks against a company handling sensitive information for the Swedish tax authority. Grave cases of hacking are punishable by up to six years...
NSA's PRISM spy program, mining data from nine biggest Internet companies

NSA's PRISM spy program, mining data from nine biggest Internet companies

Jun 07, 2013
The National Security Agency , part of the U.S. military reportedly has a direct line into the systems of some of the world’s biggest Web and tech companies, i.e Microsoft, Google, Facebook, Skype. The NSA access is part of a previously undisclosed program called PRISM , 6-year-old program which allows officials to collect real-time information and as well as stored material including search history, the content of emails, file transfers and live chats, according to reports in the Washington Post . Project PRISM may be the first of its kind and also  GCHQ , Britain’s equivalent of the NSA, also has been secretly gathering intelligence from the same internet companies through an operation set up by the NSA. Later confirmed by the White House and members of Congress as saying that the government routinely seeks information in its fight to thwart domestic and international terrorism. Other services that are reportedly part of PRISM include PalTa...
Most Sophisticated Android malware ever detected

Most Sophisticated Android malware ever detected

Jun 07, 2013
A new piece of sophisticated Android malware has been discovered by security researchers at Kaspersky Labs . Dubbed as Backdoor . AndroidOS . Obad . a , it is the most sophisticated piece of Android malware ever seen. It exploits multiple vulnerabilities , blocks uninstall attempts, attempts to gain root access, and can execute a host of remote commands. It include complex obfuscation techniques that complicated analysis of the code, and the use of a previously unknown vulnerability in Android that allowed it to take control of and maintain a foothold on infected Android devices . There are two previously unknown Android vulnerabilities exploited by Obad . It can gain administrator privileges, making it virtually impossible for a user to delete it off a device. Another flaw in the Android OS relates to the processing of the AndroidManifest.xml file. This file exists in every Android application and is used to describe the application’s structure, define its laun...
FBI seized Citadel banking Trojan servers

FBI seized Citadel banking Trojan servers

Jun 06, 2013
Microsoft and the FBI have taken down a botnet that controlled millions of infected PCs, which was responsible for massive bank fraud.  Botnets are networks of computers infected with viruses that let them be controlled by hackers. The outfit runs the Citadel Botnets and is believed to have stolen more than $500 million from bank accounts over the past 18 months. Citadel is one of the biggest botnets in operation today. Citadel is a banking Trojan that has been in existence since 2011. As with most banking Trojans, Citadel is a full crimeware kit, providing the attackers with payload builders, a command and control (C&C) server infrastructure, and configuration scripts to target various banks. Citadel infected as many as 5 million PCs around the world including here in Australia and according to Microsoft, was used to steal from dozens of financial institutions, including American Express, Bank of America, Citigroup, Credit Suisse, eBay's PayPal, HSBC...
NSA collecting phone records of millions of US citizens daily

NSA collecting phone records of millions of US citizens daily

Jun 06, 2013
The National Security Agency is collecting telephone records for millions of Americans without informing the individuals involved. The shocking news has been revealed by ' Guardian ' whose journalists had access to a " Top Secret " court order, signed by Judge Roger Vinson, issued in April against Verizon . A copy of a secret order to obtain phone records for all Verizon customers was obtained, showing that the NSA was monitoring all incoming and outgoing calls made on that network.  The order obliges the Verizon Company to deliver the daily list of calls, " both within the Member States and between the United States and other countries ." The order was issued by the U.S. The Foreign Intelligence Surveillance Court directs Verizon's Business Network Services Inc and Verizon Business Services units to hand over electronic data including all calling records on an " ongoing, daily basis " until the order expires on July 19, 2013. ...
Warning ! Facebook virus Zeus targets bank accounts

Warning ! Facebook virus Zeus targets bank accounts

Jun 05, 2013
The infamous Zeus malware has once again resurfaced as per Symantec and is capable of draining your bank accounts. Zeus propagates through phishing messages that originate from an account that has been phished. Such a phished account will then start automatically sending messages to friends with links to ads telling them to check out a video or product.  Of course, you should not click as doing so will get your account phished as well. The program is sophisticated enough that it can replace a bank’s Web site with a mimicked page of its very own. The fake page can then ask for social security number information and other data that is then sold on the black market.  According to Trend Micro the pages are being hosted by the Russian criminal gang known as the Russian Business Network. Zeus was first detected in 2007 and it is spreading online. If you click on the Zeus virus, it is designed to steal your password and drain your bank account. Facebook is aware o...
26 Million Veterans data breached by eight state sponsored organizations

26 Million Veterans data breached by eight state sponsored organizations

Jun 05, 2013
Since 2010, foreign state sponsored organizations have repeatedly compromised an unencrypted database maintained by the Veterans Affairs Department that contains personally identifiable information on roughly 26 million veterans. Including at least eight foreign-sponsored organizations, mostly connected to the Chinese military had successfully compromised VA networks and data.  Other than this, possibly Russia were identified as likely culprits in the attempts to steal VA data. Details regarding exactly what information has been compromised are sparse, but unencrypted data included names, dates of birth and Social Security numbers of veterans that could be used to commit credit and identity fraud. Lack of basic security controls, such as encryption of data, make VA an easy target. The 2006 breach was caused by the theft of a VA employee's laptop, which contained personal information on about 26 million veterans and military personnel. From another report,...
Google ordered to hand over sensitive users details to FBI without a warrant

Google ordered to hand over sensitive users details to FBI without a warrant

Jun 05, 2013
Judge Susan Illston of the U.S. District Court for the Northern District of California on Friday has ordered the Google to hand over customer details to FBI without a warrant. FBI counter terrorism agents began issuing the secret letters, which don't require a judge's approval, after Congress passed the Patriot Act in the wake of the September 11 attacks. The letters are used to collect unlimited kinds of sensitive, private information, such as financial and phone records and have prompted complaints of government privacy violations in the name of national security. Google had previously refused to give the agency access to personal data such as the search history of its users, claiming such demands were illegal without a warrant. Electronic Frontier Foundation has challenged the letters in court, said: " We are disappointed that the same judge who declared these letters unconstitutional is now requiring compliance with them ." The decision came...
Russian hacker illegally ported Xbox LIVE Arcade Game to PC

Russian hacker illegally ported Xbox LIVE Arcade Game to PC

Jun 05, 2013
A Russian hacker who goes by the handle “ Barabus ” on the GameDev.ru forums illegally crack Xbox Live Arcade game The Dishwasher: Vampire Smile , developed by Ska Studios and port it on PC. He claimed that he was justified in illegal cracking: “ This is not piracy, this is restoration of justice. The authors are not very nice to publish the game exclusively for the Xbox 360, making it impossible for PC gamers to play in such a great game .”  The port is currently in beta and has no permissions from Ska Studios to even exist. But this isn’t a problem, according to the developer, as they say they're not stealing anything from Ska Studios. In the same forum post, the game’s creator Ska Studios founder James Silva said: “ I guess you could say my reaction is mixed. I'm flattered that there's this much interest in Vampire Smile on PC. I'm not mad about the crack itself, in fact, I'm actually pretty impressed. But I'm bewildered by the cracker's attempt to jus...
Twitter Vine app hacked by 16 year old Web developer

Twitter Vine app hacked by 16 year old Web developer

Jun 05, 2013
Recently Twitter has rolled out Vine app for Android, A new way to share video on twitter. The free app, which enables people to record and share clips of up to six seconds with other Vine users as well as on Twitter and Facebook. But on the very next day, Twitter’s video-sharing application Vine was hacked by 16-year-old Will Smidlein , who uploaded the three-and-a-half minute video of Rick Astley’s song “ Never Gonna Give You Up .” This video violated Vine’s usual code that only six second videos are posted. " I think I broke Vine ," Will Smidlein tweeted Monday night , where he described himself as a Web developer. What he did exactly? Smidlein decompile the app's code into a readable format, then modify few parts of the program that actually validate user to upload only 6 sec video. " Sorry, Twitter/Vine engineers, " he wrote. " I tried to keep it quiet, but the internet never forgets." ,  it could potentially embarrass a few of...
Turkish PM Erdogan’s staff emails hacked and leaked by Syrian Electronic Army Hackers as #OpTurkey

Turkish PM Erdogan’s staff emails hacked and leaked by Syrian Electronic Army Hackers as #OpTurkey

Jun 05, 2013
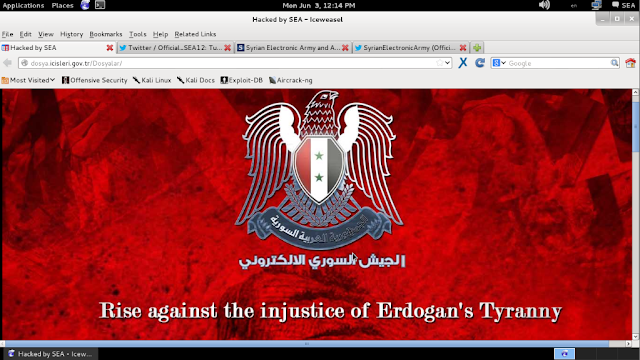
Syrian Electronic army appears to be taking part in ongoing operation against Turkey government website. Hackers collectively called Anonymous and SEA breached into Turkish Ministry of Interior website and the private information of staffers in PM Tayyip Erdogan's office. Hackers claimed that they gained access to staff email addresses, passwords and phone numbers. As exposed on internet, database include emails and plain text passwords of 90 users. In addition , Hackers also managed to take down the Turkey’s Prime Minister (basbakanlik.gov.tr) website. Many other sites belongs to Turkish govt was defaced last night by various hackers around the world including the country’s ruling party as operation #OpTurkey. The team also defaced the  dosya.icisleri.gov.tr/Dosyalar/  and placed their logo on site. " Rise against the injustice of Erdogan's Tyranny. Rise against the policies of hypocrisy perpetrated by the Erdogan Regime ." The defacement message read...
LinkedIn with Two-factor authentication and Cross Site Scripting Flaw

LinkedIn with Two-factor authentication and Cross Site Scripting Flaw

Jun 04, 2013
Two Factor Authentication is becoming a standard in the enterprise security space in an attempt to dually secure end users against malicious attacks.  Following Dropbox, Google and virtually everyone else, LinkedIn added two-factor authentication to its login process today. LinkedIn will provide temporary codes for two-factor authentication  through SMS messages. The extra step is designed to lessen the chances of computer hackers breaking into user accounts. To turn on two-step verification on LinkedIn, hit the icon in the top-right corner of the site, click on “Privacy & Settings,” and then on “Manage security settings” at the bottom. The site has provided instructions to its 225 million users on how to turn on the optional service. On other side, today @The_Pr0ph3t, whitehat Hacker from Spain reported a Cross Site Scripting Vulnerability in LinkedIn Developer site (developer.linkedin.com).  Flaw still exists on website a...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources