-->
#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

The Hacker News | #1 Trusted Source for Cybersecurity News — Index Page

Last.fm Confirms They Were Hacked, Change Your Passwords Now

Last.fm Confirms They Were Hacked, Change Your Passwords Now

Jun 08, 2012
Last.fm Confirms They Were Hacked , Change Your Passwords Now After this week’s LinkedIn fiasco, it appears the latest tech giant to fall to bored hackers is Last.fm. Music-streaming website Last.fm is the latest organisation to urge its users to change their passwords immediately. The London-based site, owned by CBS, said in an advisory that it was currently investigating a possible leak of passwords but did not provide any further details. The dating site said it is "continuing to investigate" but "as a precaution" has reset affected members passwords.Affected members will receive an email with instructions on how to reset their passwords.eHarmoney, which brands itself as "#1 Trusted Online Dating Site for Singles" has around 20 million registered online users. The breach was confirmed by Last.fm on their official Twitter account overnight, and comes amidst a backdrop of similar breaches, including at LinkedIn where up to 8 million passwords may ha...
Anonymous takes down MTNL website

Anonymous takes down MTNL website

Jun 08, 2012
Anonymous India takes down MTNL website The hacker-group Anonymous has struck again in India. This time the victim is the MTNL website. The group posted on their website, saying, ” We are against Internet Cencorship. Instead of blocking few URLs the ISP blocked the whole domain of various file sharing websites. The HC Madras, DoT didn’t isssue any list of websites to be blocked still ISP supported internet censorship. ” MTNL's corporate website could not be accessed, following the attack since afternoon and officials said efforts were underway to restore it. MTNL Delhi, Deputy - GM (Internet), Deepak Sharma said it was not hacking but 'denial of service attack' under which the server is unable to provide services to the customers. Anonymous has called for non-violent protests across several cities in India on June 9 to protest against what it alleges as ‘censorship’ of the internet. It accused the department of telecom of instructing the Internet Service Providers (I...
LinkedIn Confirms Millions of Account Passwords Hacked

LinkedIn Confirms Millions of Account Passwords Hacked

Jun 06, 2012
LinkedIn Confirms Millions of Account Passwords Hacked LinkedIn Wednesday confirmed that at least some passwords compromised in a major security breach correspond to LinkedIn accounts. Norweigan IT website Dagens IT first reported the breach, noting that “Two days ago a package on the 6.5 million encrypted passwords posted on a Russian hacker site. Vicente Silveira, Director at LinkedIn, confirmed the hack on the company's blog Wednesday afternoon and outlined steps that LinkedIn is taking to deal with the situation. He wrote that those with compromised passwords will notice that their LinkedIn account password is no longer valid. “It is worth noting that the affected members who update their passwords and members whose passwords have not been compromised benefit from the enhanced security we just recently put in place, which includes hashing and salting of our current password databases,” Linkedn director Vicente Silveira said in the blog post. The file only contains password...
cyber security

Do You Need to Protect AI, Use AI, or Govern AI? SANS has Mapped All Three.

websiteSANS InstituteAI in Cybersecurity
Free frameworks, guidelines, and role-based AI security training, gathered in one place.
cyber security

Mikko Hyppönen and Enterprise CISOs on What AI-Speed Attacks Actually Change

websitePicus SecurityAI Security / Threat Detection
Join the summit where leading security teams lay out how they prepare for attackers with AI on their side.
Researchers bypass Google Bouncer Android Security

Researchers bypass Google Bouncer Android Security

Jun 05, 2012
Researchers bypass Google Bouncer Android Security Google's Android platform has become the most popular mobile operating system both among consumers and malware writers, and the company earlier this year introduced the Bouncer system to look for malicious apps in the Google Play market. Bouncer, which checks for malicious apps and known malware, is a good first step, but as new work from researchers Jon Oberheide and Charlie Miller shows, it can be bypassed quite easily and in ways that will be difficult for Google to address in the long term. Bouncer is an automated process that scans apps for known malware, spyware, and Trojans, and looks for suspicious behaviors and compares them against previously analyzed apps. If malicious code or behavior is detected, the app is flagged for manual confirmation that it is malware. “ This screencast shows our submitted app handing us a connect-back shell on the Bouncer infrastructure so that we can explore and fingerprint its envir...
Flame Malware Spread Via Rogue Microsoft Security Certificates

Flame Malware Spread Via Rogue Microsoft Security Certificates

Jun 04, 2012
Flame Malware Spread Via Rogue Microsoft Security Certificates Microsoft released an emergency Windows update on Sunday after revealing that one of its trusted digital signatures was being abused to certify the validity of the Flame malware that has infected computers in Iran and other Middle Eastern Countries. The patch revoked three intermediate Microsoft certificates used in active attacks to “spoof content, perform phishing attacks, or perform man-in-the-middle attacks”.Microsoft also killed off certificates that were usable for code signing via Microsoft’s Terminal Services licensing certification authority (CA) that ultimately “chained up” to the Microsoft Root Authority.The authority issued certificates for users to authorise Remote Desktop services in their enterprises. The Microsoft blog post explains that a vulnerability in an old cryptography algorithm is exploited by some elements of Flame to make them appear as if they originated from Microsoft. Most systems around t...
SwaggSec gained access to China Telecom and Warner Bros

SwaggSec gained access to China Telecom and Warner Bros

Jun 04, 2012
SwaggSec gained access to China Telecom and Warner Bros A hacking group is claiming to have breached the networks of Warner Bros. and China Telecom, releasing documents and publishing login credentials. Swagg Security, or SwaggSec, the same hacker collective that breached Foxconn a few months ago to highlight the poor working conditions, has made its comeback. The hacking group posted on their Twitter account (under the name Swagg Security) that they had acquired access to the databases of both sites, as well as posted a statement on Pastebin . The group has allegedly stolen documents and login credentials, which were then posted to Pirate Bay . The torrent file posted by SwaggSec on The Pirate Bay doesn’t contain only the administrator details from China Telecom, but also some other information taken from their databases. SwaggSec said the China Telecom data is 900 user names and passwords for administrators on the company's network. The information was obtained through an in...
UGNazi hackers attack on CloudFlare via a flaw in Google

UGNazi hackers attack on CloudFlare via a flaw in Google

Jun 04, 2012
UGNazi hackers attack on CloudFlare via a flaw in Google After the FBI arrested Cosmo, the alleged leader of the UGNazi hacking group, the hackers attacked CloudFlare via a flaw in Google's two-factor authentication system. The CloudFlare hack allowed UGNazi to change the DNS for 4chan, so visitors to the site were redirected to a UGNazis Twitter account. Hackers were able to infiltrate the personal Gmail account of CloudFlare CEO Matthew Prince. "The attack was the result a compromise of Google's account security procedures that allowed the hacker to eventually access to my CloudFlare.com email addresses, which runs on Google Apps," CloudFare's CEO Matthew Prince shared . According to the statement on Pastebin , the hackers are not sorry for attacking 4chan.  4chan.org is the playground that allows pedophiles to share their "collections" and the disgusting bronies to hang out. The site is loosely monitored and child porn threads are allowed to ...
What is the Deep Web? A first trip into the abyss

What is the Deep Web? A first trip into the abyss

May 31, 2012
The Deep Web (or Invisible web) is the set of information resources on the World Wide Web not reported by normal search engines. According several researches the principal search engines index only a small portion of the overall web content, the remaining part is unknown to the majority of web users. What do you think if you were told that under our feet, there is a world larger than ours and much more crowded? We will literally be shocked, and this is the reaction of those individual who can understand the existence of the Deep Web , a network of interconnected systems, are not indexed, having a size hundreds of times higher than the current web, around 500 times. Very exhaustive is the definition provided by the founder of BrightPlanet, Mike Bergman, that compared searching on the Internet today to dragging a net across the surface of the ocean: a great deal may be caught in the net, but there is a wealth of information that is deep and therefore missed. Ordinary...
NSA intercepting 1.7 billion American electronic communications daily

NSA intercepting 1.7 billion American electronic communications daily

May 30, 2012
NSA intercepting 1.7 billion American electronic communications daily Since 9/11, the Agency has been able to "spy" on electronic communications without the need for court-approved warrants. The group has a large complex in Utah that cost $2 billion and holds the data. In 2006 the New York Times revealed that the Bush administration was eavesdropping on the electronic communications of Americans without the warrants required by law. The American Civil Liberties Union has created an infographic for mass distribution that shows some scary figures related to the U.S. National Security Agency. Four years ago Congress authorized the electronic surveillance of suspected terrorists and foreign agents located outside the United States, with provisions that supporters said would adequately protect the privacy of Americans. The only positive aspect of the FISA Amendments Act of 2008 was that the Congress imposed a four-year sunset provision on the powers it authorized. That sunse...
New Jersey mayor arrested for hacking recall website

New Jersey mayor arrested for hacking recall website

May 30, 2012
New Jersey mayor arrested for hacking recall website The FBI last week arrested the mayor of the northern New Jersey town of West New York, together with his son, on charges of hacking into a website and a related email account that called for the mayor's recall. Felix Roque, 55, the mayor of West New York, N.J., was arrested with his son, Joseph Roque, 22. They were released on $100,000 personal bond after neither entered a plea. According to the criminal complaint filed against Felix Roque and his son, on 2 February 2012 the two men began to conspire to hack into and disable a website called www.recallroque.com. Joseph Roque then allegedly performed a password reset for the Go Daddy account used to administer recallroque.com. This allowed him to cancel the domain name and effectively disable the website, the FBI agent said in the affidavit. The conspiracy and unauthorised computer access charges each carry a maximum possible sentence of five years in prison and a fine of u...
Hackers took control of two satellites for few minutes

Hackers took control of two satellites for few minutes

May 30, 2012
Hackers took control of two satellites for few minutes According to a US report recently claimed that hackers had managed to interfere with two military satellites, but one expert argues the amount of energy required would be too great for ordinary hackers. The hackers took control of the Landsat-7 and Terra AM-1 satellites for a grand total of 12 minutes and two minutes respectively. One might hope that the communications satellites suspended in orbit above the earth might be one component of the planet’s technology infrastructure that is safely out of harm’s way. But as satellite communications enthusiast Paul Marsh explained at the London Security B-Sides event in April, there are reasons to doubt the reports. He spoke about a similar story, reported in the late 1990s, about hackers supposedly accessing UK military satellite communications network SkyNet and ‘nudging’ one satellite out of synch. Whether Chinese hackers have that capability now is just one more matter of specu...
#Flame Malware - 21st Century Massive cyber attack on Iran

#Flame Malware - 21st Century Massive cyber attack on Iran

May 30, 2012
Flame Malware - 21st Century Massive cyber attack on Iran A massive, highly sophisticated piece of malware has been newly found infecting systems in Iran and elsewhere and is believed to be part of a well-coordinated, ongoing, state-run cyber-espionage operation. The Flame computer virus not only stole large quantities of information from various Iranian government agencies, but apparently even disrupted its oil exports by shutting down oil terminals, information security firm Symantec Israel said yesterday. The Flame virus recently found in Iran could be used to infect other countries, according to the International Telecommunications Union. As the United Nations agency charged with helping members protect their data networks, the ITU plans to issue a warning about the danger of Flame. Iran's National Computer Emergency Response Team (Maher) said in a statement that the detection and clean-up tool was finished in early May and is now ready for distribution to organisations a...
NASA SSL Digital Certificate hacked by Iranian Hackers

NASA SSL Digital Certificate hacked by Iranian Hackers

May 23, 2012
NASA SSL Digital Certificate hacked by Iranian Hackers Iranian hackers ' Cyber Warriors Team ' announced in an online post that it compromised an SSL certificate belonging to NASA and subsequently accessed information on thousands of NASA researchers. A space agency representative revealed that they’re currently investigating the incident. The group said the certificate was compromised by exploiting an existing vulnerability within the portal’s login system, but they didn’t outline the entire attack. Once they had control over the certificate, they claim to have used it to “obtain User information for thousands of NASA researcher With Emails and Accounts of other users [sic].” “ These incidents spanned a wide continuum from individuals testing their skill to break into NASA systems, to well-organized criminal enterprises hacking for profit, to intrusions that may have been sponsored by foreign intelligence services seeking to further their countries’ objectives, ” Paul K....
Zeus 2.x variant includes ransomware features

Zeus 2.x variant includes ransomware features

May 22, 2012
Zeus 2.x variant includes ransomware features Cybercriminals are getting more sophisticated, as reports are coming in that hacker coders have successfully merged a ransom trojan with a Zeus malware successor called Citadel . A notorious malware platform targeting financial information has added a new trick to its portfolio a digital version of hijack and ransom. F-Secure researchers have recently spotted a new Zeus 2.x variant that includes a ransomware feature. Basically a customised version of Zeus, the malware aims to provide better support for its offshoot of the Zeus code base, whilst at the same time allowing clients to vote on feature requests and code their own modules for the crimeware platform. Net-security explains the working of this Zeus 2.x variant,that Once this particular piece of malware is executed, it first opens Internet Explorer and points it towards a specific URL : lex.creativesandboxs.com/locker/lock.php. Simultaneously, the users are blocked from...
Anonymous hacks Bureau of Justice and leaks 1.7GB of data

Anonymous hacks Bureau of Justice and leaks 1.7GB of data

May 22, 2012
Anonymous hacks Bureau of Justice and leaks 1.7GB of data Anonymous has apparently hacked the United States Bureau of Justice Statistics and posted 1.7GB of data belonging to the agency on The Pirate Bay . This is a Monday Mail Mayhem release. Online statements attributed to Anonymous said they were responsible for the security breach and that the files they obtained include emails. " Today we are releasing 1.7GB of data that used to belong to the United States Bureau of Justice, until now, said Anonymous in a statement. The Department of Justice acknowledged that their webservers had indeed been breached, adding that their website as well as justive.gov had remained operational throughout the security breach. Department of Justice has been attacked multiple times since becoming a target for the hacking group after the shutdown of Megaupload. "  Within the booty you may find lots of shiny things such as internal emails, and the entire database dump. We Lulzed...
Call for Articles : THN Magazine June 2012, Malware Edition

Call for Articles : THN Magazine June 2012, Malware Edition

May 21, 2012
Call for Articles : THN Magazine June 2012, Malware Edition The Hacker News is calling for our June Magazine on the issue related to MALWARE . We'd like to see an analysis of the history of these most worrying viruses and the contemporary usage in cyber espionage and cyber warfare. It would be interesting to analyze the impact of the malware diffusion in the private sector and in government agencies, emphasizing the effectiveness of the cyber threat. Other topics to study are cyber crime activities that involve malware as method of monetization, with particular references to principal frauds schemes. What is the awareness level on hazards of the malware in common people and how the theat could harm new scenarios like mobiles and Cloud. What are the main countermeasures to mitigate virus diffusion? Thank you for your thoughtful consideration and we are looking forward to your work on this very important topic!  Email us at  admin@thehackernews.com Download all THN Ma...
Bogus Facebook apps spreading Android malware

Bogus Facebook apps spreading Android malware

May 20, 2012
Bogus Facebook apps spreading Android malware Third-party Android markets have traditionally been the main source of infection since the Android boom, as they are less strict than the genuine Play when it comes to bouncing malware. Today Gmanetwork reports that, Users of mobile devices running Google's Android OS were warned over the weekend against a new fake app of the social networking giant that may lead to potential Android malware. These duplicated applications have the same behavior as their original counterparts (in terms of functionality), but they perform a http 302 redirect to another link, that’s not Facebook-related, when they detect mobile traffic. What’s most concerning is that many of the fake app-based malwares in circulation have purported to be legitimate copies of some of the most popular titles around. No sooner were Android users on red alert for a dodgy Angry Birds Space app, were they informed of a phony Instagram app wreaking havoc through some of the ...
IBM Research domain hacked and defaced

IBM Research domain hacked and defaced

May 20, 2012
IBM Research domain hacked and defaced Hacker collective group dubbed Kosova Hacker Security or in other word KHS targeted IT giant & multinational technology and consulting corporation IBM. In this attack KHS successfully hacked into the official site of IBM Researcher ( http://researcher.ibm.com ). Hackers claims that, site had a SQL injection & remote code execution vulnerability using which they deface the website. At the time of writing the hacked url not working and Mirror of Hack can be seen here . Hackers said," we hack that why we dont like they computers :/ k ".
GFI WebMonitor - Web monitoring and Security

GFI WebMonitor - Web monitoring and Security

May 20, 2012
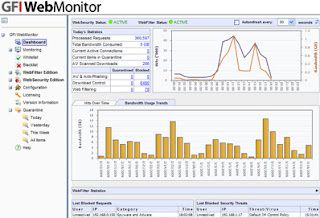
GFI WebMonitor - Web monitoring and Security With all the threats that Internet access can present to your users and your data, web security software is one of the most valuable investments you can make in your information security. Any solution should offer the following key protections: 1.       Site blocking 2.       Antivirus 3.       Reporting and logging GFI WebMonitor offers all that and more. GFI WebMonitor Unified Security includes both the web filtering and anti-malware capabilities, and can be installed as a standalone server or as an add-on to ISA or TMG. This web security suite can be installed on its own server or as a plug-in for TMG, and GFI offers a free 30-day-trial so you can evaluate it risk-free. Installation:  The installer for the TMG plug-in is straight-forward only requires a service restart, not a reboot. During the installation, you can choose to enable the option...
Quebec Liberal Party and Education Ministry websites take down in massive Cyber Attack

Quebec Liberal Party and Education Ministry websites take down in massive Cyber Attack

May 20, 2012
Quebec Liberal Party and Education Ministry websites take down in massive Cyber Attack Two provincial government websites as well as Quebec Liberal Party and Education Ministry websites went down early Saturday morning and remained inaccessible for most of the day. No one has claimed responsibility for the downed sites but Twitter was full of rumours on Saturday pointing to Anonymous, the loose group of cyber activists. The cyber troubles began just hours after a new law, Bill 78, passed in the National Assembly. It requires any group of 50 or more people holding a demonstration in the province to inform police eight hours in advance of their planned route and other pertinent details such as the start and end times. One of Anonymous’ Twitter accounts tweeted on Friday: “ Quebec Considers Draconian Anti-Protest Law ... Expect us .” Anonymous also threatened the website belonging to the province’s National Assembly. While some reported that the legislature's website had been ta...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources