-->
#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

The Hacker News | #1 Trusted Source for Cybersecurity News — Index Page

WebSurgery v0.5 - Web app testing tool Released

WebSurgery v0.5 - Web app testing tool Released

Jul 03, 2011
WebSurgery v0.5 - Web app testing tool Released WebSurgery is a suite of tools for security testing of web applications. Itwas designed for security auditors to help them with the web applicationplanning and exploitation. Currently, it uses an efficient, fast and stableWeb Crawler, File/Dir Bruteforcer and Fuzzer for advanced exploitation ofknown and unusual vulnerabilities such as SQL Injections, Cross sitescripting (XSS), brute-force for login forms, identification offirewall-filtered rules etc. Download Setup Download Portable Documentation
Pepper (Dating site) hacked by Anonymous #Antisec

Pepper (Dating site) hacked by Anonymous #Antisec

Jul 03, 2011
Pepper (Dating site) hacked by Anonymous #Antisec One of the Biggest Online dating website Pepper  http://www.pepper.nl/  hacked by Anonymous Hackers for Operation Antisec. Huge Data breached, 52000 users/passwords of users leaked by Anonymous on twitter on  http://privatepaste.com/af59e5a969
TriNity (Indian Girl Hacker) Strikes again to server with 690 websites

TriNity (Indian Girl Hacker) Strikes again to server with 690 websites

Jul 03, 2011
TriNity (Indian Girl Hacker) Strikes again to server with 690 websites Indian hacker girl, TriNity Strikes After along time. This time she  hack a windows server with 690+ Sites at 66.113.131.74 . Site attacked : http://www.coin.info/ http://catapult.coop/ Mirror of some sites on the same server : http://mirror.sec-t.net/defacements/?id=49702 http://mirror.sec-t.net/defacements/?id=49698 Complete List of Site : http://pastebin.com/4sF7ZQAB
cyber security

Reco Finds Four in Five Agents Run With Zero IT Oversight

websiteReco AISaaS Security / AI Security
See which agent permissions security teams aren't reviewing, and why it matters now.
cyber security

Build Your Email Security Strategy for the Agentic Era

websiteAdaptive SecurityEmail Security / Cybersecurity
Get the 2026 checklist for defending against AI phishing, compromised accounts, and human error.
UP Rajarshi Tandon Open University Allahabad Website Hacked

UP Rajarshi Tandon Open University Allahabad Website Hacked

Jul 03, 2011
UP Rajarshi Tandon Open University Allahabad Website Hacked Website of UP Rajarshi Tandon Open University Allahabad Hacked last night. Link  http://www.uprtou.ac.in/ Hacker wrote message on the site " SECURE YOUR WEBSITE.. OR ELSE GET HACKED BY SOMEONE...The Education system in India sucks.. Till when we would be learning all the bullshit physics, chem, history and commerce.. We need some real knowledge.. Baccha, kabil bano.. kamyaabi jhak marke peeche aayegi.. lol. .sorry admin.. just resotre your site..Don't worry.. nothing has been deleted... " Legend H mirror : http://legend-h.org/mirror/187224/uprtou.ac.in
Nmap 5.59 BETA1 - 40 new NSE scripts & improved IPv6

Nmap 5.59 BETA1 - 40 new NSE scripts & improved IPv6

Jul 01, 2011
Nmap 5.59 BETA1 - 40 new NSE scripts & improved IPv6 Official Change Log: o [NSE] Added 40 scripts, bringing the total to 217!  You can learn  more about any of them at http://nmap.org/nsedoc/. Here are the new  ones (authors listed in brackets):  + afp-ls: Lists files and their attributes from Apple Filing    Protocol (AFP) volumes. [Patrik Karlsson]  + backorifice-brute: Performs brute force password auditing against    the BackOrifice remote administration (trojan) service. [Gorjan    Petrovski]  + backorifice-info: Connects to a BackOrifice service and gathers    information about the host and the BackOrifice service    itself. [Gorjan Petrovski]  + broadcast-avahi-dos: Attempts to discover hosts in the local    network using the DNS Service Discovery protocol, then tests    whether each host is vulnerable to the Avahi NULL UDP packet    denial...
Official Website of Amy Winehouse - Songer/Songwriter Defaced

Official Website of Amy Winehouse - Songer/Songwriter Defaced

Jul 01, 2011
Official Website of Amy Winehouse - Songer/Songwriter Defaced Amy Jade Winehouse official website  http://www.amywinehouse.com/   defaced by Anonymous hackers for Antisec . Amy Jade Winehouse  (born 14 September 1983) is an English singer-songwriter, known for her powerful contralto vocals and her eclectic mix of various musical genres including R&B, soul, and jazz. She has received publicity over her substance abuse and mental health issues. Related hack => Meggit - US Military and Law Enforcement equipment supplier hacked for #Antisec - Read here
Meggit - US Military and Law Enforcement equipment supplier hacked for #Antisec

Meggit - US Military and Law Enforcement equipment supplier hacked for #Antisec

Jul 01, 2011
Meggit Database Hacked - US Military and Law Enforcement equipment supplier for #Antisec Database of www.meggitttrainingsystems.com a US Military and Law Enforcement equipment supplier has been hacked and exposed by Anonymous ( The Bash Crew ) .  Hackers said " People of the USA your government puts there trust and your money into these people and we got into there database useing a google dork and a simple sql injection.Any ways we hope this will cause many lulz atleast in spamming heads of the corp's and government that choose such a poorly secured site. " vUNL link :  http://www.meggitttrainingsystems.com/main.php?id=119 Hackers Release database on Pastebin :  http://pastebin.com/0r4A9DVR
Mesa Arizona Fraternal Order of Police website hacked, Data exposed !

Mesa Arizona Fraternal Order of Police website hacked, Data exposed !

Jul 01, 2011
Mesa Arizona Fraternal Order of Police website hacked, Data exposed ! Anonymous Hackers deface Mesa Arizona Fraternal Order of Police website -  http://mesafop.com/  . This hack is done for Operation Antisec. The Post a message and All data of  Arizona Police on the deface page. Alternate you can see written part on :  http://pastebin.com/RakyZgJE  . Hackers claim to deface following domains : azfop.com, azfop78.com, azfop5.com, tucsonfop.com, mesafop.com,azfop32.com, azfop50.com, azfop44.com, azfop62.com, azfop58.com Hackers expose Credit Card details and Email/Passwords of lots of officers Not only this, They also expose the usernames and passwords for 1200 FOP members in deface page.
SQL Injection Vulnerability in Google Lab Database System

SQL Injection Vulnerability in Google Lab Database System

Jun 30, 2011
SQL Injection Vulnerability in Google Lab Database System Very Big & Critical Vulnerability detected in Google Lab System. Vendor is already reported by hackers, But they don’t take positive step in this case, so finally hackers exposed  the vulnerability in public by  Bangladesh Cyber Army Admin - Shadman Tanjim on their Forum . Google Lab Website has SQL Injection Vulnerability and Dangerous thing is this Vulnerability is Exploitable. Hackers are able to get Tables, columns and data from Database. Google Lab Database has his own customize DB system. But Interesting things is their database system is Similar as Ms Access database. In this case Ms Access SQL Injection System is Also Work on Google Lab Database system. Statement By Hacker : I already contact with Google Corporation but they don’t give positive response, I think this is their big fault,  and will suffer for that. But if they give Positive response t...
MasterCard downed by ISP, not Anonymous hackers

MasterCard downed by ISP, not Anonymous hackers

Jun 30, 2011
MasterCard downed by ISP, not Anonymous hackers Two days before Anonymous declare that MasterCard again down by Ddos attack in support of Wikileaks & Anonymous via twitter . It was shortly after MasterCard went down that someone on Twitter, known as ibomhacktivist, promoted “ MasterCard.com DOWN!!! ”, adding the site was down for messing with WikiLeaks and Anonymous. But in actual, MasterCard.com was offline, and shortly after the outage was noticed by the public, someone on Twitter claimed credit. In a statement, MasterCard blamed the outage on an ISP issue, without discounting that they were attacked upstream. " MasterCard's corporate, public-facing Website experienced intermittent service disruption, due to a telecommunications/Internet Service Provider outage that impacted multiple users. It is important to note that no cardholder data has been impacted and that cardholders can continue to use their cards securely. We are continuing to monitor the situation c...
Indonesian and Australian police launched Cyber Crime Investigation Center

Indonesian and Australian police launched Cyber Crime Investigation Center

Jun 30, 2011
Indonesian and Australian police launched Cyber Crime Investigation Center Indonesian and Australian police officially launched a joint project called the Cyber Crime Investigation Center. The center was officiated by Indonesian National Police chief Gen. Timur Pradopo and Australian Federal Police chief Comr. Tony Negus at the National Police Headquarters in Jakarta on Thursday. Timur said the center had been planned since six months ago. " Today, we launch the center, which will be equipped with tools needed to carry out cyber crime investigation ," Timur said, adding that its communication technology equipment was being provided by the Australian government." Of course, this [center] will improve our capacity to detect and [investigate cyber] crimes, particularly transnational crimes ," he said. Negus said the center would allow the Indonesian National Police to deal with technology and IT-related crimes. He added that the Australian police force was looki...
OpenSSH 3.5p1 Remote Root Exploit for FreeBSD

OpenSSH 3.5p1 Remote Root Exploit for FreeBSD

Jun 30, 2011
OpenSSH 3.5p1 Remote Root Exploit for FreeBSD OpenSSH 3.5p1 Remote Root Exploit for FreeBSD has been shared by kcope on twitter . The Released note is as given below : OpenSSH 3.5p1 Remote Root Exploit for FreeBSD Discovered and Exploited By Kingcope Year 2011 -- The last two days I have been investigating a vulnerability in OpenSSH affecting at least FreeBSD 4.9 and 4.11. These FreeBSD versions run OpenSSH 3.5p1 in the default install. The sshd banner for 4.11-RELEASE is "SSH-1.99-OpenSSH_3.5p1 FreeBSD-20060930". A working Remote Exploit which spawns a root shell remotely and previous to authentication was developed. The bug can be triggered both through ssh version 1 and ssh version 2 using a modified ssh client. During the investigation of the vulnerability it was found that the bug resides in the source code file "auth2-pam-freebsd.c". http://www.freebsd.org/cgi/cvsweb.cgi/src/crypto/openssh/Attic/auth2-pam-freebsd.c This file does not exist in Fre...
Mobius Forensic Toolkit v0.5.8 Released

Mobius Forensic Toolkit v0.5.8 Released

Jun 30, 2011
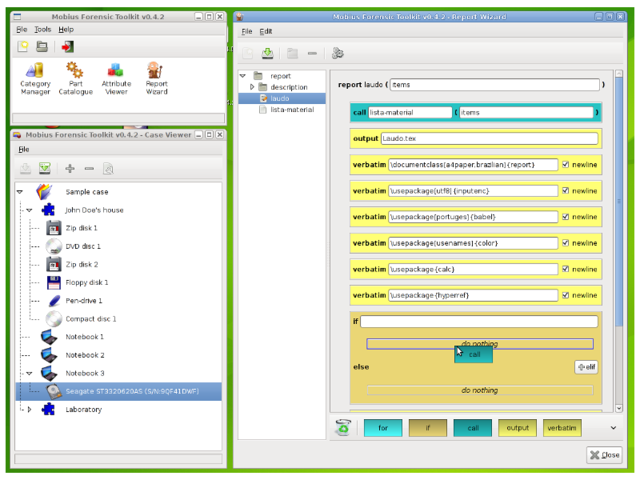
Mobius Forensic Toolkit v0.5.8 Released Mobius Forensic Toolkit is a forensic framework written in Python/GTK that manages cases and case items, providing an abstract interface for developing extensions. Cases and item categories are defined using XML files for easy integration with other tool Change Log : The Hive (registry viewer) features three new reports:email accounts, TCP/IP interfaces, and computer descriptions. All registry reports can be exported as CSV and the user password report can be exported in a format suitable for John the Ripper as well. Minor improvements were made Installation As root, type: python setup.py install Usage Run mobius_bin.py. Download Here
TDSS rootkit infects 1.5 million US computers

TDSS rootkit infects 1.5 million US computers

Jun 30, 2011
TDSS rootkit infects 1.5 million US computers Millions of PCs around the world infected by the dangerous TDSS ‘super-malware’ rootkit as part of a campaign to build a giant new botnet. The report is presented by researchers from security firm Kaspersky Lab. TDSS also known as ‘TDL’ and sometimes by its infamous rootkit component, Alureon. It has grown into a multi-faceted malware nexus spinning out ever more complex and dangerous elements as it evolves. Kaspersky Lab researchers were able to penetrate three SQL-based command and control (C&C) servers used to control the activities of the malware’s latest version, TDL-4, where they discovered the IP addresses of 4.5 million IP PCs infected by the malware in 2011 alone. Almost 1.5 million of these were in the US.If active, this number of compromised computers could make it one of the largest botnets in the world, with the US portion alone worth an estimated $250,000 (£155,000) to the underground economy. The researchers noti...
FBI searches LulzSec suspect home in Hamilton, Ohio

FBI searches LulzSec suspect home in Hamilton, Ohio

Jun 30, 2011
FBI searches LulzSec suspect home in Hamilton, Ohio The investigation into the LulzSec hacking team continues, with news that FBI agents have searched a house in Hamilton, Ohio. FBI investigation believed to have been fuelled by interviews with Ryan Cleary, but did not lead to charges. Federal agents are said to have searched a teenager's home in Jackson Road, Hamilton on Monday 27 June, although no-one was charged after the search warrant was served. Ohio teenager was known within LulzSec as " m_nerva ", who leaked text logs of discussions between the group after they had hacked into the website of an FBI affiliate at the beginning of June. After that, m_nerva's case address was listed by LulzSec as being in Hamilton, Ohio  Last week FBI agents searched the house of a woman in Iowa and questioned her about links with the group. LulzSec said in a statement that it had six members, though it never stated their gender.
Hackers target Al-Qaida Internet communications systems

Hackers target Al-Qaida Internet communications systems

Jun 30, 2011
Hackers target Al-Qaida Internet communications systems Computer hackers shut down Al-Qaida's ability to communicate its messages to the world through the Internet. Al-Qaida's online communications have been temporarily crippled.The attack was carried out within the past few days by unknown hackers targeting al-Qaida's Internet communications systems. According to Kohlmann," My guess is that it will take them at least several days more to repair the damage and get their network up and functioning again ,". A year ago, Al-Qaida's Internet communications suffered a similar hacker attack. British newspapers reported earlier this month that the the UK government hacked into an al-Qaida website last year and inserted recipes for making cupcakes in place of instructions on how to build bombs. The target was the group's English language magazine, "Inspire," intended for Muslims in the West. The magazine is the product of al-Qaida in the Arabian P...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources