-->
#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

The Hacker News | #1 Trusted Source for Cybersecurity News — Index Page

Hijacking Servers Remotely with Hikit advanced persistent threat

Hijacking Servers Remotely with Hikit advanced persistent threat

Aug 26, 2012
Security researchers have revealed the existence of an advanced persistent threat that has been making the rounds since April 2011.  Backdoor.Hikit  is a dangerous backdoor Trojan that will damage infected system and files. Usually, Backdoor. Hikit will open backdoor to allow remote attackers to connect to the infected system and carry out harmful activities, such as stealing information or destroying files and programs. It is really stubborn those antiviruses often fail to delete it for good, for it runs secretly and automatically when Windows boots without your knowledge or consent and can disguise it as fake system files or processes. Besides, many other threats, such as adware, redirecting virus, Trojan variants from family, such as Trojan Horse Generic 27.PN, BackDoor.Hupigon5.CJMY, Trojan.Zeroaccess.C, Trojan:win64/Sirefef.E and so on, which is really a threat to system and data security. According to experts from security firm Symantec , it all starts with the unknow...
Hackers Deface website of former British cabinet minister

Hackers Deface website of former British cabinet minister

Aug 26, 2012
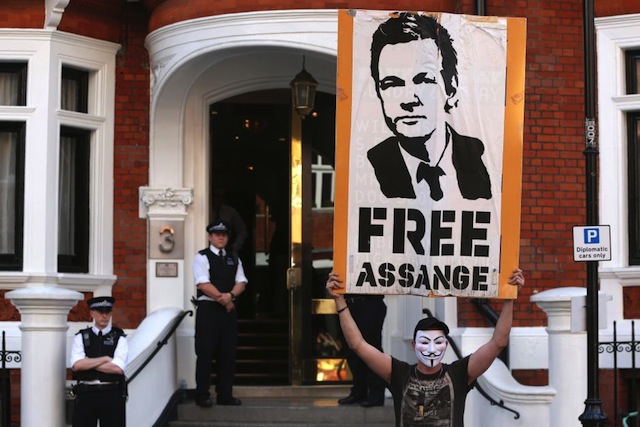
Hackers claiming allegiance to the Anonymous movement of cyber-rebels have defaced the website of a former British cabinet minister in solidarity with WikiLeaks founder Julian Assange. " If the reason ... is revenge for Assange's treatment, it's weird to attack me," Hain said in comments carried by the BBC. "They have not done their research because I have supported Assange and opposed his extradition. " Hain’s website was defaced Saturday by a group calling itself Anonymous UK, whose logo consisted of a dark, headless suit against a Union Jack. The group made a variety of allegations against the 62-year-old Labour Party politician, before adding: “ The UK’s persecution of Julian Assange will NOT be forgotten .” Assange's fight to avoid extradition took a dramatic turn in June, when Assange fled to the Ecuadorean Embassy seeking refuge. The ensuing standoff sparked a diplomatic crisis between Britain and Ecuador and could potentially drag on for months...
I know how to get Julian Assange out of the Embassy

I know how to get Julian Assange out of the Embassy

Aug 24, 2012
Let’s forget the political mumbo jumbo and posturing going on between countries about the release of Julian Assange. It is time to approach this in a “Sho-Gun” switch-a-roo style and get this over with. If not, we are going to be reading endless editorials and opinions about who is doing what, and what is doing who. Ugggh. With the help of the Ecuadorian Administration and some well planned orchestration with the group Anonymous, we can do this. Let’s let the Guy Fawkes mask slide us into victory with my new handy dandy plan that is sure to get the by now, haggard and worried Assange, into Ecuadorian freedom and fame. It is simple really. We need a call to arms, a ready army of Anons that can be recruited at a moments notice to storm the embassy. Just stop for a minute and picture it. Hundreds, no thousands, of masked Anons, wearing black, storming the embassy at night and throwing a wig on Assange and, of course, a mask (I am sure he has one) and moving him out into the crowd...
cyber security

Do You Need to Protect AI, Use AI, or Govern AI? SANS has Mapped All Three.

websiteSANS InstituteAI in Cybersecurity
Free frameworks, guidelines, and role-based AI security training, gathered in one place.
cyber security

Mikko Hyppönen and Enterprise CISOs on What AI-Speed Attacks Actually Change

websitePicus SecurityAI Security / Threat Detection
Join the summit where leading security teams lay out how they prepare for attackers with AI on their side.
Frankenstein Malware turning legitimate software into invisible malware

Frankenstein Malware turning legitimate software into invisible malware

Aug 24, 2012
Many malware and viruses can be identified by detection software because of known bits of malicious code. But what if there was a virus compiled from little bits of programs you already had installed? That's just what two security researchers are looking into. Frankenstein or The Modern Prometheus is a classic story in which a doctor creates life through technology in the form of a creature assembled from the parts of dead men. While this biological idea exists only in fiction, researchers have recently used it to craft a very ingenious piece of malware. Vishwath Mohan and Kevin Hamlen at the University of Texas at Dallas are interested in how malware disguises itself in order to propagate more widely. In Windows Explorer alone, Frankenstein found nearly 90,000 gadgets in just over 40 seconds, which means that malware created by the system would have a huge number of possible variations, work quickly, and be very difficult to detect. Frankenstein follows pre-written blueprints ...
Turkish hackers hack FC Spartak Moscow Soccer team

Turkish hackers hack FC Spartak Moscow Soccer team

Aug 24, 2012
Turkish hackers recently hacked the Web site of soccer team FC Spartak Moscow after the Russian team's fans burned Turkish flags and pictures of Atatürk during a Champions League playoff match against Turkish team Fenerbahce on August 21. A portrait of Atatürk next to a Turkish flag was also posted on the website. The group replaced the website's original content with a statement that called on the team to "immediately apologize." " You will immediately apologize to the Turkish Republic and the Turkish people. No crime goes without punishment, and FIFA may forgive you, but we won't ," The Spartak site was running again by Thursday afternoon after the club used its Twitter account to blame the incident on 'Turkish hackers. Spartak Moscow fans burned flags and posters of modern Turkey's founding father, Mustafa Kemal Atatürk, during their team’s 2-1 victory over the Istanbul giants in the first leg of their Champions League playoff.
NetWeirdRC - Commercial backdoor tool targeting Mac

NetWeirdRC - Commercial backdoor tool targeting Mac

Aug 24, 2012
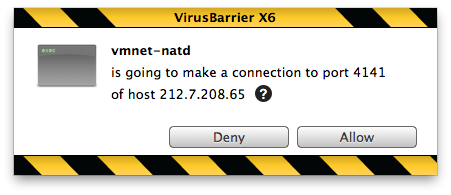
NetWeirdRC is a commercial backdoor tool targeting Mac OS X 10.6 and later, as well as Windows, Linux and Solaris, according to Intego . The product is sold for US$60 in the malware world, relatively cheap in comparison to the OSX/Crisis malware that was being sold for €200,000 ($240,000). It’s a commercial remote access tool, that after installation, calls home to the IP address 212.7.208.65 on port 4141 and awaits instructions. Then it carries out functions including installing files, gathering system information, stealing browser passwords and grabbing screen shots. In addition, it said, the malware can " harvest stored and encrypted usernames and passwords from Opera, Firefox, SeaMonkey, and Thunderbird browsers and mail clients ." It's able to infect Apple OS X (versions 10.6 and newer), Linux, Solaris, and Windows systems.
For the LULZ of it, I apologize to Lulzsec

For the LULZ of it, I apologize to Lulzsec

Aug 24, 2012
Note : This Article Cross posted from our Magazine's 13th Issue - August 2012 called "BOTNET | The Hacker News Magazine", Written by Ann Smith (Executive Editor, The Hacker News Magazine). You can Download full magazine free here . Shame on me.  When someone mentioned Lulzsec I would slightly bristle and turn a mighty heel towards the “real” movement.  You know, the Anons that are taking down corruption and terror, targeting the real enemies of the world.  If you were doing it for the LULZ of it, well, you were playing in the proverbial sand box and I thought you were hindering, instead of helping.  I even wrote an editorial spanking them for releasing the emails of servicemen who had signed up for a porn site.   Then, I read the book, WE ARE ANONYMOUS by Parmy Olson. Every person who considers themselves Anonymous or who  sympathizes and rallies for the cause, must read this book.  You will not only get a good education from this history ...
LulzSec Leader Sabu Gets 6-Month Sentencing Delay for helping Feds

LulzSec Leader Sabu Gets 6-Month Sentencing Delay for helping Feds

Aug 23, 2012
Today was the day that Hector Xavier Monsegur, a.k.a. Sabu, Xavier DeLeon, and Leon, was supposed to be sentenced for the 12 counts of computer hacking conspiracies and other crimes he pleaded guilty to, including the infamous hacks of HBGary Federal, HBGary, Sony, Fox, and PBS, but he has had his sentencing delayed, perhaps as a reward for assisting the US police with their enquiries and investigations. Monsegur allegedly rooted out the vulnerabilities used in the hacks conducted by LulzSec, which went on a high-profile tear in 2011 that exposed emails, documents, and other information of its victim organizations. Sabu is the hacker nom de plume of 28-year-old New Yorker Hector Monsegur, an unemployed father of two who allegedly commanded a loosely organized, international team of perhaps thousands of hackers from his nerve center in a public housing project on New York’s Lower East Side. According to the FBI, he could face a maximum sentence of 124 years and six months for 12 offe...
Power Plants Are Vulnerable To Hackers with Siemens flaw

Power Plants Are Vulnerable To Hackers with Siemens flaw

Aug 23, 2012
The U.S. Department of Homeland Security has issued an alert warning that hackers could exploit code in Siemens-owned technology to attack power plants and other national critical infrastructure. Justin W. Clarke, an expert in securing industrial control systems, disclosed at a conference in Los Angeles on Friday that he had figured out a way to spy on traffic moving through networking equipment manufactured by Siemens' RuggedCom division. RuggedCom, a Canadian subsidiary of Siemens that sells networking equipment for use in harsh environments such as areas with extreme weather, said it was investigating Clarke's findings, but declined to elaborate. Clarke said that the discovery of the flaw is disturbing because hackers who can spy on communications of infrastructure operators could gain credentials to access computer systems that control power plants and other critical systems. According to security researcher Justin W. Clarke, Rugged OS contains the same private key used...
Malware Campaign Targeting BlackBerry

Malware Campaign Targeting BlackBerry

Aug 23, 2012
Websense ThreatSeeker Network intercepted a malware campaign targeting BlackBerry customers. These fake emails state that the recipient has successfully created a BlackBerry ID. According to Security Labs , those users who are targeted receive an email with the subject line “ Your BlackBerry ID has been created .” The email encourages users to follow instructions in the attached file on how to “ enjoy the full benefits ” of their ID. The malware comes attached to an email that is an exact copy of the email you receive when creating a new BlackBerry ID. It teases you by asking you to download an attachment that allows you to fully appreciate the BlackBerry user experience. Those who open the attached .zip file will drop a handful of executable files that will modify the system registry to start malware programs upon the machine’s next startup.
Philippine police arrest 357 foreigners for cyber fraud

Philippine police arrest 357 foreigners for cyber fraud

Aug 23, 2012
Police on Thursday rounded up 357 foreigners accused of duping Taiwanese and Chinese citizens in an online scam in what an official described as the largest single-day operation against organized crime in the country.  Director Samuel Pagdilao Jr., CIDG director, said CIDG and Paocc agents led by Senior Supt. Ranier Idio raided 20 houses in several subdivisions in Quezon, Manila, Marikina, Cainta and Antipolo cities at around 6:30 a.m. on Thursday and they rounded up the foreigners. The suspects were brought to the Police National Training Institute (PNTI) in Camp Vicente Lim in Laguna. They face charges for violating the Access Device Act. The syndicate's operations involve the use of the internet, wherein the group will call unsuspecting victims in China, claiming that they represent police, prosecutor's office, courts, insurance companies, banks, and other financial institutions. The syndicate raked in at least P20 million ($472,000) each day using the scam, Pagdilao said...
McAfee will prevent vehicles from becoming vulnerable to Car Virus

McAfee will prevent vehicles from becoming vulnerable to Car Virus

Aug 22, 2012
Vehicles are becoming more and more reliant on computers for efficiency, safety systems, and infotainment systems. Most vehicles on the market today use throttle-by-wire systems, where the onboard computer controls the throttle of the vehicle. Toyota has had problems in the past with so-called unintended acceleration, with many pointing fingers at the electronic systems in the car. Intel's McAfee unit, which is best known for software that fights PC viruses, is one of a handful of firms that are looking to protect the dozens of tiny computers and electronic communications systems that are built into every modern car. McAfee, makers of the popular anti-virus software, are just one of the teams looking to protect automobiles from many bugs and viruses which could wreak havoc on the tiny computers inside modern cars. “ You can definitely kill people ”, said John Bumgarner, chief technology officer of the U.S. Cyber Consequences Unit, a non-profit organization that helps companies an...
Hijacking Virtual Machines with Crisis malware

Hijacking Virtual Machines with Crisis malware

Aug 22, 2012
The Windows version of Crisis , a piece of malware discovered in July, is capable of infecting VMware virtual machine images, Windows Mobile devices and removable USB drives, according to researchers from antivirus vendor Symantec.The installer was actually a Java archive (JAR) file which had been digitally signed by VeriSign. Crisis is distributed via social engineering attacks that trick users into running a malicious Java applet. The applet identifies the user's OS, Windows or Mac OS X and executes the corresponding installer. “ The threat uses three methods to spread itself: one is to copy itself and an autorun.inf file to a removable disk drive, another is to sneak onto a VMware virtual machine, and the final method is to drop modules onto a Windows Mobile device ,” Symantec explained in a blog post . Malware authors are putting significant efforts into making sure that new variants of their Trojan programs are not detected by antivirus products when they are released. Also...
Anonymous Hackers target website of Russian court that sentenced Pussy Riot

Anonymous Hackers target website of Russian court that sentenced Pussy Riot

Aug 21, 2012
The website of  the Moscow district court that sentenced three members of the band Pussy Riot to jail has been attacked by hackers posting anti-Putin messages. As well as the anti-Putin slogan Anonymous Russia posted an appeal for the band’s release as well as a video clip of one of the band’s songs.The slogan read: “ Putin’s thieving gang is plundering our country, wake up comrades! ” In a message posted on the website, the hackers said the in Russian that :  We are American group Anonymous. We don’t forget and we don’t forgive. Justice system has to be transparent. Pussy [Riot's members] are alive. Another caption called for the release of the band’s jailed members - Nadezhda Tolokonnikova, 22, Marina Alyokhina, 24, and Yekaterina Samutsevich, 30. Jude Marina Syrova said that the women had grossly violated public order and “ deeply insulted the faith of the believers with their disrespectful criminal act ” when they took over a church pulpit in Moscow’s Chri...
Half Million Chinese Android Devices got infected with SMSZombie

Half Million Chinese Android Devices got infected with SMSZombie

Aug 21, 2012
The amount of malware crafted and aimed at Android devices is ever-increasing. With Android being the most popular platform for smartphones and tablets around the world, Android users have become the low-hanging fruit when it comes to writing malware by the nefarious users. A new Android threat has affected 500,000 devices in China so far. Analysts at TrustGo Security Labs have discovered the Trojan!SMSZombie.A. It is a complex and sophisticated malware that exploits a vulnerability in the China Mobile SMS Payment System to fund unauthorised payments, steal bank card numbers and receipt information regarding money transfers. The trojan is difficult to detect, and even more difficult to remove.  SMSZombieA was first discovered on August 8, and the malware is embedded in several wallpaper apps. The wallpaper apps are noted to use provocative titles and nude images to encourage users to download. The trojan installs itself on a device after its user has downloaded and installed the...
MatrixDAR - First Military Grade Encryption for Android

MatrixDAR - First Military Grade Encryption for Android

Aug 21, 2012
AuthenTec, a leading provider of mobile and network security, today introduced a new security offering that provides military-grade encryption to data stored on today's Android smartphones and tablets without sacrificing device performance. AuthenTec's MatrixDAR(TM) for Android meets the stringent requirements of FIPS 140 certification.  MatrixDAR allows for full disk encryption in both the device and its storage media and incorporates AuthenTec's SafeZone software. This expands the company's security services for data-in-transit over SSL and IPSec connections and data-as-rest stored on a mobile device. It prevents unauthorized access and renders the smartphone or tablet useless if lost or stolen. AuthenTec offers the product for OEMs to directly install on devices, allowing IT departments to avoid installation of separate encryption software. “ Our new MatrixDAR offering gives smartphone and tablet OEMs the ability to easily integrate military-grade FIPS 140-cert...
Sensitive data in human brain successfully extract by Hackers

Sensitive data in human brain successfully extract by Hackers

Aug 21, 2012
It is now possible to hack the human brain ? YES ! This was explained researchers at the Usenix Conference on Security, held from 8 to 10 August in Washington State. Using a commercial off-the-shelf brain-computer interface, the researchers have shown that it’s possible to hack your brain, forcing you to reveal information that you’d rather keep secret. In a study of 28 subjects wearing brain-machine interface devices built by companies like Neurosky and Emotiv and marketed to consumers for gaming and attention exercises, the researchers found they were able to extract hints directly from the electrical signals of the test subjects’ brains that partially revealed private information like the location of their homes, faces they recognized and even their credit card PINs. Brain-computer interface or BCIs are generally used in a medical setting with very expensive equipment, but in the last few years cheaper, commercial offerings have emerged. For $200-300, you can buy an Emotive...
Julian Assange - The most Fuckable Man on the Planet

Julian Assange - The most Fuckable Man on the Planet

Aug 19, 2012
Julian Assange made a speech today from the balcony of the Ecuadorian Embassy in London and I felt a primal urge brought on by the fact that this man, in all his manly glory, has stuck his proverbial neck out for the essence of life. Truth and Justice. He is a handsome and articulate man, fighting for the basic rights of every human being on the planet. What could be more sexy? Putting aside husbands, lovers, friends, and professional media, he can Wik my Leaks anytime he wants. Julian started by reminding us that he is there because he can’t be elsewhere. He blended his thanks for Ecuador’s stand for justice with the announcement of an emergency meeting of Latin American countries next Friday specifically to address his situation and to defend the right of asylum. He made a straight forward statement that the United States must return to the values it was founded on and “ Obama must do the right thing .” Bradley Manning must be released and “ he is a hero and example to all ...
AMD Blog Hacked, Database leaked on Internet

AMD Blog Hacked, Database leaked on Internet

Aug 19, 2012
A team of Hackers called, " r00tBeer Security Team " today hack into official blog of Advanced Micro Devices (AMD) which is a American multinational semiconductor company. AMD is the second-largest global supplier of microprocessors based on the x86 architecture and also one of the largest suppliers of graphics processing units. Hacker deface the blog page ( http://blogs.amd.com/wp-content/r00tbeer.html ) and also leak the complete user database of blog on his twitter account. Leaked database SQL file uploaded on Mediafire by Hackers which include 200 AMD user's Emails, Wordpress Blog Usernames and Passwords. During the time of writing, I think AMD is not aware about that they are the Victim of a Hack attack. We are tweeting to the AMD team for informing them. Screenshot of Hack as shown below: Now only AMD, these hackers also hack another High Profile website called " TBN - The Botting Network ", A Popular forum to learn How to make Money with 96000 member...
Serious Security Flaw : iPhone Bug Allows SMS Spoofing

Serious Security Flaw : iPhone Bug Allows SMS Spoofing

Aug 17, 2012
A rather serious security flaw in the iPhone ’s SMS messaging system has been discovered and revealed by well-known security researcher and jailbreak extraordinaire ‘pod2g’. Security flaw affecting all iPhones that he says could facilitate hackers or thieves to access your personal information. The researcher claims that the flaw has actually been present in Apple’s iPhone software ever since the first iPhone was launched in 2007, but has failed to have been picked up on by anybody, including Apple it seems. Researcher revealed an SMS spoofing flaw that affects every version of Apple’s mobile OS. Using the flaw, hackers could spoof their identities via text and send messages asking for private information (by pretending to be from a users’ bank, for example), or direct users to phishing sites. Users would be under the impression they were replying to the sender displayed on the screen of their iPhone, when in fact the text would be routed through to a different number without their ...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources