-->
#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

The Hacker News | #1 Trusted Source for Cybersecurity News — Index Page

No Turning Back ~ 2012 by Patti Galle

No Turning Back ~ 2012 by Patti Galle

Jan 16, 2012
No Turning Back ~ 2012 by Patti Galle Patti Galle , from The Hacker News Editorial Staff wrote an Article in THN Magazine January Edition . We would like to share this read with all of our site readers. Rebellions are most always rooted in a call for justice, decency and morality. World history is full of countless rebellions against despots and others who did not conform to the will of the people. And as inequality grows to absurd new heights around the world and institutions of power are considered fundamentally dishonest, corrupt, and leaders no longer command the respect and confidence of the people then you have societies where social upheaval is inevitable. Rebellions spring up against fraudulent power and authority, and it is grounded in real outrage against mass murder (neo-imperialism, neo-colonialism), violation of human rights (torture, war crimes), widespread lying and hypocrisy, endemic political corruption, unrestrained thirst for money and power, and unprecedented ...
Wireless Penetration Testing Series Part 2: Basic concepts of WLANs

Wireless Penetration Testing Series Part 2: Basic concepts of WLANs

Jan 16, 2012
Wireless Penetration Testing Series Part 2: Basic concepts of WLANs This blog post is in continuation of the Wireless Penetration Testing and Hacking series we started ( Part 1: Getting Started with Monitoring and Injection ) on the basis of the “SecurityTube Wi-Fi Security Expert” ( SWSE ) course which is based on the popular book “ Backtrack 5 Wireless Penetration Testing ”. In the third video, the instructor talks about some of the basic concepts of WLANs. We learn that communication over WLAN's happens over frames. There are mainly 3 types of WLAN frames which are Management frames, Control frames, and Data frames. These types of packets also have different subtypes . We learn that an SSID is a name given to an Access point or a network consisting of multiple Access points. We then learn about Beacon frames which are broadcast frames sent out periodically by Access point to broadcast their presence in the current RF (Radio frequency) vicinity. The instructor then starts wire...
Saudi hacker target Israeli stock exchange and National air carrier

Saudi hacker target Israeli stock exchange and National air carrier

Jan 16, 2012
Saudi hacker target Israeli stock exchange and National air carrier Saudi cyber Hacker OxOmar  struck again on Monday. This time disrupted the websites of Israel's stock exchange and National air carrier. Last week he had leaked private information about more than 400,000 Israelis. Credit card companies said around 25,000 numbers, some of them expired, had been posted . The pro-Palestinian group is referring to itself as “ Nightmare .” The site of El Al crashed but officials at Israel's flag carrier would not confirm or deny the incident was the work of hackers. A person familiar with the situation at El Al Israel Airlines says the carrier took down its website Monday after the alleged Saudi hacker network behind previous attacks warned that both sites would be targeted. " There has been an attack by hackers on the access routes to the (TASE) website. The stock exchange's trading activities are operating normally ," said Orna Goren, deputy manager of the excha...
cyber security

Reco Finds Four in Five Agents Run With Zero IT Oversight

websiteReco AISaaS Security / AI Security
See which agent permissions security teams aren't reviewing, and why it matters now.
cyber security

Build Your Email Security Strategy for the Agentic Era

websiteAdaptive SecurityEmail Security / Cybersecurity
Get the 2026 checklist for defending against AI phishing, compromised accounts, and human error.
Nigerian Army Education site hacked by Nigerian Hacktivists

Nigerian Army Education site hacked by Nigerian Hacktivists

Jan 16, 2012
Nigerian Army Education site hacked by Nigerian Hacktivists Today the official website of Nigerian Army Education Corps ( NAEC ) got defaced by some Nigerian Hacktivists, He tweeted . The Complete message posted by Hackers as shown below:
Hacker will release full Norton Antivirus code on Tuesday

Hacker will release full Norton Antivirus code on Tuesday

Jan 16, 2012
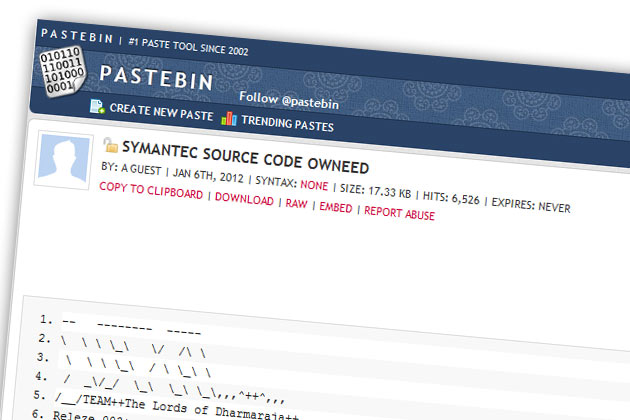
Hacker will release full Norton Antivirus code on Tuesday A hacker with code name of ' Yama Tough ' announce via Twitter that on Tuesday he will leak the full source code for Symantec Corp's flagship Norton Antivirus software which is 1,7Gb src. Last week Yama Tough has released fragments of source code from Symantec products along with a cache of emails. The hacker says all the data was taken from Indian government servers. Yama Tough is trying to prove that Indian government was snooping on America and China. YamaTough said via Twitter " Pass it on to forensics and win the lawsuit ,".He has offered support to an American man who filed a lawsuit against Symantec Corp by publishing source code from a 2006 version of Norton Utilities, a software program at the heart of the legal dispute. It was not immediately clear how the source code might help the case. A Symantec spokesperson commented on the incident: " We are still gathering information on ...
Data Stealing Malware on Internal Computer of Japan Space Agency

Data Stealing Malware on Internal Computer of Japan Space Agency

Jan 16, 2012
Data Stealing Malware on Internal Computer of  Japan Space Agency Japan Aerospace Exploration Agency (JAXA) announce that their computer has been infected with a virus, leading to a possible leak of data on its H-II Transfer Vehicle (HTV) the craft popularly known as Konotori that hauls cargo for the International Space Station (ISS). JAXA still isn't sure how the virus got on the computer, or who put it there. JAXA said the infection occurred on July 6 last year, when an employee in his 30s involved in the HTV's operation at the Tsukuba Space Center opened an e-mail attachment titled "bonenkai". An identical e-mail was also sent to several coworkers, but the employee accidentally opened the attachment as the sender had the same name as one of his friends. The space agency is working to minimize the damage and prevent further incursions. JAXA is now conducting an investigation into the leak and is checking other computers for viruses, according to the press releas...
Fake Angry Birds Game spreading Malware from Android Market

Fake Angry Birds Game spreading Malware from Android Market

Jan 16, 2012
Fake Angry Birds Game  spreading Malware from Android Market From last week premium rate SMS Trojans surfaced in the Android Market. Google has pulled 22 apps that are masquerading as legitimate versions of popular games like Angry Birds and Cut the Rope. Security researchers have discovered a way to bypass an Android smartphone owner's permissions and access private data stored on their smartphone. Avast Blog explain this as - For example, if someone tried to look for “Cut the rope free”, this malicious application was in the fourth place in the search results. Apps published by the developer Miriada Production may look like well known Android games (Angry birds, Need for speed, World of Goo and others) and users could be easily confused.  The fake apps include "Cut the Rope", "Need for Speed", "Assassins Creed", "Where's My Water? ","Riptide GP", "Great Little War Game", "World of Goo", "Angry Bir...
Zappos a division of Amazon got Hacked

Zappos a division of Amazon got Hacked

Jan 16, 2012
 Zappos a division of Amazon got Hacked A notification mail from Zappos is circulating in Customers that a division of Amazon " Zappos.com " got Hacked by Unknown Hackers. Notification mail indicated that names, email addresses, mailing addresses, and the last four digits of customer's social security numbers have been compromised. Also the databases that contain sensitive billing information, such as credit card numbers, was not accessed by hackers. According to messages from Zappos CEO Tony Hsieh to employees and customers: Zappos are currently working with law enforcement for an investigation.
Security Enhanced (SE) Android Released by National Security Agency (NSA)

Security Enhanced (SE) Android Released by National Security Agency (NSA)

Jan 14, 2012
Security Enhanced (SE) Android Released by National Security Agency (NSA) The National Security Agency (NSA) releases the first version of Android Security Enhanced . The system is designed to minimize the impact of security holes on Android . SE Android project is enabling the use of SELinux in Android in order to limit the damage that can be done by flawed or malicious apps and in order to enforce separation guarantees between apps. However, the scope of the SE Android project is not limited to SELinux.  How can SELinux help Android? Confine privileged daemons. Protect them from misuse. Limit the damage that can be done via them. Sandbox and isolate apps. Strongly separate apps from each other and from the system. Prevent privilege escalation by apps. Provide centralized, analyzable policy. Distinctive features SE Android: Per-file security labeling support for yaffs2, Filesystem images (yaffs2 and ext4) labeled at build time, Kernel permission checks...
URL redirection Vulnerability in Google & Facebook

URL redirection Vulnerability in Google & Facebook

Jan 13, 2012
URL redirection Vulnerability in Google An open redirect is a vulnerability that exists when a script allows redirectionto an external site by directly calling a specific URL in an unfiltered,unmanaged fashion, which could be used to redirect victims to unintended,malicious web sites. A web application accepts a user-controlled input that specifies a link to an external site, and uses that link in a Redirect. A similar vulnerability is reported in Google by " Ucha Gobejishvili ( longrifle0x ) ".  This problem may assist an attacker to conduct phishing attacks, trojan distribution, spammers. Url: https://accounts.google.com/o/oauth2/auth?redirect_uri=http://www.something.com Same vulnerability in Facebook, Discovered by  ZeRtOx from Devitel group : http://www.facebook.com/l.php?h=5AQH8ROsPAQEOTSTw7sgoW1LhviRUBr6iFCcj4C8YmUcC8A&u=www.something.com Impact of Vulnerability  : The user may be redirected to an untrusted page that contains malwar...
Microsoft launching Real Time Hosted Threat Intelligence Feed

Microsoft launching Real Time Hosted Threat Intelligence Feed

Jan 12, 2012
Microsoft launching Real Time Hosted Threat Intelligence Feed Microsoft is to offer a real-time intelligence feed of botnet and e-crime data to public and private sector subscribers, according to security company Kaspersky. Currently, Microsoft is testing a real-time feed to distribute information collected from several sources on major botnets, including Rustock, Waldec and Kelihos networks. Partners would be able to access the information using application program interfaces (APIs) that would be provided free by Microsoft. Data from networks of compromised computers will be among the information on offer to ISPs, CERTs, government agencies and private companies, Kaspersky said . Microsoft will have a lot of data in this system already as anyone who has watched the company’s spectacular attacks on the Kelihos botnet last summer will attest, adding to similar campaigns against Rustock and Waledec, will vouch for. " Companies could use the data to look for opportunistic mal...
The Saudi hacker to Mossad "Don’t waste your time by searching for me"!

The Saudi hacker to Mossad "Don’t waste your time by searching for me"!

Jan 12, 2012
The Saudi hacker to Mossad " Don’t waste your time by searching for me "! In a response to the Israeli hackers, the Saudi hacker xOmar exposed 200 Israeli credit cards and he described the Israeli hackers by idiots and he said that they published invalid credit cards. And he asked Mossad through his website not to search for him, because they won't catch him.  xOmar threatened the Israeli people by exposing 200 credit cards daily, and all of these credit cards are valid. speaking about the latest efforts to locate his place, he said '' I've heard from some idiots saying that I am from Mexico, and another said that I am in Riyadh, and last one said that I am from Dubai " and he said to mossad in a message '' don't waste your time '' The Secretary-General of the Committee on Information and awareness of banking in Saudi banks '' Tal'at hafiz '' have told the " Arabiya.Net " yesterday that Saudi banks ha...
Self-extracting archive (SFX) as Creative Virus Handler

Self-extracting archive (SFX) as Creative Virus Handler

Jan 12, 2012
Self-extracting archive (SFX) as Creative Virus Handler Yesterday I Found and interesting article about " Self-extracting archive (SFX) " on Unremote.org by DarkCoderSc. SFX is a little application that contains compressed files. Creating a customized WinRAR SFX archives is a very easy task, but not all people know how to do it.  It is therefore exactly the same as a .ZIP or .RAR archive. The only difference is that, when you execute it, will automatically extract the files. However, if you add some parameters, you can execute them after extraction or execute a shell command before extraction. So this feature can be used as good virus handler. Let's See how? DarkCoderSc shared his experience with us using a Video Demonstration as shown Below. Start up the WinRAR application; click ‘Browse for folder’ under the ‘File’ menu and browse to the location of the file. With the file highlighted, clicking on the ‘Add’ button will kickoff the archiving process and sele...
Warm up the keyboard, Its time for February The Hacker News Magazine !

Warm up the keyboard, Its time for February The Hacker News Magazine !

Jan 11, 2012
Warm up the keyboard, Its time for February The Hacker News Magazine ! Warm up the keyboard, hack into the internet security of your mind and help us fill the February The Hacker News Magazine with fun, interesting and educational web security info. Our readers love to see what you are up to and what the industry is creating and manufacturing for anyone who turns on their computer and wonders if today is the day they will be hacked into cyber space! Mostly, what they can do about it and how they can protect themselves. Topics of interest include, but are not limited to the following: - New Attack and Defense Techniques - Vulnerability discovery - Small Tactics & Techniques - Big Attacks & Impact - Mobile Hacking - Professional Exploit Development - Security and Hacking Events Around The World - Technical Book Reviews - Security and Hacking Threats - Play with Security Tools - Expert Interview We welcome contributions from readers and hackers like YOU! ...
Stratfor Back Online After Hack with message for Anonymous Hackers

Stratfor Back Online After Hack with message for Anonymous Hackers

Jan 11, 2012
Stratfor Back Online After Hack with message for Anonymous Hacker Security analysis firm Stratfor has relaunched its website after Anonymous hackers brought down its servers and stole thousands of credit card numbers and other personal information belonging to its clients. Hacking collective Anonymous admitted the cyber attack on Christmas Eve and went on to claim that it used the stolen details to make $500,000 in charitable donations to The American Red Cross and Save the Children, as well as other charities.Anonymous eventually released the stolen data to the world, including 75,000 credit card numbers and 860,000 usernames and passwords. Approximately 50,000 of those belong to .mil or .gov email accounts used by the US government. " This was our failure ," Chief Executive George Friedman said in a message to Stratfor's subscribers. " I take responsibility. I deeply regret that this occurred and created hardship for our customers and friends. " Friedma...
US become victim of Indian spy unit, Apple & RIM deny their role !

US become victim of Indian spy unit, Apple & RIM deny their role !

Jan 11, 2012
US become victim of Indian spy unit, Apple & RIM deny their role ! A recently leaked memo reveals that American and Canadian based company’s Apple, Research in Motion and Nokia may have helped the government of India spy on U.S. agencies in order to receive larger shares of the overall Indian cell phone market. Last week, an Indian hacker crew successfully broke into a secured Indian military government network. The group, the Lords of Dharmaraja (who posted up outdated Norton security source code last week) posted documents that infer Apple, Nokia, and Research In Motion gave the Indian government backdoor access to their devices in exchange for mobile phone market rights. The US-China Economic and Security Review Commission (USCC) has asked for an investigation after hackers posted. " We are aware of these reports and have contacted relevant authorities to investigate the matter ," said USCC spokesman Jonathan Weston on Monday. " We are unable to make furthe...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources