-->
#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

The Hacker News | #1 Trusted Source for Cybersecurity News — Index Page

Dutch News site spread Malware on 100000 Computers

Dutch News site spread Malware on 100000 Computers

Mar 16, 2012
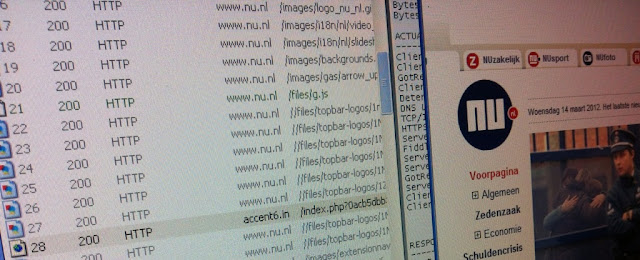
Dutch News site spread Malware on 100000 Computers Dutch popular news site NU.nl appears to be serving Java exploit (drive-by malware) to users of IE. Nu.nl has approximately one hour long served the Javascript code that attempted to provide visitors to the news site with a trojan to infect. The attackers made use of servers in India which an exploit kit was placed. The Ministry of Security and Justice issue a warning for malware yesterday by Nu.nl estimated to have infected 100,000 computers. Erik Loman, developer at security firm SurfRight, made ​​known on Twitter on the front page of the news javascript code ' g.js ' was blocked. The code triggered by Loman a nuclear exploit pack on a web server in India was placed. The exploit script checked the browser and common plugins like Flash and Adobe Reader security hole. If an exploit was found, the server sent the Sinowal-malware, a trojan of Russian origin, which is continuously updated and attempts to steal bank detail...
[POC] Windows RDP Vulnerability Exploit

[POC] Windows RDP Vulnerability Exploit

Mar 16, 2012
[POC] Windows RDP Vulnerability Exploit The vulnerability described by Microsoft as critical is known as MS12-020 or the RDP flaw. The hackers worked quickly on this particular vulnerability and we've already seen attempts to exploit the flaw which exists in a part of Windows called the Remote Desktop Protocol. Proof of concept (POC) exploit of the deadly RDP vulnerability has been shown to trigger blue screens of death on Windows XP and Windows Server 2003 machines. The exploit attacks a RDP (Remote Desktop Protocol) flaw patched by Microsoft on Tuesday. The discovery of proof-of-concept code on a Chinese website less than 72 hours later came as no great surprise. Security firms warned that worse is likely to follow. The vulnerability might easily be exploited to create a worm that spreads automatically between vulnerable computers. Two POC discovered, first POC to emerge was posted briefly on a Chinese website before disappearing. The second, based off the Chinese...
President Assad's hacked emails reveal isolation of Syria's leader

President Assad's hacked emails reveal isolation of Syria's leader

Mar 16, 2012
President Assad 's hacked emails reveal isolation of Syria's leader Asad’s personal email account was hacked by Anonymous hackers few hours ago and The Guardian then acquired over 3,000 documents from hacked email that according to opposition is the personal email of ruling couple Bashar and Asma al-Assad sam@alshahba.com and ak@alshahba.com The newspaper said it got the trove of e-mails from a member of the Syrian opposition whom it does not identify. The documents are said to have been intercepted by members of the Supreme Council of the Revolution between June and early February. According to the Guardian, the e-mails show that Assad regularly received advice from Iran or advisers to Iran about how he should respond to the crisis in his country. He received a memo from his media consultant with advice that was based on " consultations with a good number of people in addition to the media and political adviser for the Iranian ambassador. " The memo advised ...
cyber security

Do You Need to Protect AI, Use AI, or Govern AI? SANS has Mapped All Three.

websiteSANS InstituteAI in Cybersecurity
Free frameworks, guidelines, and role-based AI security training, gathered in one place.
cyber security

Mikko Hyppönen and Enterprise CISOs on What AI-Speed Attacks Actually Change

websitePicus SecurityAI Security / Threat Detection
Join the summit where leading security teams lay out how they prepare for attackers with AI on their side.
Malicious Android application stealing banking credentials

Malicious Android application stealing banking credentials

Mar 15, 2012
Malicious Android application stealing banking credentials A new form of smart Android malware can not only steal your online banking information, but update itself in the future and secretly send contact information stored on your device off to the Bad Guys. Security researchers at McAfee have discovered a malicious Android application capable of grabbing banking passwords from a mobile device without infecting the user’s computer. From a McAfee blog post on the subject, penned by Malware Researcher Carlos Castillo: " To get the fake token, the user must enter the first factor of authentication (used to obtain initial access to the banking account). If this action is not performed, the application shows an error. When the user clicks “Generar” (Generate), the malware shows the fake token (which is in fact a random number) and sends the password to a specific cell phone number along with the device identifiers (IMEI and IMSI). The same information is also sent to one of th...
Stanford University defaced by Indian Hackers

Stanford University defaced by Indian Hackers

Mar 15, 2012
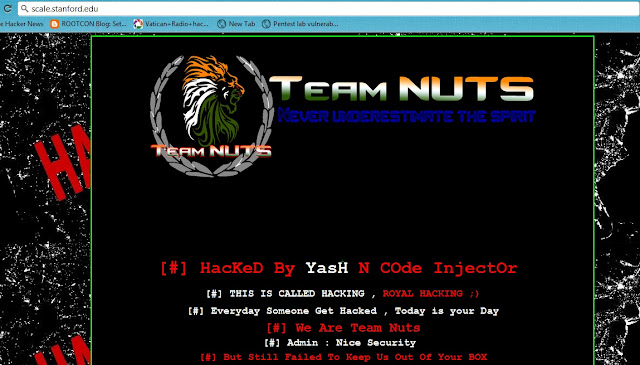
Stanford University defaced by Indian Hackers Stanford University subdomain ( http://scale.stanford.edu/ ) defaced by Indian hackers " Yash " and " C0de Inject0r " from Team Nuts . Stanford is an American private research university located in Stanford, California. Hacker write on page " Everyday Someone Get Hacked , Today is your Day ". " Admin -Good Security ,But Still Failed To Keep Us Out Of Your BOX " They added. Deface page have " Vande Mataram " as background music. Vande Mataram is a patriotic song for Indians. Reason of Defacement is unknown. At time of writing this post, site displaying black colour background with Hackers message on it. Team Nuts Hackers was mostly active last year, you can check their past hacks here .
PS3 hacker Geohot arrested for possession of marijuana

PS3 hacker Geohot arrested for possession of marijuana

Mar 15, 2012
PS3 hacker Geohot arrested for possession of marijuana George 'GeoHot' Hotz, who you might know as "geohot" who made the Sony console's root key available last year, has been banged up for carrying drugs. He was traveling by car with friends on his way to the SXSW conference in Austin to give a talk titled “ The Final Frontier of Reverse Engineering ” when he had to stop at a border patrol checkpoint in Sierra Blanca, Texas. Department of Homeland Security officers were using dogs to decide if a vehicle warranted a search, and Hotz’s car was barked at. Geohot holds a medical marijuana license in California (for those pesky headaches, clearly) and as such, was legally allowed to tote around a confectionary treat bag of THC-infused sweets. Sadly for Geohot, as he may or may not have noticed, he wasn't in California when a sheriff pulled a 1/4 oz. of Mary Jane from the glove box, alongside a pack of chocolates said to contain less than 1/8 oz. of the same Wa...
Carbylamine PHP Encoder - Make PHP files Fully Undetectable from Antivirus

Carbylamine PHP Encoder - Make PHP files Fully Undetectable from Antivirus

Mar 15, 2012
Carbylamine PHP Encoder - Make PHP files Fully Undetectable from Antivirus Carbylamine PHP Encoder is a PHP Encoder for obfuscating/encoding PHP files so that antivirus detection signatures can be bypassed. High Security PHP Encoder Stops unauthorized personnel from reading, modifying and reverse engineering your code. Advance PHP obfuscation makes your code extremely hard to understand. Improves security by preventing hackers from analyzing your source code. Encoding is a process where the PHP source code is converted to an intermediate machine readable format. This format is hard for humans to read and convert back to source code. As a result it protects your code from casual browsing. This means that if people obtain access to your site's code they will not be able to use that for unintended purposes. Obfuscation is a process where code intentionally made very hard to read as source code or as reverse engineered code. This obfuscation is designed to manage risks that st...
Iran Defense Forum users logins compromised and Leaked

Iran Defense Forum users logins compromised and Leaked

Mar 15, 2012
Iran Defense Forum users logins compromised and Leaked Hacker with name " Le0n B3lm0nt " claimed to hack into the Iran Defense Forum website (irandefence.net) and leak user details of all 3,212 members including their usernames, Emails and Passwords.  Iran Defense Forum is an independent forum that is not associated with the Iranian Government, neither it is affiliated with any governmental or regulatory agencies nor related to any political or religious entity. Hacker leak the database on Pastebin Note . Also two days before  Iran hacked BBC Persian TV  The Reason behind this attack is part of a broader attempt by the government to disrupt the BBC’s Persian service. This attack follows various tactics by the Iranian government, such as harassment, arrests, and threats against the relatives of BBC Persia correspondents who still live in Iran, in an effort to force the journalists to quit the Persian news service.
FBI actually leak Stratfor e-mails just to bust Julian Assange?

FBI actually leak Stratfor e-mails just to bust Julian Assange?

Mar 14, 2012
FBI actually leak Stratfor e-mails just to bust Julian Assange ? Internal emails disclosed by Anonymous and WikiLeaks suggest that Stratfor, a private intelligence firm working with the U.S. Justice Department. But The FBI turned a computer hacker to build its case against a group of people it alleges are responsible for a string of audacious attacks that captured the personal details of more than one million people. Hector Monsegur, known as Sabu, leader of the Anonymous affiliated hacking group LulzSec, was arrested by FBI agents in his New York apartment on Monday, June 7, 2011, at 10:15PM. On August 15, Monsegur pleaded guily to several counts of hacking and identity theft.  Seeing that Xavier 'Sabu' Monsegur had apparently been working for the FBI for the last couple of months, it isn't too far-fetched to think that the leaks of the Stratfor e-mails given to Wikileaks by Anonymous was nothing more than a tactic to entrap Wikileaks and build a case against Assange...
Chinese Trojans Gh0stRAT used to attack pro-Tibet organisations

Chinese Trojans Gh0stRAT used to attack pro-Tibet organisations

Mar 14, 2012
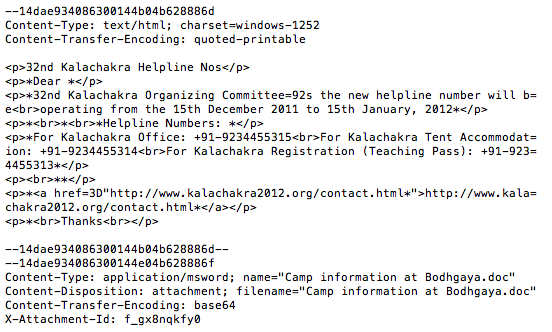
Chinese Trojans Gh0stRAT used to attack pro-Tibet organisations AlienVault has discovered a range of spear phishing attacks taking place against a number of Tibetan organizations apparently from Chinese attackers. The security firm believes that the attacks are originating from the same Chinese group that launched the Nitro attacks last year and and signal a serious escalation into cyberwar from the 'cold war' that has existed between the two countries since the occupation by the Chinese army in 1950. The new attack uses a malicious Word attachment sent by email to organisations including the Central Tibet Administration and International Campaign for Tibet using English-language subject lines promoting a Tibetan religious festival. The attacks were given the name Nitro, and they leveraged Phishing and a PDF exploit to target a vulnerability in Windows (CVE-2010-3333). The malicious payload being delivered in this latest attack is a variant of Gh0stRAT , which exploits a...
'The Consortium' Just Called the Movement a 'SLUT '

'The Consortium' Just Called the Movement a 'SLUT '

Mar 14, 2012
' The Consortium ' Just Called the Movement a ' SLUT ' I’m disappointed. At the pinnacle of one of the greatest and most innovative political movements the world has ever seen, you have the new hackers group named “Consortium” bringing the movement to a new low and quite frankly, an embarrassment. When the world is finally revolting against tyranny, corruption and a disgraceful abuse of human rights, the group Consortium chooses to hack into a porn site and stole Users identity and credit card numbers of men and women, mostly who are serving in the military. ( List of Military Emails , Used in Porn Site to sign up is available in our last related article) May I ask Consortium to what end does this serve? There have been depictions of a sexual nature as old as civilization, such as, the Venus figurines and sexual rock art since prehistoric times. Using the excuse that the site was poorly secured, is no excuse at all for demeaning and demoralizing people using the...
Role of free Hosting in Cyber Crime

Role of free Hosting in Cyber Crime

Mar 14, 2012
Role of free Hosting in Cyber Crime Zscaler experts notice that free hosting and DNS providers abused for hosting Phishing Pages, Spamming, Botnets or Malwares. Many free hosted sites considered as spam. They list " x90x.net " Free hosting Provider which used to host many Facebook Phishing sites. Like Other Blacklisted serviecs ( co.cc, pastehtml.com ) this free hosting can also be blacklisted by Google or Browsers soon.  Few Phishing Pages hosted on x90.net: faceb000k.x90x.net jebemtakra-pisdfa-asdasdsds-ddfs.x90x.net mesnaindustrija-goranovic-m-e-s-n-a.x90x.net dft3.x90x.net/fbcd.html d3xt0pcr3w.x90x.net When you’re on a shared server it’s important to find out if anyone else on your server has been blacklisted for spamming. Why? Because on a shared server you’re IP address and their IP address will be the same, and it does not matter if your domain name is different, you’ll still be blacklisted along with every other person on that server. Not Eve...
Anonymous-OS 0.1 : Anonymous Hackers released their own Operating System

Anonymous-OS 0.1 : Anonymous Hackers released their own Operating System

Mar 14, 2012
Yes! Its true,  Anonymous Hackers released their own Operating System with name " Anonymous-OS" , is Live is an ubuntu-based distribution and created under Ubuntu 11.10 and uses Mate desktop. You can create the LiveUSB with  Unetbootin . Also Read: Top Best Password Managers . Also Read: Deep Web Search Engines . Pre-installed apps on Anonymous-OS: - ParolaPass Password Generator - Find Host IP - Anonymous HOIC - Ddosim - Pyloris - Slowloris - TorsHammer - Sqlmap - Havij - Sql Poison - Admin Finder - John the Ripper - Hash Identifier - Tor - XChat IRC - Pidgin - Vidalia - Polipo - JonDo - i2p - Wireshark - Zenmap …and more Download Anonymous-OS 0.1 Warning : It is not developed by any Genuine Source, can be backdoored OS by any Law enforcement Company or Hacker. Use at your own Risk. Update: Another Live OS for  anonymity available called " Tails ". Which is a live CD or live USB that aims at preserving yo...
Microsoft adds Enhanced Memory Protections in IE10

Microsoft adds Enhanced Memory Protections in IE10

Mar 14, 2012
Microsoft adds Enhanced Memory Protections in IE10 Internet Explorer 10, the next version of the popular browser from Microsoft will incorporate new protections in terms of memory management. French security firm VUPEN has managed to hack Microsoft's Internet Explorer 9 on a fully patched Windows 7 SP1 machine. Internet Explorer 10 introduces significant improvements in memory protections to help make vulnerabilities harder to exploit, helping to keep users safe on the sometimes-hostile Web. These improvements will increase the difficulty and development cost of exploits, making life harder for the bad guys. As VUPEN founder Chaouki Bekrar claims, the memory corruption bug they used to do that is one of many they found, but he also admitted that the new IE 10 will be much harder to break into as Microsoft has added new protection mechanisms. Internet Explorer 10 will include two major new features: HEASLR (High Entropy Address Space Layout Randomization): functionality ad...
Potential Security Risk of Geotagging for the Military

Potential Security Risk of Geotagging for the Military

Mar 14, 2012
Potential Security Risk of Geotagging for the Military Did you know that when you upload photos to the Internet they can tell more about you, then you would want to disclose to a random stranger watching it? Where you live, where you spend time with your kids, when you are at home, and when you are not. How is that? Modern smartphones and cameras can add additional information to digital photos they create - date and time, camera model, and lot's of other information, including GPS coordinates of place where photo has been made. And when you upload such photo to your favorite social network it might either display this info explicitly, or just leave it intact and any user who's watching it can find you on a map. A article posted by  Cheryl Rodewig on United States Army website with title " Geotagging poses security risks ". They explain , The question was posed by Brittany Brown, social media manager of the Online and Social Media Division at the Office of the Ch...
Microsoft Security Bulletin with Remote Desktop Flaws

Microsoft Security Bulletin with Remote Desktop Flaws

Mar 14, 2012
Microsoft Security Bulletin with Remote Desktop Flaws Microsoft has released 6 updates in this month's patch Tuesday, including a patch for a critical hole which the software maker warns could be hit within the next 30 days. Microsoft is warning that there’s a remote, pre-authentication, network-accessible code execution vulnerability in its implementation of the RDP protocol. A remote code execution vulnerability exists in the way that the Remote Desktop Protocol accesses an object in memory that has been improperly initialized or has been deleted. An attacker who successfully exploited this vulnerability could run abitrary code on the target system. An attacker could then install programs; view,change, or delete data; or create new accounts with full user rights, Read More . The vulnerability, which affects all versions of Windows, was privately reported to Microsoft’s via the ZDI vulnerability broker service and the company said it was not yet aware of any attacks in the wild....
BBC Persian TV hacked by Iranian government

BBC Persian TV hacked by Iranian government

Mar 14, 2012
BBC Persian TV hacked by  Iranian government According to BBC News, today Iran hacked BBC Persian TV ( http://www.bbc.co.uk/persian/ ) . This is not the first time the Iranian government has tampered with the BBC’s Persian service, Zdnet Report. The Reason behind this attack is part of a broader attempt by the government to disrupt the BBC’s Persian service. This  attack follows various tactics by the Iranian government, such as harassment, arrests, and threats against the relatives of BBC Persia correspondents who still live in Iran, in an effort to force the journalists to quit the Persian news service. In Addition to this, The BBC’s London office was inundated with automatic phone calls and the company’s satellite feeds into Iran were also jammed, while this only affected owners of illegal satellite dishes, these are of course the only ones that can receive the BBC signal in Iran. The BBC has previously accused Iran of attempting to j...
Tunisian Islamist Website Hacked by Anonymous

Tunisian Islamist Website Hacked by Anonymous

Mar 13, 2012
Tunisian Islamist Website Hacked by Anonymous The Facebook page of Hizb Ettahrir, an Islamist political party that is legally unrecognized in Tunisia, was hacked last night by a Tunisian group claiming affiliation with the international cyber activist collective Anonymous. " We are fighting you... your emails, your bank accounts and transactions will be probed, your hard discs will be copied ," said a man wearing the Guy Fawkes mask that has become a trade mark of Anonymous members. The YouTube video embedded above, in French, was posted a few days ago warning of the attack. The video warned their e-mails, bank accounts, and hard drives will be probed. Furthermore, it said if the Tunisian government won’t stop them, Anonymous will. The video warned, “ We are fighting you… your emails, your bank accounts and transactions will be probed, your hard discs will be copied. If the Tunisian government won’t stop your activities in the weeks to come, Anonymous will . ”   The a...
10 Lessons learnt from Kim Dotcom

10 Lessons learnt from Kim Dotcom

Mar 13, 2012
10 Lessons learnt from Kim Dotcom Article Cross Post from InternetServices. Kim Dotcom, a hacker that was able to take his knowledge and create a site called Megaupload, was recently arrested due to alleged copyright infringement allegations. Even though he was the top dog in the company, he did not commit these crimes alone, and many other key players were also arrested in the wake of these crimes. Unfortunately, while this guy is obviously intelligent, he should have been using those brains for good instead of evil. However it wasn’t all bad, and some good did come from it. Check out 10 things the Internet learned from Kim Dotcom. Cyberlocker technology: This has also been referred to as a ‘cloud storage infrastructure’. Basically this technology allowed you to store files that were too large to e-mail for free on the Internet. For instance, you could upload a big long wedding video and your family could go there to download it at no charge. If they wanted to watch it or downlo...
ServerPro Web Hosting Defaced by Team L0g!cs

ServerPro Web Hosting Defaced by Team L0g!cs

Mar 13, 2012
ServerPro Web Hosting Defaced by Team L0g!cs Web hosting provider ServerPro has been compromised and completely defaced by hacking group named " Team L0g!cs ". ServerPro boasts to have over 200,000 clients over a 10 year stand. Shown Defacement page that showcases information about the hack and the group behind the attack, along with some nice ambient music. The attackers were even nice enough to leave behind a contact email in case you have any questions. While writing this Post , Google showing " Warning,  found malware on the site " on the homepage, as shown below: If we Proceed by ignoring the warning, Visitors can see Deface Page still on the page.
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources