-->
#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

Search results for hacker tiger | Breaking Cybersecurity News | The Hacker News

Exclusive Interview with TiGER-M@TE (Bangladesh Google website Hacker)

Exclusive Interview with TiGER-M@TE (Bangladesh Google website Hacker)

Jan 12, 2011
Update : Latest Hack by TiGER-M@TE :  700,000 sites on Inmotion Hosting Server hacked in one shot On the morning of Saturday, Jan 8, 2011 the biggest news of cyber world was -  Google Bangladesh website (Google.com.bd) Hacked by TiGER-M@TE  . TiGER-M@TE is a Bangladeshi Hacker, He was already connected to "The Hacker News" from last 2-3 months for providing his Hacks News ! Finally we take a small interview of this great Hacker, who make Google Down !! Unix Root          -  Tell us Some Introduction about you. TiGER-M@TE -  Me TiGER-M@TE , nationality Bangladeshi. I've Been hacking since 2007 and I work alone.I like to exploit servers rather than exploiting web application and I use only 0days and private exploits. Unix Root          -  Do you Hack Google on Jan 8, 2011 and Why ? TiGER-M@TE -  I've hacked not only Google but also local domain of Yahoo, Avast, Microsoft, Bing,...
700,000 sites on Inmotion Hosting Server hacked by TiGER-M@TE in one shot !

700,000 sites on Inmotion Hosting Server hacked by TiGER-M@TE in one shot !

Sep 25, 2011
700,000 sites on Inmotion Hosting Server hacked by TiGER-M@TE in one shot ! 700,000 websites hosted on InMotion Hosting network hacked by TiGER-M@TE including  Trinity FM, Blast Magazine. It was not just a server hack, actually whole data center got hacked.   List of all hacked 700000 sites are available here .  Hackers copied over the index.php in many directories (public_html, wp-admin), deleted my images directory and added index.php files where they weren’t needed. 2,00,000 websites hack mirror already Submitted to Zone-H by TiGER-M@TE . We ( The Hacker News ) talk with hacker about the hack, He claim " I hack 700000 websites in one shot, this may be a new world Record. After submitting 200,000 domains,zone-h was going down again and again and became almost unresponsive in the end.so i was unable to submit all websites.so i've listed all domains in attachment .   It was not just a server hack, actually whole data center got hacked. " In Moti...
The Hacker News Hacking Awards : Best of Year 2011

The Hacker News Hacking Awards : Best of Year 2011

Dec 31, 2011
The Hacker News Hacking Awards : Best of Year 2011 2011 has been labeled the " Year of the Hack ” or “ Epic #Fail 2011 ”. Hacking has become much easier over the years, which is why 2011 had a lot of hacking for good and for bad. Hackers are coming up with tools as well as finding new methods for hacking faster then companies can increase their security.  Every year there are always forward advancements in the tools and programs that can be used by the hackers. At the end of year 2011 we decided to give " The Hacker News Awards 2011 ". The Hacker News Awards will be an annual awards ceremony celebrating the achievements and failures of security researchers and the Hacking community. The THN Award is judged by a panel of respected security researchers and Editors at The Hacker News. Year 2011 came to an end following Operation Payback and Antisec, which targeted companies refusing to accept payments to WikiLeak's, such as, Visa and Amazon. Those attacks were carrie...
cyber security

Reco Finds Four in Five Agents Run With Zero IT Oversight

websiteReco AISaaS Security / AI Security
See which agent permissions security teams aren't reviewing, and why it matters now.
cyber security

Build Your Email Security Strategy for the Agentic Era

websiteAdaptive SecurityEmail Security / Cybersecurity
Get the 2026 checklist for defending against AI phishing, compromised accounts, and human error.
Malawi Google ,MSN, Yahoo domains defaced by TiGER-M@TE

Malawi Google ,MSN, Yahoo domains defaced by TiGER-M@TE

Feb 14, 2013
Famous Bangladeshi hacker TiGER-M@TE  known for his big defacements strikes again! This time he teams up with another hacker ' h311 c0d3 ' for another big defacement campaign.  According to mirror records on Zone-H, These hackers managed to deface Malawi Google, Yahoo, MSN, Windows and many more top domains using DNS poisoning attack. During talk with ' The Hacker News ', hackers disclose that they collectively hacked into Malawi (.mw) Domain Registrar website and also target Master and Slave DNS servers. The attackers changed the authoritative DNS records for the affected domains, to point the domain names to their own web server with a deface page hosted on it. All this could have been much worse if the attacker had other goals in his mind rather than defacing famous websites. Imagine how many accounts could have been compromised, if these websites were redirected to a phishing page, instead of a defacement page. At the time of reporting, D...
Google Bangladesh website (Google.com.bd) Hacked by TiGER-M@TE

Google Bangladesh website (Google.com.bd) Hacked by TiGER-M@TE

Jan 09, 2011
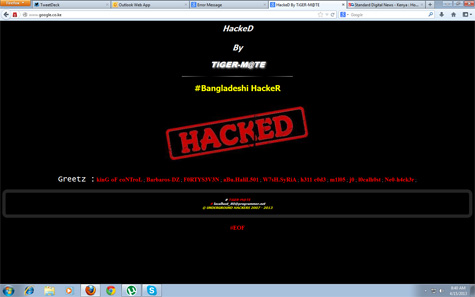
Google Bangladesh website ( Google.com.bd ) Hacked by TiGER-M@TE We just got an anonymous tip that Google’s been ‘hacked’ – sure enough, visitors of the company’s Bangladesh search site (Google.com.bd) see a defaced landing page rather than the usual search site. As far as I can tell, www.google.com.bd functions properly, so whether this really constitutes a ‘hack’ is up for debate. According to Zone-h , Bangladeshi hacker TiGER-M@TE has been quite active with defacements lately, and has targeted some high-profile sites in the past, including the local website for American Express and Airtel (video). See google cache :   http://webcache.googleusercontent.com/search?q=cache:lOhkVDab32MJ:www.google.com.bd/+google+bangladesh&cd=1&hl=en&ct=clnk&gl=in News Source : TiGER-M@TE
Google Kenya domain defaced by TiGER-M@TE

Google Kenya domain defaced by TiGER-M@TE

Apr 15, 2013
On Monday morning, Google has been the victim of a cyber-attack. Defacement attack was launched by Bangladeshi hacker TiGER-M@TE , their Kenyan domain google.co.ke  was defaced, instead the page splayed a black background€™ stamped in red across it. When a user visited the page the hacked screen spiraled in as some foreign music played in the background.  Google is the third most used site in Kenya. TiGER-M@TE has been quite active with defacements lately, and has targeted some high-profile sites in the past.
Cyber Espionage Group Targets Asian Countries With Bitcoin Mining Malware

Cyber Espionage Group Targets Asian Countries With Bitcoin Mining Malware

Feb 07, 2018
Security researchers have discovered a custom-built piece of malware that's wreaking havoc in Asia for past several months and is capable of performing nasty tasks, like password stealing, bitcoin mining, and providing hackers complete remote access to compromised systems. Dubbed Operation PZChao , the attack campaign discovered by the security researchers at Bitdefender have been targeting organizations in the government, technology, education, and telecommunications sectors in Asia and the United States. Researchers believe nature, infrastructure, and payloads, including variants of the Gh0stRAT trojan, used in the PZChao attacks are reminiscent of the notorious Chinese hacker group— Iron Tiger . However, this campaign has evolved its payloads to drop trojan, conduct cyber espionage and mine Bitcoin cryptocurrency. The PZChao campaign is attacking targets across Asia and the U.S. by using similar attack tactics as of Iron Tiger, which, according to the researchers, si...
Fake Google Iranian domain defaced by Algerian Script Kiddies

Fake Google Iranian domain defaced by Algerian Script Kiddies

May 03, 2012
Google got Pwned ? NO Few  Algerian Script Kiddies  try to spread fake rumours that they Hack and Deface the Giant Search engine " Google Iranian " domain  http://www.google.co.ir/  . As the above screenshot shown a Algerian flag on it  and Page Titles : " H4Ck3D By vaga-hacker dz and DR.KIM". As mentioned by hacker, the team include hackers named : " V4Ga-Dz,Dz0ne,DR-KIM King-Dz,BroX0 aghilass elite jrojan password kha&mix wasim -dz " . It is not confirmed that, either these are member from some Anonymous Hackers but they try to use Anonymous Hackers Tag line :  We Dont Forget ,  We Dont Forgive,  Expect Us!   to get some publicity. According to further investigation by " The Hacker News " Technical Team, we found that " google.co.ir " possibly not belongs to GOOGLE because site rank is " 3141379 "  , that means the site should have less than 100 Visitors/Day ap...
Autonomous AI Agents Compromise Thousands of Credentials in Under Six Hours

Autonomous AI Agents Compromise Thousands of Credentials in Under Six Hours

Sep 08, 2026 Artificial Intelligence / Cybercrime
Threat actors are continuing to leverage artificial intelligence (AI) to streamline their operations , with one financially motivated hacking group employing an autonomous, multi-agent attack framework to carry out a large-scale credential harvesting campaign within six hours. Google Threat Intelligence Group (GTIG) said it has observed attackers with diverse motivations targeting proprietary AI models across healthcare, government, and media sectors, exfiltrating API credentials, and co-opting victim cloud environments to sustain unauthorized AI workloads. This highlights growing attacker focus on enterprise AI assets for espionage, extortion, and resource theft. "At this point, we can assume that all threat actors are using AI in some capacity and their operations have benefited," John Hultquist, chief analyst at GTIG, said in a statement shared with The Hacker News. "Like everyone else, we're concerned about the vulnerability problem, but AI is being applie...
MSI Data Breach: Private Code Signing Keys Leaked on the Dark Web

MSI Data Breach: Private Code Signing Keys Leaked on the Dark Web

May 08, 2023 Data Breach / Software Security
The threat actors behind the ransomware attack on Taiwanese PC maker MSI last month have leaked the company's private code signing keys on their dark website. "Confirmed, Intel OEM private key leaked, causing an impact on the entire ecosystem," Alex Matrosov, founder and CEO of firmware security firm Binarly,  said  in a tweet over the weekend. "It appears that Intel Boot Guard may not be effective on certain devices based on the 11th Tiger Lake, 12th Adler Lake, and 13th Raptor Lake." Present in the leaked data are firmware image signing keys associated with 57 PCs and private signing keys for Intel Boot Guard used on 116 MSI products. The Boot Guard keys from MSI are believed to impact several device vendors, including Intel, Lenovo and Supermicro. Intel Boot Guard is a  hardware-based security technology  that's designed to protect computers against executing tampered UEFI firmware. The development comes a month after MSI  fell victim  to a double...
SloppyLemming Targets Pakistan and Bangladesh Governments Using Dual Malware Chains

SloppyLemming Targets Pakistan and Bangladesh Governments Using Dual Malware Chains

Mar 03, 2026 Malware / Phishing
The threat activity cluster known as SloppyLemming has been attributed to a fresh set of attacks targeting government entities and critical infrastructure operators in Pakistan and Bangladesh. The activity, per Arctic Wolf, took place between January 2025 and January 2026. It involves the use of two distinct attack chains to deliver malware families tracked as BurrowShell and a Rust-based keylogger.  "The use of the Rust programming language represents a notable evolution in SloppyLemming’s tooling, as prior reporting documented the actor using only traditional compiled languages and borrowed adversary simulation frameworks such as Cobalt Strike, Havoc, and the custom NekroWire RAT," the cybersecurity company said in a report shared with The Hacker News. SloppyLemming is the moniker assigned to a threat actor that's known to target government, law enforcement, energy, telecommunications, and technology entities in Pakistan, Sri Lanka, Bangladesh, and China since ...
Researchers Detail Bitter APT’s Evolving Tactics as Its Geographic Scope Expands

Researchers Detail Bitter APT’s Evolving Tactics as Its Geographic Scope Expands

Jun 05, 2025 Threat Intelligence / Network Security
The threat actor known as Bitter has been assessed to be a state-backed hacking group that's tasked with gathering intelligence that aligns with the interests of the Indian government. That's according to new findings jointly published by Proofpoint and Threatray in an exhaustive two-part analysis. "Their diverse toolset shows consistent coding patterns across malware families, particularly in system information gathering and string obfuscation," researchers Abdallah Elshinbary, Jonas Wagner, Nick Attfield, and Konstantin Klinger said. Bitter, also known as APT-C-08, APT-Q-37, Hazy Tiger, Orange Yali, T-APT-17, and TA397, has a history of focusing primarily on South Asian entities , with select intrusions also targeting China, Saudi Arabia, and South America. In December 2024, evidence emerged of the threat actor's targeting of Turkey using malware families such as WmRAT and MiyaRAT, indicating a gradual geographical expansion. Stating that Bitter fr...
Bitter APT Targets Turkish Defense Sector with WmRAT and MiyaRAT Malware

Bitter APT Targets Turkish Defense Sector with WmRAT and MiyaRAT Malware

Dec 17, 2024 Cyber Espionage / Malware
A suspected South Asian cyber espionage threat group known as Bitter targeted a Turkish defense sector organization in November 2024 to deliver two C++-malware families tracked as WmRAT and MiyaRAT. "The attack chain used alternate data streams in a RAR archive to deliver a shortcut (LNK) file that created a scheduled task on the target machine to pull down further payloads," Proofpoint researchers Nick Attfield, Konstantin Klinger, Pim Trouerbach, and David Galazin said in a report shared with The Hacker News. The enterprise security company is tracking the threat actor under the name TA397. Known to be active since at least 2013, the adversary is also referred to as APT-C-08, APT-Q-37, Hazy Tiger, and Orange Yali. Prior attacks conducted by the hacking group have targeted entities in China, Pakistan, India, Saudi Arabia, and Bangladesh with malware such as BitterRAT , ArtraDownloader , and ZxxZ, indicating a heavy Asian focus. Bitter has also been linked to cyber...
Someone Hacked Selena Gomez Instagram, Shared Nude Justin Bieber Photos

Someone Hacked Selena Gomez Instagram, Shared Nude Justin Bieber Photos

Aug 30, 2017
The highest followers account on Instagram owned by Selena Gomez has recently been hacked with unknown hackers posting a bunch of nude photographs of her ex-boyfriend Justin Bieber on her account. The latest hack is not part of the ongoing Fappening events affecting a majority of celebrities by targeting their iCloud accounts, rather in the case of Selena, some hacker managed to breach her Instagram account and posted Bieber's photos. Bieber's three full-frontal shots of naked photos were visible to Selena's 125 million Instagram followers for a short duration of time, after which her account was swiftly taken down Monday night. A post from Selena's official Instagram account went up Monday showing 3 pics of Bieber with a caption that read: "LOOK AT THIS N***A LIL SHRIMPY." Selena's team has since re-secured her Instagram account, which was back online minutes after it was taken down, with the photos of Bieber deleted. The Bieber nude images...
DoNot Team Linked to New Tanzeem Android Malware Targeting Intelligence Collection

DoNot Team Linked to New Tanzeem Android Malware Targeting Intelligence Collection

Jan 20, 2025 Android / Malware
The Threat actor known as DoNot Team has been linked to a new Android malware as part of highly targeted cyber attacks. The artifacts in question, named Tanzeem (meaning "organization" in Urdu) and Tanzeem Update, were spotted in October and December 2024 by cybersecurity company Cyfirma. The apps in question have been found to incorporate identical functions, barring minor modifications to the user interface. "Although the app is supposed to function as a chat application, it does not work once installed, shutting down after the necessary permissions are granted," Cyfirma noted in a Friday analysis. "The app's name suggests that it is designed to target specific individuals or groups both inside and outside the country." DoNot Team, also tracked as APT-C-35, Origami Elephant, SECTOR02, and Viceroy Tiger, is a hacking group believed to be of Indian origin, with historical attacks leveraging spear-phishing emails and Android malware families to...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources