-->
#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

The Hacker News | #1 Trusted Source for Cybersecurity News — Index Page

Syrian Electronic Army's own website got hacked by Turkish hacker

Syrian Electronic Army's own website got hacked by Turkish hacker

Jan 14, 2014
Oops.. Hackers got Hacked! The Syrian Electronic Army , who has hacked hundreds of High Profile targets in 2013-14, today they got hacked by a Turkish hacker. Turkguvenligi , a Turkish hacker told The Hacker News that he hacked and defaced the official website of the hacking group SEA ( sea . sy  and  leaks . sea . sy ). SEA Group has taken down many serious targets like Microsoft, Obama & New York Times' twitter accounts & websites in the past, but today their own server got breached. The most common hacking technique used by the SEA Group is Phishing , but the Turkguvenligi hacked then using an exploit known for vulnerabilities in the server or website. At the time of writing this news, the whole website of SEA was down, but our readers can see the defacement mirror on Zone-H . Turkguvenligi tagged SEA in a  tweet , says " hi guys, you have been hacked ": The Syrian Electronic Army group has not commented anything about the hack, b...
Mozilla recommends the use of Open Source Browsers against State Surveillance

Mozilla recommends the use of Open Source Browsers against State Surveillance

Jan 14, 2014
After the revelations from NSA internal documents leaked by Edward Snowden, the world knows the NSA as the Real Techie Gangster of this 21st Century, with the ability to brutally infiltrate every kind of electronic device, the Internet, and global communications.  " It is becoming increasingly difficult to trust the privacy properties of software and services we rely on to use the Internet. Governments, companies, groups and individuals may be surveilling us without our knowledge. " The Inventor of JavaScript & current CTO of Mozilla, Mr. Brendan Eich said in a blog post NSA is not just focused on high-tech exploits, but also specialize in inserting secret backdoor to legitimate products. Its Tailored Access Operations (TAO) unit works with the CIA and FBI to intercept shipments of hardware to insert spyware into the devices. This way NSA is able to keep an eye on all levels of our digital lives, from computing centers to individual computers, and from laptops to mobi...
Cisco released Security advisory for critical Router password reset vulnerability

Cisco released Security advisory for critical Router password reset vulnerability

Jan 14, 2014
In the first week of this year, we have reported about a critical vulnerability found in more than 2000 Routers that allow attackers to reset the admin panel password to defaults. Recently, Cisco has released a security advisory , detailed about the similar vulnerability affecting their three networking products. Cisco has rated the flaw highly critical and marked it as 10.0 on the Common Vulnerability Scoring System (CVSS). A security researcher found a secret service listening on port 32764 TCP, allowed a remote user to send unauthenticated commands to the device and reset the administrative password. Successful exploitation of the vulnerability allows the hacker to execute arbitrary commands on the device with escalated privileges. Vulnerable Cisco products are: WAP4410N Wireless-N Access Point, Cisco WRVS4400N Wireless-N Gigabit Security Router, and the Cisco RVS4000 4-port Gigabit Security. "This vulnerability is due to an undocumented test interface in t...
cyber security

947 Security Pros Told SANS Where the AI Skills Gap Actually Is

websiteSANS InstituteAI in Cybersecurity
Read the 2026 workforce research, then see the AI security training built around those gaps.
cyber security

Mikko Hyppönen and Enterprise CISOs on What AI-Speed Attacks Actually Change

websitePicus SecurityAI Security / Threat Detection
Join the summit where leading security teams lay out how they prepare for attackers with AI on their side.
100Gbps DDoS attack took down Gaming servers with NTP Servers

100Gbps DDoS attack took down Gaming servers with NTP Servers

Jan 14, 2014
The New Year begins with a new form of amplified Distributed Denial of Service (DDoS) Attack, a weapon for attackers to bring down websites and servers. As we have reported two weeks ago that the attackers are abusing the Network Time Protocol (NTP) servers to perform an amplified version of DDoS Attack on various targets across the world. Earlier this week a number of popular Gaming services, including League of Legends, EA.com and Battle.net from Blizzard were taken down by similar DDoS attack . 'Network Time Protocol (NTP)' is a distributed network clock time synchronization protocol that is used to synchronize computer clock times in a network of computers and runs over port 123 UDP. " The attacker sends a small spoofed 8-byte UDP packets are sent to the vulnerable NTP Server that requests a large amount of data (megabytes worth of traffic) be sent to the DDoS's target IP Address.  "Security Researcher, Wang Wai  detailed  in a previous article on ‘The ...
ASUS Wireless router leaves USB Storage Devices vulnerable to remote attackers

ASUS Wireless router leaves USB Storage Devices vulnerable to remote attackers

Jan 13, 2014
In this era of Computers and Smartphones, where we are connected to the Internet every second and use it almost for everything. For an Internet connection, one has to plug a device called Router between the ISP (Internet Service Provider) and device. Some Routers are available with USB option, where you can attach an external Hard Disk that allows files to be stored and retrieved across a computer network. Asus one of the largest IT hardware manufacturer providing these kind of devices by which you can connect to the internet and make your external hard disk available on the Internet as FTP server just by configuring AiDisk utility from the router’s administrator panel.  Many ASUS Routers have this feature available, including models: RT-N66U, RT-N56U, RT-N15U, RT-N65U, RT-AC66U, DSL-N55U and RT-N16. Recently a vulnerability has been noticed by some Sweden users in the ASUS Routers, that allows an attacker to access your Hard Disk remotely from any part ...
How to use PGP encryption with Mozilla Thunderbird Email client

How to use PGP encryption with Mozilla Thunderbird Email client

Jan 13, 2014
In my last article, we have learnt that how to encrypt our Emails using Gnu Privacy Guard . Previously we used Microsoft Outlook as a desktop mail client and a GpgOL plugin to handle encryption decryption of our communication. Since Microsoft is a US-based company, that has to follow all the laws of that contingent. Should we trust Microsoft product to save our e-mail password and data? Obviously NO!  This made me write a new article on the same topic is that today we are going to use an open source mail client i.e.  Mozilla Thunderbird , available for Windows, Mac OS X and Linux. Thunderbird Installation: Initially you need to download the Thunderbird mail client, and install it to make your email communication more secure and private. Open Thunderbird tool and configure your mail account, as shown: Installing and Configuring ENIGMAIL:  In the next step you need to install an Add-on in Thunderbird, called  ENIGMAIL . You can search and install add-on using...
US retailer Neiman Marcus confirmed data breach after TARGET

US retailer Neiman Marcus confirmed data breach after TARGET

Jan 13, 2014
The TARGET Hack was not the only massive Data breach that happened during the last Black Friday, but also other three major US Retailers were also hacked. Recently, Neiman Marcus also confirmed a data breach that involves Credit card theft from its customers during the holiday shopping season, using similar techniques to the one that penetrated Target last month. Neiman Marcus has 79 stores and reported total sales of $1.1 Billion in the Q4 2013. Neiman Marcus revealed that its customers are at risk after hackers breached servers of the company and accessed the payment information of those who visited its stores. The company is working to inform customers whose cards have been used for fraudulent purchases, but differently from the case of retailer Target, the company hasn't provided information on the nature of data leaked and on the number of customer records exposed. Neiman Marcus spokesperson Ginger Reeder announced that the company does not yet know the cause, size or dur...
Samsung KNOX - An Encrypted Virtual Operating system for Android Devices

Samsung KNOX - An Encrypted Virtual Operating system for Android Devices

Jan 12, 2014
Last year Samsung launched a security feature called ' KNOX ' for high-end enterprise mobile devices. It's a nice security addition and free with new Samsung handsets such as the Galaxy Note 3 and Samsung Galaxy S4. Samsung Knox is an application that creates a virtual partition (container) within the normal Android operating system that allows a user to run two different Android systems on a same device, so that you can securely separate your personal and professional activities. KNOX based virtual operating system of your phone requires a password to be accessed and helps you to securely store data that they're especially concerned about, such as personal pictures and video, in protected containers that would be resistant to hacking attempts on stolen devices. You can switch between Knox mode and personal mode using shortcuts in the app tray and notification tray. All the data and applications stored in the KNOX container system are completely isolated from the rest...
Microsoft Official Blog and Twitter account hacked by Syrian Electronic Army

Microsoft Official Blog and Twitter account hacked by Syrian Electronic Army

Jan 12, 2014
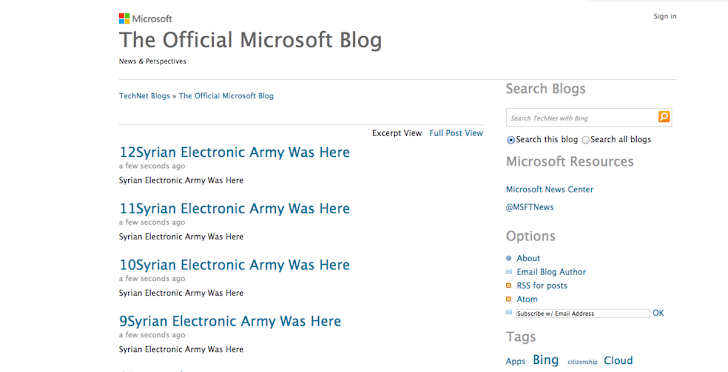
It could be the worst day ever for Microsoft's patch management and Incident response team. A group of pro-Syrian  hackers ' Syrian Electronic Army ' has successfully compromised the official Twitter account of the Microsoft News ( @MSFTNews ), Xbox Support. They also defaced the Microsoft's TechNet blog ( blogs.technet.com ), and posted deface not over the blog. Microsoft says the situation is under control and no customer data was compromised. It seems that hackers have more internal access to the mailer system of the Microsoft, as they shared a screenshots of the internal communications between Microsoft’s Public relations team and Steve Clayton, who is the manager in charge of Microsoft’s corporate media platforms.  Last week, the SEA hacked Skype's blog and official twitter page, to spread the information about the NSA spying i.e. " Hacked by Syrian Electronic Army.. Stop Spying! " and today we have seen similar tweets from the Microsoft's N...
MIT University website defaced by Anonymous hackers in honor of Aaron Swartz

MIT University website defaced by Anonymous hackers in honor of Aaron Swartz

Jan 11, 2014
Today is January 11, 2014 and the last year on the same day a 26-year-old, young hacker, Reddit cofounder and the digital Activist, Aaron H. Swartz committed suicide. He found dead in his Brooklyn, New York apartment, where he had hanged himself. Swartz was indicted by a federal grand jury in July 2011, accused of hacking the MIT JSTOR database and stealing over four million documents with the intent to distribute them. He could have prison for 50 years and $4 million in fines by the Court, but before that he committed suicide in fear. Swartz's father, Robert, later blamed the MIT and the judiciary system for his son's death. On the first Anniversary of Aaron Swartz , today the Anonymous group of hackers defaced the sub-domain of the Massachusetts Institute of Technology (MIT) website ( http://cogen.mit.edu/ ) for about an hour as part of #OPLASTRESORT. Defacement page was titled ' THE DAY WE FIGHT BACK '. The message posted on it, “ Remember The Day We Fight Back,...
Mac OS X Flashback Trojan is still alive, recently infected 22,000 Apple machines

Mac OS X Flashback Trojan is still alive, recently infected 22,000 Apple machines

Jan 11, 2014
The Flashback Trojan, the most sophisticated piece of malware that infected over 600,000 Apple's Macs systems back in April, 2012 is still alive and has infected about 22,000 machines recently, according to the researchers from Intego . For a refresh, Flashback Trojan was first discovered in September 2011, basically a trojan horse that uses a social engineering to trick users into installing a malicious Flash player package. Once installed, the Flashback malware injects a code into that web browser and other applications like Skype to harvest passwords and other information from those program's users. The Trojan targets a known vulnerability in Java on Mac OS X systems. The system gets infected after the user redirects to a compromised website, where a malicious javascript code to load the exploit with Java applets. Then an executable file is saved on the local machine, which is used to download and run malicious code from a remote location. It took Apple months to recogni...
KALI Linux 1.0.6 released; officially added Emergency Self Destruct feature

KALI Linux 1.0.6 released; officially added Emergency Self Destruct feature

Jan 10, 2014
A few days back the developers of one of the most advance open source operating system for penetration testing called ' KALI Linux ' announced that they were planning to include " emergency self-destruction of LUKS ". They patched a utility called cryptsetup,  which introduces a self destruction feature that will allow the Kali user to encrypt the full hard disk to make the data inaccessible in an emergency case by entering a secret password at boot time. Offensive Security has finally announced today the release of the latest version i.e. Kali Linux 1.0.6 with Kernel version 3.12, and also added the Self Destruct feature along with many new penetration testing and hacking tools. The new release also includes an ARM image script, that allow the user to build Kali Linux images for various ARM devices. Some more scripts are also added that enables the user to build their own custom Amazon AMI and Google Compute cloud images. If you already have a Kali ...
Hackers behind TARGET data breach looking for Pro-cracker to decrypt Credit card PINs

Hackers behind TARGET data breach looking for Pro-cracker to decrypt Credit card PINs

Jan 10, 2014
I think you haven’t forgotten the massive data breach occurred at TARGET , the third-largest U.S. Retailer during last Christmas Holidays. People shop during Black Friday sales in which over 40 million Credit & Debit cards were stolen, used to pay for purchases at its 1500 stores nationwide in the U.S. TARGET officially confirmed that the encrypted PINs (personal identification numbers) of payment cards were stolen in the breach, since the stolen pin data were in encrypted form so they were confident that the information was “ Safe and Secure ”, because PIN cannot be decrypted without the right key. The Breach was caused by a malware attack, that allowed the criminals to manipulate Point of Sale (PoS) systems without raising red flags and the card numbers compromised in the breach are now flooding underground forums for sale. Possibly a group of Eastern European cyber criminals who specializes in attacks on merchants and Point-of-Sale terminals either attached a physical de...
Small satellite terminals (VSAT) are vulnerable to Cyber attack

Small satellite terminals (VSAT) are vulnerable to Cyber attack

Jan 10, 2014
The Military Units that rely on very small aperture terminals (VSATs) for satellite communications in remote areas are vulnerable to cyber attack . Researchers from cyber intelligence company IntelCrawler recently identified nearly 3 million VSATs, many of them in the United States, and found that about 10,000 of them could be easily accessed because of configuration weaknesses. " We have scanned the whole IPv4 address space since 2010 and update the results in our Big Data intelligence database, including details about the satellite operator's network ranges, such as INMARSAT, Asia Broadcast Satellite, VSAT internet iDirect, Satellite HUB Pool, and can see some vulnerabilities, " Researchers have warned that terminals having data transmission rate 4kbps to 16 Mbps used in narrow and broadband data transmission are vulnerable to cyber attack. VSATs are most commonly used to transmit narrowband data such as credit card, polling or RFID data or broadband data for VoIP or ...
Rogue software update cause Malware attack on Japanese Nuclear Power Plant

Rogue software update cause Malware attack on Japanese Nuclear Power Plant

Jan 10, 2014
The most critical and worst target of a State-sponsored cyber-attack s could be Hospitals, Dams, Dykes and Nuclear power stations and this may cause military conflicts between countries. According to Japan Today , The Monju nuclear power plant in Tsuruga, Japan was accidentally targeted by a malware on 2nd January, when a worker updated the system to the latest version of the video playback program. Monju Nuclear Plant  is a sodium-cooled fast reactor, was launched in April 1994. It has not been operational for most of the past 20 years, after an accident in which a sodium leak caused a major fire. Employees over there are only left with a regular job of company's paperwork and maintenance. So the malware could have stolen only some sensitive documents, emails, training records and employees' data sheets. The Malware command-and-control server suspected to be from South Korea. The malware itself is not much sophisticated like Stuxnet  o...
Hack or attempt to Hack, you may face 20 years in prison

Hack or attempt to Hack, you may face 20 years in prison

Jan 09, 2014
The Senate Judiciary Committee Chairman ' Patrick Leahy ' reintroduced a revamped version of the " Personal Data Privacy and Security Act " for tough criminal penalties for hackers, that he originally authored in 2005. During last Christmas Holidays, a massive data breach had occurred at the shopping giant  Target,  involving hack of 40 million credit & debit cards, used to pay for purchases at its 1500 stores nationwide in the U.S. Reason: "Target Data Breach? Seriously"?  In a statement, as published below, the Senator wrote: "The recent data breach at Target involving the debit and credit card data of as many as 40 million customers during the Christmas holidays is a reminder that developing a comprehensive national strategy to protect data privacy and cybersecurity remains one of the most challenging and important issues facing our Nation" It seems that the  TARGET Breach  was scheduled, as the best opportunity to ramp u...
Yahoo Mail turns on HTTPS encryption by default to protect users

Yahoo Mail turns on HTTPS encryption by default to protect users

Jan 09, 2014
After the release of NSA Secret spying over Internet communications, I am expecting from all tech companies to make surveillance significantly harder. Yahoo has HTTPS encryption support since late 2012, but users had to opt in to use the feature. Documents revealed by the Edward Snowden shows that the NSA secretly accessed data from several tech giants, including Yahoo, by intercepting unencrypted Internet traffic in a program called Muscular. As promised back in October 2013,  Yahoo  has finally enabled the HTTPS connections by default for their users, that will now automatically encrypts the connections between users and its email service. Jeff Bonforte , senior vice-president of communication products at Yahoo announced  in a blog post: It is 100% encrypted by default and protected with 2,048 bit certificates. This encryption extends to your emails, attachments, contacts, as well as Calendar and Messenger in Mail. HTTPS by default is really a good news fo...
23-year-old Stack overflow vulnerability discovered in X11 Server

23-year-old Stack overflow vulnerability discovered in X11 Server

Jan 09, 2014
X.Org Foundation develops the X-Window System, the standard window system for open source operating systems and devices. Most of the graphical user interfaces for Unix and Linux systems rely on it. At the 30th Chaos Communication Congress (CCC) in Germany, Ilja van Sprundel , a security researcher gave the presentation titled  " X11 Server security with being 'worse than it looks.'". He found more than 120 bugs in a few months. In the presentation, he has presented a 23 year old Stack overflow vulnerability in X11 System that could lead to privilege escalation to root and affects all versions of the X Server back to X11R5. Later today, X.Org Foundation released a security Advisory , states “ A BDF font file containing a longer than expected string could overflow the buffer on the stack. Testing in X servers built with Stack Protector resulted in an immediate crash when reading a user-provided specially crafted font. ” The flaw resides in a file at " libXfo...
Google Chrome to encrypt Stored Cookies by default to enhance browser security

Google Chrome to encrypt Stored Cookies by default to enhance browser security

Jan 09, 2014
When you visit a website, it stores some information on your system through a web browser for later use i.e. Login information, so you do not have to re-login to your website every time you visit the same website on the same browser. Cookies are usually stored as plain text or in the database by the browser and if a computer is accessed by multiple people, one person might scan another’s cookie folder and look for things like passwords or long-life session IDs. If an attacker has the physical access to your system, can steal all your cookies easily to hijack accounts. There are many tools available on the Internet that can make it quicker and easier for an attacker to export all your cookies from the browser. The Google Chrome web browser also saves cookies to a SQLite database file in the user's data folder. One can import that file to SQL Editor software to read all cookies in plain text format. Google's open source project Chromium browser now have a new feat...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources