-->
#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

The Hacker News | #1 Trusted Source for Cybersecurity News — Index Page

Android vulnerability allows hackers to modify apps without breaking signatures

Android vulnerability allows hackers to modify apps without breaking signatures

Jul 04, 2013
Almost all Android handsets are  vulnerable to a  flaw that could allow hackers to seize control of a device to make calls, send texts, or build a mobile botnet , has been uncovered by Bluebox Security .i.e almost 900 million Android devices globally. Or simply, The Flaw allow hackers to modify any legitimate and digitally signed application in order to transform it into a Trojan program that can be used to steal data or take control of the OS. When an application is installed and a sandbox is created for it, Android records the application's digital signature and all subsequent updates for that application need to match its signature in order to verify that they came from the same author and anything without the signature certificate won’t install or run on a user’s device. The vulnerability has existed since at least Android 1.6, which means that it potentially affects any Android device released during the last four years.  Samsung ’s flag...
STOP using Facebook and Google and if you fear US spying

STOP using Facebook and Google and if you fear US spying

Jul 03, 2013
Edward Snowden , a former NSA systems analyst, have revealed the NSA's sweeping data collection of U.S. phone records and some Internet traffic and the programs target foreigners and terrorist suspects mostly overseas. According to the Constitution of all countries, capturing and reading emails or text messages without privileges is illegal . Several Asian and European countries is worried about the US spying. Today a Germany's top security official has warned, " If you are worried about the US spying on you, you need to stop using Google and Facebook. " Internet users who fear their data is being intercepted by U.S. intelligence agencies such as the National Security Agency's should stay away from American websites run through American servers, Interior Minister Hans-Peter Friedrich said. " If these reports are true, it's disgusting. The United States would be better off monitoring its secret services rather than its allies. " Head of t...
Who Governs The Internet and whose property is it?

Who Governs The Internet and whose property is it?

Jul 02, 2013
The recent exposes and revelations by Edward Snowden about the Top Secret Internet Snooping program currently run by US National Security Agency (NSA) have shocked the world. The extent of snooping is even more shocking and what has just stunned the world is the sheer name of top Internet companies who had shared data of all their users and not to forget except Microsoft, all of them namely Google, Facebook, and Apple have longed established themselves as the outright defenders of free speech and Right to Privacy . Many of them are funders and donors of Electronic frontier foundation in US. The recently formed renowned organization defending right to privacy and free speech on Internet . Though much is being written about the extent of snooping, leaked Memos, Obama's Admissions, NSA's careful acceptance of the snooping Program but What bothers me is the stand of Indian Government in this mess. We are reportedly 5th most spied country by US NSA under this program and ...
cyber security

AI Security's Greatest Hits

websiteWizAI Security / Cheat Sheet
Get 7 of the most widely used AI security resources in one pack. Each asset provides practical tools for securing AI apps, models, and agents.
cyber security

Free Assessment: Identify Hidden Internal Risk

websiteBitdefenderAttack Surface / Threat Detection
Discover unnecessary user access to risky tools, shadow IT, based on real user behavior.
Edward Snowden applies for political asylum in Russia

Edward Snowden applies for political asylum in Russia

Jul 01, 2013
A Russian immigration source informed that the US intelligence agency whistleblower Edward Snowden has applied for political asylum in Russia. Few days back, Russian president Vladimir Putin has said Russia would never hand over Mr Snowden over to the United States but that if Snowden wants to stay in Russia he " must stop his work aimed at harming our American partners. " He initially fled from Hawaii to Hong Kong and then to Russia . The US has annulled his passport, and Ecuador, where he had hoped to get asylum, has been coy over offering him shelter. Sarah Harrison is an employee of anti-secrecy group WikiLeaks , who accompanied Mr Snowden on his trip from Hong Kong. " Snowden is not a Russian agent ", Putin said on Monday, and that Russian intelligence services were not working with the fugitive American, who is believed to remain in the transit area at a Moscow airport eight days after arriving from Hong Kong. Speaking at a news confe...
Android based hacking tool to steal passwords from connected computers

Android based hacking tool to steal passwords from connected computers

Jul 01, 2013
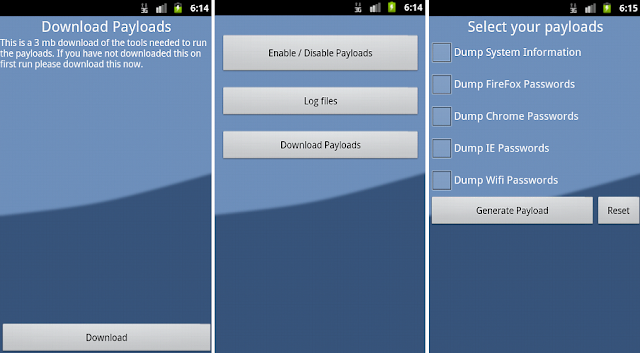
A recently discovered new form of Android malware called  USB Cleaver  can not only infect your smartphone, but also targets your PC to steal sensitive information from it. A hacking tool discovered by analysts at F-Secure, which is capable of stealing information from a connected Windows machine. USBCleaver seems to be designed to facilitate a targeted attack by gathering details that would be helpful in a later infiltration attempt. To use the application, hacker must install an application called USB Cleaver on his Android device. Once executed, the app downloads a ZIP file from a remote server and then unzips the downloaded file to the following location: /mnt/sdcard/usbcleaver/system folder. Tools is design to steal information like  Browser passwords (Firefox, Chrome and IE), PC's Wi-Fi password, The PC's network information etc. When the device is then plugged into a PC, /mnt/sdcard is mounted and, if autorun is enabled, go.bat and t...
NSA can eavesdrop traffic in Real Time, more PRISM slides leaked

NSA can eavesdrop traffic in Real Time, more PRISM slides leaked

Jun 30, 2013
The NSA surveillance program PRISM story was started with four leaked slides from the Washington Post weeks before and today they has revealed four more annotated slides about the NSA operation, along with detailing the various levels of scrutiny from the FBI and NSA that happen before, during and after approved wiretaps take place. According to new slides, The NSA can track real-time events such as email logins or the sending of email, and the logging in or out of a user to a chat service. For live communications, this data goes straight to the NSA's PRINTAURA filtering system, while both the FBI and NSA scan pre-recorded data independently. Two of the new slides detail the data collection process, from the initial input of an agency analyst, to data analysis under several previously-reported analysis tools such as Marina (internet data), Mainway (call records), Nucleon (voice data), and Pinwale (video data). There were 117,675 active surveillance target...
Want to be the Part of History? Just be a part of E-HACK

Want to be the Part of History? Just be a part of E-HACK

Jun 30, 2013
E-HACK is an Information Security Workshop, organized by infySEC . The workshop aims at creating awareness about INFORMATION SECURITY by showing in what all ways information or data can be stolen. Meddle in cyber-warfare, battle with our machine master mind who will throw challenges on web application security, network security, algorithms, reverse engineering and decryption.  The team which cracks the final level will attain the glory of being Winner at our E-HACK Guinness record attempt with tons of prizes waiting. Be simple but not simpler is quote by Einstein, that’s secret of success for E-HACK. Be there to witness the epic battle of brains. It’s planned to be done in a more fun way, through a game called CTF (Capture the Flag) . The only way to know how to protect our information is by knowing the ways in which it can be stolen. So, we’ll be having wide range of discussions on what all ways a HACKER can get his hands on your information and in what all ways you can thwart...
Facebook implementing Advanced HTTPS to minimize NSA Interception

Facebook implementing Advanced HTTPS to minimize NSA Interception

Jun 29, 2013
For years the National Security Agency has successfully shielded its surveillance programs from any real public scrutiny. There have been a lot of news stories about NSA surveillance programs following the leaks of secret documents by Edward Snowden . We have learned that the NSA is collecting millions of Americans’ phone records on a daily basis, that it operates a program called PRISM involving the surveillance of Internet communications, including Email, Facebook posts, and instant messages. The NSA is allowed to record the conversations of non-Americans without a specific warrant for each person monitored, if at least one end of the conversation is outside of the U.S. It is also allowed to record the communications of Americans if they are outside the U.S. and the NSA first gets a warrant for each case. Because Facebook is using outdated Web encryption, which cryptographers say the NSA could penetrate reasonably quickly after intercepting the communicatio...
Stellar Wind Surveillance program under Obama administration

Stellar Wind Surveillance program under Obama administration

Jun 27, 2013
According to secret documents obtained by the Guardian , Obama administration permitted the National Security Agency to surveillance the Emails and  Internet metadata  of all Americans. This secret warrant less surveillance program, collectively known by the NSA code name Stellar Wind , was launched in the end of 2001, to handover the data to the United States government.  Program was officially authorized after the September 11, 2001 terrorist attacks by President George W. Bush and continued under President Barack Obama through 2011. A federal judge at the Fisa court approved this bulk collection order for internet metadata, in every 90 days.  Documents also exposed that all communications with at least one communicant outside the United States or for which no communicant was known to be a citizen of the United States, was recorded by surveillance program . Metadata also details the internet protocol addresses (IP) used by people insi...
Malware threat to Opera users, Trojan signed with a stolen certificate

Malware threat to Opera users, Trojan signed with a stolen certificate

Jun 27, 2013
On June 19, Browser maker Opera admitted that, it discovered an attack on its internal network infrastructure and windows users may have been tricked into installing a Trojan signed with a stolen Opera certificate. " On June 19th we uncovered, halted and contained a targeted attack on our internal network infrastructure. Our systems have been cleaned and there is no evidence of any user data being compromised." "We are working with the relevant authorities to investigate its source and any potential further extent. We will let you know if there are any developments ." said in a post on the Opera Security Blog. Code signing certificates are used to cryptographically verify that a piece of software comes from its purported publisher. It is possible that a few thousand Windows users, who were using Opera between 01.00 and 01.36 UTC on June 19th, may automatically have received and installed the malicious software. Opera plans to roll out a new version of its ...
Hacking Facebook Account with just a text message

Hacking Facebook Account with just a text message

Jun 27, 2013
Can you ever imagine that a single text message is enough to hack any Facebook account without user interaction or without using any other malicious stuff like Trojans, phishing , keylogger etc. ? Today we are going to explain you that how a UK based Security Researcher, " fin1te " is able to hack any Facebook account within a minute by doing one SMS. Because 90% of us are Facebook user too, so we know that there is an option of linking your mobile number with your account, which allows you to receive Facebook account updates via SMS directly to your mobile and also you can login into your account using that linked number rather than your email address or username. According to hacker , the loophole was in phone number linking process, or in technical terms, at file  /ajax/settings/mobile/confirm_phone.php This particular webpage works in background when user submit his phone number and verification code, sent by Facebook to mobile. That submission form h...
Chinese Hackers group 'Comment Crew' is still active and operating under cover

Chinese Hackers group 'Comment Crew' is still active and operating under cover

Jun 27, 2013
Security experts are confident that the Chinese hackers group known as Comment Crew is still operating under cover. “ The Comment Crew is back again ” this is the rumor within Intelligence community, researchers suspect the involvement of the group of hackers in the recent cyber dispute between U.S. and China. Let’s make a step back, last February Mandiant Intelligence firm released an interesting report that revealed an enterprise-scale computer espionage campaign dubbed APT1. Mandiant linked the APT1 attacks, that compromised 141 organizations in seven years, to Chinese military unit called " 61398 ". The is very interesting is that the security firm identified a common pattern for the attacks conducted by Chinese hackers group, it was also able to define a series of key indicators for identifying ongoing APT attacks. Mandiant security firm had monitored the group during last years and report details its operations, it wasn’t the only one FireEye is anoth...
NSA Hacks into 3 major Chinese operators to steal millions of SMS Data

NSA Hacks into 3 major Chinese operators to steal millions of SMS Data

Jun 26, 2013
Once again NSA whistleblower Edward Snowden revealed the truth, that the NSA hacks into China’s mobile operators to steal millions of text messages.  Every month Washington come up with new reports  and accuse other nations, particularly China, for cyber hacking , but the biggest culprit of such crime is in fact the United States. All of this appeared to go relatively well for Washington until revelations emerged of the U.S. National Security Agency's PRISM surveillance program . According to Snowden, U.S. spies had hacked 3 major mobile phone companies in China and a core network to steal text messages of millions of Chinese citizens. Fang Binxing, a President at Beijing University who is considered the chief pioneer of China’s Great Firewall Internet filtering system, has warned in the past that telecom equipment from international companies like Cisco is a threat to China’s national security. As such, it could have allowed NSA operatives to ...
Serious Smishing vulnerability reported in Samsung Galaxy S4

Serious Smishing vulnerability reported in Samsung Galaxy S4

Jun 25, 2013
Serious security vulnerability was recently discovered on the Samsung flagship Galaxy S4 device, claiming that attackers can use it to silently send text messages. Qihoo 360 Technology, an antivirus company based in China, said that this particular vulnerability is related to the " cloud backup " feature of Galaxy S4, which is not properly protected and can be abused. This vulnerability was first discovered on June 17 and already reported the issue to Samsung and the company is already in the process of developing an official update to fix the vulnerability. A rogue mobile application could contain code exploiting the vulnerability to send fraudulent scam text messages ordering premium-rate services, the firm said. By exploiting the vulnerable cloud backup feature, malware could pretend to be the identity of any contact, friend, relative, or organization when faking phishing SMS messages. When these phishing SMS messages are received, users may be tricked i...
Russian President rejected US demand to extradite Edward Snowden

Russian President rejected US demand to extradite Edward Snowden

Jun 25, 2013
Russian President Vladimir Putin bluntly rejected U.S. pleas to extradite National Security Agency Whistleblower Edward Snowden on Tuesday, says since Snowden has not committed a crime in that country, the government will not extradite him back. Putin said, "Mr. Snowden is a free man," Snowden did not cross the Russian border, implying that he is still in the Moscow airport’s transit zone, a sort of diplomatic neutral space. " He arrived as a transit passenger – he didn't need a visa, or other documents, " Putin said. After arriving Sunday on a flight from Hong Kong, Snowden booked a seat on a Havana-bound flight from Moscow on Monday en route to Venezuela and then possible asylum in Ecuador, but he didn't board the plane. " The sooner he selects his final destination point, the better both for us and for himself ," Putin said. White House Press Secretary Jay Carney on Monday urged Russia to ultimately turn him over. " We do ex...
Hack Windows 8.1 to earn $100,000 bounty from Microsoft

Hack Windows 8.1 to earn $100,000 bounty from Microsoft

Jun 25, 2013
If you don’t know yet, Microsoft is offerings up to $100,000 in exchange for finding vulnerabilities and exploits in the upcoming Windows 8.1 Preview which is expected to launch on June 26, the same time as the Microsoft Build Developer Conference. Qualifying submissions with accompanying defensive ideas will also be eligible for a BlueHat Bonus worth up to $50,000. “ These are super challenging to discover and they require a new technique ,” says Mike Reavey, director of Microsoft’s Security Response Center. Windows 8.1 is a major update to Microsoft's brand new operating system Windows 8, and given the serious bounty on offer, Microsoft clearly wants to leave nothing to chance as far as securing the operating system is concerned. " Learning about new exploitation techniques earlier helps Microsoft improve security by leaps, instead of capturing one vulnerability at a time as a traditional bug bounty alone would ," he said. Microsoft’s senior s...
British spy agency has secret access to Global Internet and telephones

British spy agency has secret access to Global Internet and telephones

Jun 25, 2013
The Britain's spy agency GCHQ is running an online eavesdropping operation that has gained secret access to more than 200 optical fiber cables carrying global Internet traffic and telephone calls. The existence of the program has been disclosed in documents shown to the Guardian by the NSA whistleblower Edward Snowden as part of his attempt to expose what he has called the largest program of suspicion less surveillance in human history. Dubbed as , Operation Tempora has been running for around 18 months and allows GCHQ to tap into and store huge volumes of data drawn from fibre-optic cables for up to 30 days. GCHQ is also sharing this sensitive personal information with its American partner, the National Security Agency (NSA). The paper said GCHQ is tapping 200 internet links in total, each with a data rate of 10Gbps, with the agency having the technical capacity to concurrently analyze 46 of these 200 streams of data at a time. That access could ...
Google added malicious apps scanner to Chrome Web Store

Google added malicious apps scanner to Chrome Web Store

Jun 24, 2013
Over the past few years, Cyber Criminals have choose the official Google Chrome Web Store to push malware. In a recent announcement by Google, like Google Play Android apps store, all new apps uploaded to the Chrome Web Store will now also be automatically scanned for malware. Also, Google warned developers that it may take a little longer than before for their app to go live in the store, and  scanning may take from just a few minutes up to an hour.  " Starting today in the Chrome Web Store, you might notice that your item is not broadly available immediately after you publish it. " It is always against the Chrome Web Store Content Policies to distribute malware, if developer still wants to upload something malicious, they should cancel the process and withdraw their program. " This new functionality does not require any action on the part of developers. When you publish an item in the store, the developer dashboard will indicate that your item is i...
California issued cease and desist order against Bitcoin Foundation

California issued cease and desist order against Bitcoin Foundation

Jun 24, 2013
The Bitcoin Foundation has received a cease-and-desist letter from the California Department of Financial Institutions, which oversees banks, credit unions, and other financial organizations operating in the state. Jon Matonis, who is a board member at the Foundation, revealed the letter on Forbes. The agency charges Bitcoin Foundation with allegedly " engaging in the business of money transmission without a license or proper authorization ." If they found to be in violation of the California Financial Code, the foundation could be fined up to $2,500 a day per violation, in addition to criminal prosecution. Convictions under the federal statute are punishable by up to 5 years in prison and a $250,000 fine. Bitcoin doesn't have any kind of central regulatory authority, and trading takes place through Mt. Gox or other exchange floors. So, California’s decision to send a money transmitter warning to the Bitcoin Foundation is a Washington, D.C., nonprofit, makes no sense...
Facebook hack exposes contact Information of 6 Million Users

Facebook hack exposes contact Information of 6 Million Users

Jun 23, 2013
Facebook is alerting its users about a security breach due to a technical glitch, that may have inadvertently exposed the email addresses and telephone numbers of roughly 6 million users. " We recently received a report to our White Hat program regarding a bug that may have allowed some of a person’s contact information (email or phone number) to be accessed by people who either had some contact information about that person or some connection to them, " Facebook said in its announcement. The problem stemmed from a tool that allows users to upload their contact lists or address books to Facebook so that the social network can serve up friend recommendations or invite people to join Facebook. " Because of the bug, some of the information used to make friend recommendations and reduce the number of invitations we send was inadvertently stored in association with people's contact information as part of their account on Facebook, " As a result, ...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources