-->
#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

The Hacker News | #1 Trusted Source for Cybersecurity News — Index Page

Cyber war against Israel have taken very dangerous turn

Cyber war against Israel have taken very dangerous turn

Aug 24, 2011
Cyber war against Israel have taken very dangerous turn The Cyber war between Egypt and Israel have taken very dangerous turn by setting normal internet users as target for botnet attacks. Since week ago some Egyptian hackers attacked so many Israeli's gov communities and organizations on the internet. Israeli prime minister Netanyahus for example . But yet it wasn't very scary attacks level , as it was far from the normal computer users. In Sudden escalation for the attack level , an Egyptian group launched computer worm which infected about 50000 personal computer in Israel and united states. Despite of my virtual machine security level , it was also infected by the same worm. I (Reuben Rayner) didn't notice that am infected till the attackers launched an exe file which viewed message in the full screen mode. Quits of the attackers message  they started with the word "Anti-Zionism"  " If u can see this message this mean that u either from israel o...
Egyptian Consulate in United Kingdom Defaced Cocain hackers

Egyptian Consulate in United Kingdom Defaced Cocain hackers

Aug 24, 2011
Egyptian Consulate in United Kingdom Defaced Cocain hackers Cocain Hacker deface the website of  Egyptian Consulate in United Kingdom. Mirror of hacked site is available on Zone-H .
Knock v1.5 - Subdomain Scanner , allows to bypass wildcard

Knock v1.5 - Subdomain Scanner , allows to bypass wildcard

Aug 24, 2011
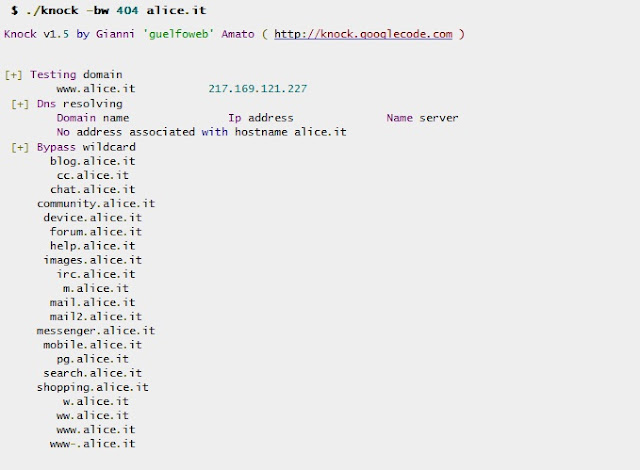
Knock v1.5  - Subdomain Scanner , allows to bypass wildcard Knock is a python script, written by Gianni 'guelfoweb' Amato, designed to enumerate subdomains on a target domain through a wordlist. This program is self contained, doesn't need to be installed in any particular location. All it needs is a recent version of Python 2.xOnly for use the Zone Transfer option (-zt) you must install the module dnspython, otherwise you can do without. If the name server allows zone transfers to occur, all the DNS names and IP addresses hosted by the name server will be returned in human-readable ASCII text. Usage $ python knock.py <option> <url> Rapid Scan Scanning with internal wordlist: $ python knock.py <url> Scanning with external wordlist: $ python knock.py <url> <wordlist> Options -zt Zone Transfer discovery: $ python knock.py -zt <url> -dns Dns resolver: $ python knock.py -dns <url> -wc Wildcard testing: $ python knock.py ...
cyber security

Reco Finds Four in Five Agents Run With Zero IT Oversight

websiteReco AISaaS Security / AI Security
See which agent permissions security teams aren't reviewing, and why it matters now.
cyber security

Build Your Email Security Strategy for the Agentic Era

websiteAdaptive SecurityEmail Security / Cybersecurity
Get the 2026 checklist for defending against AI phishing, compromised accounts, and human error.
Thehacker12 Dumps Logins for 20,000 Customers and U.S. Employees

Thehacker12 Dumps Logins for 20,000 Customers and U.S. Employees

Aug 24, 2011
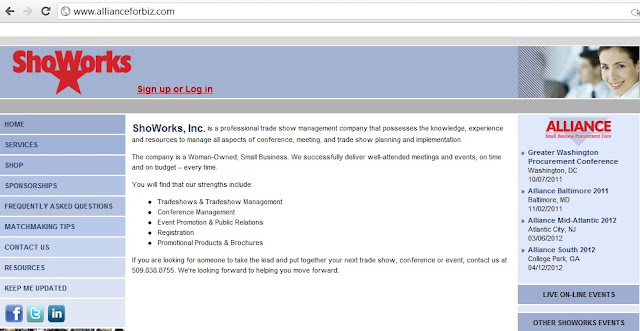
Thehacker12 Dumps Logins for 20,000 Customers and U.S. Employees ThEhAcKeR12  has hacked into an events management company and obtained sensitive information belonging to 20,000 individuals, many of whom were United States government employees or contractors. Hacker posted an Excel spreadsheet containing login credentials and personal information for 20,000 people obtained from allianceforbiz.com . Allianceforbiz.com is a professional trade show management company that manages conferences, meetings and trade shows for customers, according to the company Website. The list has been made public on Pastebin and Mediafire and a message posted on Twitter: " 20,000 email-passwords had been leaked consisting mostly of US Mill Army, Govern. & corporate giants ." The spreadsheet contains usernames, passwords, e-mail addresses. company name. The file also contained 17,668 company names, of which 14,739 were unique, and most had only one e-mail address associated with ...
German Gema website hacked by Anonymous Hackers

German Gema website hacked by Anonymous Hackers

Aug 23, 2011
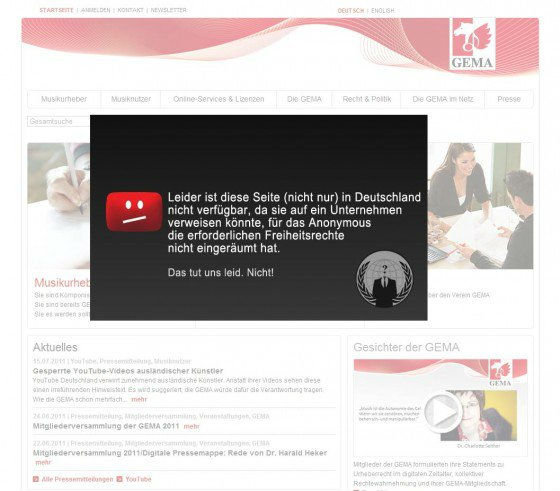
German Gema website hacked by Anonymous Hackers The GEMA website was hacked by Anonymous. Here is a screenshot who was circulating now the whole web presence disappeared. Whoever wants to playback or perform music in public in Germany will become, as a rule by doing this, a customer of GEMA. GEMA (Society for musical performing and mechanical reproduction rights) is a performance rights organization from Germany. It is the only institution in Germany. GEMA represents some 60,000 composers, authors and music publishers and the rights of more than a million copyright owners internationally whose works are used in Germany.
XSS vulnerability in Bing.com Maps by Juan Sacco (runlvl)

XSS vulnerability in Bing.com Maps by Juan Sacco (runlvl)

Aug 23, 2011
XSS vulnerability in Bing.com Maps One of the Security Researcher " Juan Sacco (runlvl) " - Insecurity Research Labs expose the Cross Site vulnerability (XSS) in Bing.com Search Engine. BING.COM is prone to a XSS vulnerability because the application failsto properly perform adequate boundary checks on user-supplied data.An attacker can exploit this issue to execute arbitrary code in thevictim's browser. Details : The reflected XSS vulnerability is a variant of a cross-site scriptingflaw: it occurs when the data provided by the attacker is exectued bythe browser, and then displayed on "normal" pages returned to otherusers in the course of regular browsing, without proper HTML escaping. Aclassic example of this is with online message boards where users areallowed to post HTML formatted messages for other users to read. Vulnerable Link
Android Trojan GingerMaster Uses Gingerbread Root Exploit

Android Trojan GingerMaster Uses Gingerbread Root Exploit

Aug 23, 2011
Android Trojan GingerMaster  Uses Gingerbread Root Exploit As our smartphones become more ubiquitous and more powerful, they need to be protected in much the same way that you would protect your computer. Further to this, a malicious piece of malware has been discovered for devices powered by Android 2.3.3 Gingerbread, giving the hacker the ability to take complete control of the smartphone remotely. According to Assistant Professor Xuxian Jiang from the NCSU Department of Computer Science, the new threat, which his team has dubbed GingerMaster, is the first malware to use the root exploit for Android 2.3. " As this is the first time such malware has been identified, it is not surprising when our experiments show that it can successfully evade the detection of all tested (leading) mobile anti-virus software, " he writes . Once the GingerMaster malware is installed and has root privileges, it then reaches out to a remote command-and-control server and asks for instr...
Automated HTTPS Vulnerability Testing by Qualys SSL Labs

Automated HTTPS Vulnerability Testing by Qualys SSL Labs

Aug 23, 2011
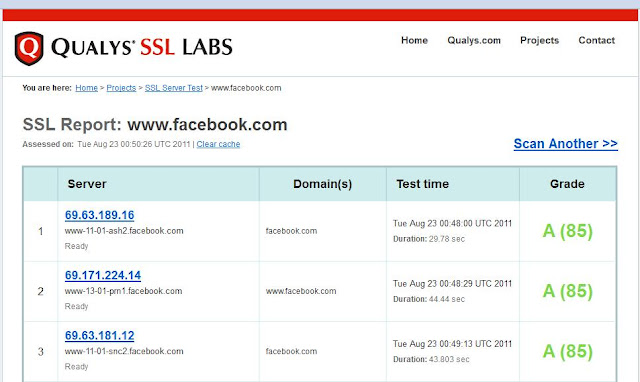
Automated HTTPS Vulnerability Testing by Qualys SSL Labs One of main problem in HTTP protocol is encrypting traffic and verifying data security, securing the web application against any threat is very important especially that if hackers conduct a Man-in the middle attack he can get all users information while data are transferred in a clear text form. HTTPS is a combination of the HTTP with SSL/TLS protocol to provide encrypted communication and secure identification of a network web server. HTTPS connections are often used for payment transactions, social network websites and for sensitive transactions in corporate information systems. HTTPS is a huge step forward for website user’s safety, but it can also be a huge challenge for the security teams, here we need to test our server to be sure that our users and customers are secure for this purposes we can use Qualys SSL server test SSL Server Test is a free online service that performs a deep analysis of the configuration of ...
F-Secure : Chinese Government Launching Online Attacks

F-Secure : Chinese Government Launching Online Attacks

Aug 23, 2011
F-Secure : Chinese Government Launching Online Attacks According to F-Secure Chinese military documentary shows footage of gov't systems launching attacks against US target. China is often blamed for launching online attacks, but the evidence is almost always circumstantial. Many of the targeted espionage Trojans seem to come from China, but we can't actually prove it. However, some new evidence has just surfaced. On 17th of July, a military documentary program titled "Military Technology: Internet Storm is Coming" was published on the Government-run TV channel CCTV 7, Millitary and Agriculture (at military.cntv.cn ). The program seems to be a fairly standard 20-minute TV documentary about the potential and risks of cyber warfare. However, while they are speaking about theory, they actually show camera footage of Chinese government systems launching attacks against a U.S. target. This is highly unusual. The most likely explanation is that this footage ended ...
Turkish government website Hacked by kurdish hacker for bombarding Kurdistan Regions

Turkish government website Hacked by kurdish hacker for bombarding Kurdistan Regions

Aug 23, 2011
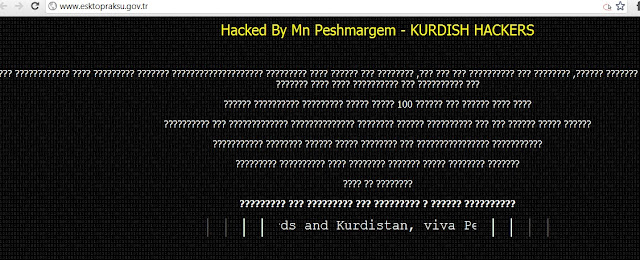
Turkish government website Hacked by kurdish hacker for bombarding Kurdistan Regions Today a kurdish hacker " Mn Peshmargem " deface the website of  Turkish government for protest against the bombarding done by the Turkish Military planes in Kurdistan Regions. Message Posted by Hacker : Fuck racism Turkish, fuck acursed Ataturk, fuck you Turkish the fad ended of the Mongolians wait for your non honored soldiers, that they are embarrassed in front of a Peshmarga like me. If a Kurd die, 100 honorless Turks must go to hell afterwards. You coward Turks are always honorless and lost in front of a Peshmarga like me in the battle fronts. Do you want to hide your honorlessness and cowardice by bombing the mountains in Kurdistan??? Be sure that you must pay back a debt for bombing the mountains in Kurdistan. Fuck the honorless Turks, viva Kurds and Kurdistan, viva Peshmarga.
Kathmandu Metropolitan City website database hacked by T34mT!g3R

Kathmandu Metropolitan City website database hacked by T34mT!g3R

Aug 23, 2011
Kathmandu Metropolitan City website database hacked by  T34mT!g3R Hackers of Team "T34mT!g3R" today expose the SQL injection Vulnerability in Kathmandu Metropolitan City website and extract the database of site. Hacker post the Database info and  Vulnerable  Link   at pastebin .
Uniscan 4.0 vulnerability scanner Released

Uniscan 4.0 vulnerability scanner Released

Aug 23, 2011
Uniscan 4.0 vulnerability scanner Released The Uniscan vulnerability scanner is aimed at information security, which aims at finding vulnerabilities in Web systems and is licensed under the GNU GENERAL PUBLIC LICENSE 3.0 (GPL 3). The Uniscan was developed using the Perl programming language to be easier to work with text, has an easy to use regular expressions and is also multi-threaded. Uniscan Features Identification of system pages through a Web Crawler. Use of threads in the crawler. Control the maximum number of requests the crawler. Control of variation of system pages identified by Web Crawler. Control of file extensions that are ignored. Test of pages found via the GET method. Test the forms found via the POST method. Support for SSL requests (HTTPS). Proxy support. Official Change Log : - Uniscan is now Modularized. - Added directory checks. - Added file checks. - Added PUT method enabled check. - Bug fix in crawler when found ../ directory. - Crawle...
Metropolitan UK Police hacked for #Antisec by CSL Security using SQL injection Vulnerability

Metropolitan UK Police hacked for #Antisec by CSL Security using SQL injection Vulnerability

Aug 22, 2011
Metropolitan UK Police hacked for #Antisec by  CSL Security  using SQL injection Vulnerability One of the Anonymous Hacker " CSL Security " expose SQL Injection Vulnerability  in Metropolitan UK Police website via Twitter . He posted the stuff on Pastebin .  Vulnerable link is also posted by hacker. Where as no data has been published or leaked by Anonymous hackers yet. Yesterday  Danish Government database of 1,000,000 companies private info leaked by Hackers for Antisec Operation. Last week for OpBart - BART Police database hacked by Anonymous also.
Call for Papers from DefCon Chennai (DC602028)

Call for Papers from DefCon Chennai (DC602028)

Aug 22, 2011
Call for Papers from DefCon Chennai (DC602028) Background: We are the Official DEF-CON Chennai Group [DC602028] The Event is taking place on 11th September 2011 at a resort in ECR Road Chennai,India. We will be having a Private conference room for the meet. Regarding Paper Submission We require uniqueness when it comes to Paper submission for DEF-CON Chennai DC602028. Uniqueness as Follows: -> Papers can be on your own research with proof of concept. -> Paper should be of current subject and not more than 1 year old. -> Topics of interest includes everything related to Security. -> Topics related to mobile security or Anroid Security . -> Any new methods of hacking or any 0day/tool disclosure Some of the Sample Topics = New threats faced by Corporate = Threats faced by Normal user from a Malicious person = Mobile security and Mobile Application = Denial of Service attack = Cyber laws = Forensics = Webapp Vulnerabilities = Online Fraud and Soci...
Nokia developer forum Hacked by pr0tect0r AKA mrNRG

Nokia developer forum Hacked by pr0tect0r AKA mrNRG

Aug 22, 2011
Nokia website Hacked by pr0tect0r AKA mrNRG NOKIA , One of the biggest Telecommunications Internet Computer software Company Website hacked by Indian Hacker " pr0tect0r AKA mrNRG " . He Deface the developer.nokia.com  sub-domain of NOKIA and also Redirect Another page to Custom Created Page . Hacker wrote " LOL, Worlds number 1 mobile company but not spending a dime for a server security! FFS patch your security holes otherwise you will be just another antisec victim. No Dumping, No Leaking!! ". Mirror of Hack is also Available on Zone-h . One week before , Pakistan one of the biggest forum  Defence.pk  was also Hacked by pr0tect0r A.K.A. mrNRG in occasion of Independence Day. Nokia Official Statement : During our ongoing investigation of the incident we have discovered that a database table containing developer forum members’ email addresses has been accessed, by exploiting a vulnerability in the bulletin board software that allowed an SQL Injecti...
OWASP Zed Attack Proxy (ZAP) v.1.3.2 Released

OWASP Zed Attack Proxy (ZAP) v.1.3.2 Released

Aug 22, 2011
OWASP Zed Attack Proxy (ZAP) v.1.3.2 Released The OWASP Zed Attack Proxy (ZAP) is an easy to use integrated penetration testing tool for finding vulnerabilities in web applications.It is designed to be used by people with a wide range of security experience and as such is ideal for developers and functional testers who are new to penetration testing as well as being a useful addition to an experienced pen testers toolbox. Some of ZAP's features: Intercepting Proxy Automated scanner Passive scanner Brute Force scanner Spider Fuzzer Port scanner Dynamic SSL certificates API Beanshell integration Download and Details
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources