-->
#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

Search results for tweaks | Breaking Cybersecurity News | The Hacker News

This iPhone Malware infecting Jailbroken Devices Stole 225,000 Apple Accounts

This iPhone Malware infecting Jailbroken Devices Stole 225,000 Apple Accounts

Aug 27, 2015
Jailbreakers Beware! Some shady tweaks that you installed on their jailbroken devices are looking to steal your iCloud login credentials, a report said. The iCloud account details, including email addresses and passwords, of nearly 220,000 jailbreak users have been breached , an online Chinese vulnerability-reporting platform WooYun reported . WooYun is an information security platform where researchers report vulnerabilities and vendors give their feedbacks. Backdoor Privacy Attack The security breach, according to the website, was a result of ' backdoor privacy attack ' caused by the installation of a malicious jailbreak tweak. It appears that Hackers are using a variety of " built-in backdoors " that could be numerous of malicious jailbreak tweaks in an effort to acquire victim's iCloud account information. Once installed, these malicious tweaks transferred the iCloud login details of the jailbreak users to an unknown remote se...
Cydia Repository by BigBoss Hacked, All Paid and Free Tweaks Stolen

Cydia Repository by BigBoss Hacked, All Paid and Free Tweaks Stolen

Jul 21, 2014
BigBoss repository, one of the biggest and most popular repositories for jailbreak tweaks in Cydia , has reportedly been hacked by either an individual or a group of hackers. Cydia is a software application for iOS that enables a user to find and install software packages on jailbroken iOS Apple devices such as the iPhone, the iPod Touch, and the iPad. Most of the software packages available through Cydia are free, but some require purchasing. The BigBoss repository is default repository in jailbroken iOS devices and has long been one of Cydia’s biggest and best, but it may have just been targeted by cybercriminals. The hackers, who go by the name “Kim Jong-Cracks”, managed to gain access to all packages , including all paid as well as free, and made their own repository available with all BigBoss repository applications for free. “ The other post more than likely broke rule 1 because it linked the site directly. To anyone that didn't see the post the BigBoss rep...
DarkGate Malware Exploited Recently Patched Microsoft Flaw in Zero-Day Attack

DarkGate Malware Exploited Recently Patched Microsoft Flaw in Zero-Day Attack

Mar 14, 2024 Malware / Cyber Attack
A DarkGate malware campaign observed in mid-January 2024 leveraged a recently patched security flaw in Microsoft Windows as a zero-day using bogus software installers. “During this campaign, users were lured using PDFs that contained Google DoubleClick Digital Marketing (DDM) open redirects that led unsuspecting victims to compromised sites hosting the Microsoft Windows SmartScreen bypass CVE-2024-21412 that led to malicious Microsoft (.MSI) installers,” Trend Micro  said . CVE-2024-21412 (CVSS score: 8.1) concerns an internet shortcut files security feature bypass vulnerability that permits an unauthenticated attacker to circumvent SmartScreen protections by tricking a victim into clicking on a specially crafted file. It was  fixed  by Microsoft as part of its Patch Tuesday updates for February 2024, but not before it was weaponized by a threat actor called  Water Hydra  (aka DarkCasino) to deliver the DarkMe malware in attacks targeting financial instituti...
cyber security

The AI for Security Virtual Summit (Oct 20)

websiteWizAI for Security
Join Figma, Perplexity, and Wiz to learn how to monitor rogue agents, automate triage, and secure code. Save your spot!
cyber security

New: Analyzing 2026's Most Prevalent Browser Attack Techniques

websitePush SecurityBrowser Security / Phishing
4 in 5 ClickFix attacks are via search engines. 30+ device code phish kits this year. Get the latest analysis.
Google Search Algorithm to Demote Piracy Sites In Search Results

Google Search Algorithm to Demote Piracy Sites In Search Results

Oct 22, 2014
The Search Engine giant is not going to spare the Pirated content providing sites . Google is ready to fulfill its commitment to downgrade the search rankings of ‘ notorious ’ piracy sites globally that often rank above legal and commercial sites. Google and the Copyright holders are, to some extent, enemies for years, but in Google's ongoing anti-piracy efforts, the company will fight copyright infringement and assure rights holders that their contents will be appeared at the top of its search results and that the search made up only a small portion of pirate traffic. DOWNGRADE PIRATED SITES Google is preparing major tweaks to its search engine, which you’ll be able to see this week, to ensure that the ‘notorious’ piracy sites that enable the downloading or streaming of pirated contents are out of search results when people search for music, movies and other copyrighted content. The announcement of the algorithm update came as Google updated “ How Google Fights ...
'AdThief' Chinese Malware Infects Over 75,000 Jailbroken iOS devices

'AdThief' Chinese Malware Infects Over 75,000 Jailbroken iOS devices

Aug 20, 2014
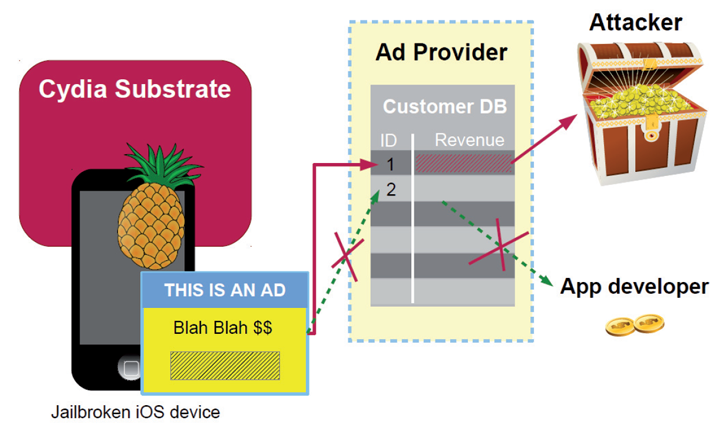
If you have jailbroken your iPhone, iPad, or iPod touch and have downloaded pirated tweaks from pirated repositories, then you may be infected by “AdThief” malware, a Chinese malware that is now installed on more than 75,000 iPhone devices. According to a recent research paper published on Virus Bulletin by the Security Researcher Axelle Apvrille , the malware, also known as " spad ," was first discovered by security researcher Claud Xiao in March this year. Till now, AdThief aka Spad malware has hijacked an estimated 22 million advertisements and stealing revenue from developers on the iOS jailbreak community, Axelle Apvrille says. The malware allegedly infects iOS jailbroken devices by disguising itself as Cydia Substrate extension, presents only on jailbroken Apple devices, when a malware infected Cydia package is downloaded and installed by the unsuspecting user. Once installed, the malware modifies certain advertisements displayed on your iOS devi...
Iranian Hackers Launch ‘SpearSpecter’ Spy Operation on Defense & Government Targets

Iranian Hackers Launch ‘SpearSpecter’ Spy Operation on Defense & Government Targets

Nov 14, 2025 Malware / Threat Intelligence
The Iranian state-sponsored threat actor known as APT42 has been observed targeting individuals and organizations that are of interest to the Islamic Revolutionary Guard Corps (IRGC) as part of a new espionage-focused campaign. The activity, detected in early September 2025 and assessed to be ongoing, has been codenamed  SpearSpecter by the Israel National Digital Agency (INDA). "The campaign has systematically targeted high-value senior defense and government officials using personalized social engineering tactics," INDA researchers Shimi Cohen, Adi Pick, Idan Beit-Yosef, Hila David, and Yaniv Goldman said. "These include inviting targets to prestigious conferences or arranging significant meetings." What's notable about the effort is that it also extends to the targets' family members, creating a broader attack surface that exerts more pressure on the primary targets. APT42 was first publicly documented in late 2022 by Google Mandiant, detailing its...
Malicious PyPI, npm, and Ruby Packages Exposed in Ongoing Open-Source Supply Chain Attacks

Malicious PyPI, npm, and Ruby Packages Exposed in Ongoing Open-Source Supply Chain Attacks

Jun 04, 2025 Supply Chain Attack / DevOps
Several malicious packages have been uncovered across the npm, Python, and Ruby package repositories that drain funds from cryptocurrency wallets, erase entire codebases after installation, and exfiltrate Telegram API tokens, once again demonstrating the variety of supply chain threats lurking in open-source ecosystems. The findings come from multiple reports published by Checkmarx, ReversingLabs, Safety, and Socket in recent weeks. The list of identified packages across these platforms are listed below - Socket noted that the two malicious gems were published by a threat actor under the aliases Bùi nam, buidanhnam, and si_mobile merely days after Vietnam ordered a nationwide ban on the Telegram messaging app late last month for allegedly not cooperating with the government to tackle illicit activities related to fraud, drug trafficking, and terrorism. "These gems silently exfiltrate all data sent to the Telegram API by redirecting traffic through a command-and-control (C2...
New TrojPix Attack Leaks Data From Air-Gapped Systems via Video Cable Emissions

New TrojPix Attack Leaks Data From Air-Gapped Systems via Video Cable Emissions

Jul 06, 2026 Cyber Espionage / Endpoint Security
Researchers at  Shandong University  have shown a fast new way to pull data off computers that are cut off from every network. The technique, called  TrojPix , tweaks on-screen pixels in ways the eye cannot see, so that the video cable carrying them radiates a faint radio signal a nearby receiver can decode. But TrojPix works only once malware is already on the target machine, so it is a way for stolen data to get out, not a way in. In the researchers' tests, TrojPix hit a peak throughput of 8.1 Mbps and reached as far as 208 meters, the two measured separately rather than together. Most air-gap covert channels crawl along at bits or kilobits per second; at 8.1 megabits, roughly a megabyte a second, TrojPix could move a 100 MB file in under two minutes. That turns the threat from leaking a password into moving whole files while the monitor looks switched off. Real-world range is another matter: a receiver still has to fight through walls, shielding, and noise. Th...
The Hidden Cost of Recurring Credential Incidents

The Hidden Cost of Recurring Credential Incidents

Apr 07, 2026 Cybersecurity / Identity Security
When talking about credential security, the focus usually lands on breach prevention. This makes sense when IBM’s 2025 Cost of a Data Breach Report puts the average cost of a breach at $4.4 million. Avoiding even one major incident is enough to justify most security investments, but that headline figure obscures the more persistent problems caused by recurring credential incidents. Account lockouts and compromised credentials don’t make the news. They show up as repeated helpdesk tickets, interrupted workflows, and time pulled away from higher-value work. Individually, each incident seems minor, but collectively they place a constant burden on IT teams and the wider business. The real cost doesn’t just sit in the breach you might prevent, but in the day-to-day disruption you’re already dealing with. Repeated incidents equal repeated costs If an organization finds itself suffering from credential-based attacks or repeated account c...
How to Protect Your SaaS from Bot Attacks with SafeLine WAF

How to Protect Your SaaS from Bot Attacks with SafeLine WAF

Mar 02, 2026 Application Security / DevOps
Most SaaS teams remember the day their user traffic started growing fast. Few notice the day bots started targeting them. On paper, everything looks great: more sign-ups, more sessions, more API calls. But in reality, something feels off: Sign-ups increase, but users aren’t activating. Server costs rise faster than revenue. Logs are filled with repeated requests from strange user agents. If this sounds familiar, it’s not just a sign of popularity. Your app is under constant automated attack, even if no ransom emails have arrived. Your load balancer sees traffic. Your product team sees “growth”. Your database sees pain. This is where a WAF like SafeLine fits in. SafeLine is a self-hosted web application firewall (WAF) that sits in front of your app and inspects every HTTP request before it reaches your code.  It does not just look for broken packets or known bad IPs. It watches how traffic behaves: what it sends, how fast, in what patterns, and against which endpoints. ...
Google Fixing the little things !

Google Fixing the little things !

Apr 07, 2011
Google Fixing the little things ! Ever since I joined the Gmail team, my friends have been eager to tell me, " I love Gmail ! Except for this one thing... " And every day, Gmail users share their "one thing" that would make Gmail better for them through our  suggestions page . While we enjoy creating new solutions to old problems with features like  Priority Inbox , those little annoyances and missing pieces are important, too. Recently, we've rolled out several small tweaks to Gmail to show it a little extra love.   Here’s a rundown: Auto-save contacts setting : Most people like that Gmail automatically saves every email address you send messages to; it can help recover forgotten addresses of former teachers, bosses, and people you contacted once but never thought you'd need to contact again. For some people, though, this feature can cause too much  contacts clutter . Today, we're rolling out a new setting to let you turn off the auto-save option. Yo...
ThreatsDay Bulletin: GhostAd Drain, macOS Attacks, Proxy Botnets, Cloud Exploits, and 12+ Stories

ThreatsDay Bulletin: GhostAd Drain, macOS Attacks, Proxy Botnets, Cloud Exploits, and 12+ Stories

Jan 01, 2026 Cybersecurity / Hacking News
The first ThreatsDay Bulletin of 2026 lands on a day that already feels symbolic — new year, new breaches, new tricks. If the past twelve months taught defenders anything, it’s that threat actors don’t pause for holidays or resolutions. They just evolve faster. This week’s round-up shows how subtle shifts in behavior, from code tweaks to job scams, are rewriting what “cybercrime” looks like in practice. Across the landscape, big players are being tested, familiar threats are mutating, and smaller stories are quietly signaling bigger patterns ahead. The trend isn’t about one big breach anymore; it’s about many small openings that attackers exploit with precision. The pace of exploitation, deception, and persistence hasn’t slowed; it’s only become more calculated. Each update in this edition highlights how the line between normal operations and compromise is getting thinner by the week. Here’s a sharp look at what’s moving beneath the surface of the cybersecurity world as 2026 begin...
Hurray! Unlocking Your Cell Phone is Officially Legal Again

Hurray! Unlocking Your Cell Phone is Officially Legal Again

Aug 02, 2014
President Barack Obama signed a bill into law Friday that aims to make it legal for consumers to “unlock” their cell phones in order to change their cell phone service providers without paying for a new phone. The bill is known as the Unlocking Consumer Choice and Wireless Competition Act , which orders the U.S. Library of Congress (LoC) to allow cell phone owners to " unlock " their devices – typically “ locked ,” to a specific service provider like AT&T or Verizon – for its use on other networks without the permission of their service provider. " As long as their phone is compatible and they have complied with their contracts, consumers will now be able to enjoy the freedom of taking their mobile service - and a phone they already own - to the carrier that best fits their needs, " the White House said in a statement . UNLOCKING Vs. JAILBREAKING Unlocking means the device can only access the network of a particular telecomm, like AT&T or Veriz...
How to Remove KeyRaider Malware that Hacked Over 225,000 iOS Devices

How to Remove KeyRaider Malware that Hacked Over 225,000 iOS Devices

Sep 07, 2015
Jailbreaking your device may have got you the best of apps but after reading this you will know what a high price you could have to pay for the jailbreak. Read on… A malware named ‘ KeyRaider ’ has supposedly stolen user credentials of approximately 225K iPhone users. It has been given this name as it raids victims’ username and passwords, private keys and certificates. Figures say that KeyRaider malware has affected a large number of users in China and worldwide 17 more countries. Also, the origin of malware is suspected to be in China, as said in investigations conducted by Palo Alto Networks for reporting any suspicious tweaks on iPhones. Users falling prey to KeyRaider may be the victims of: Ransomware Data Theft DDoS Attacks Malware is targeting jailbroken phones and when in action, it captures Apple ID of the users and make transactions using it. The researchers say that it is spreading with the help of Cydia app repositories that are popular amo...
Armitage Update : Graphical cyber attack management tool for Metasploit

Armitage Update : Graphical cyber attack management tool for Metasploit

Feb 15, 2012
Armitage Update : Graphical cyber attack management tool for Metasploit Armitage is a graphical cyber attack management tool for Metasploit that visualizes your targets, recommends exploits, and exposes the advanced capabilities of the framework. Armitage aims to make Metasploit usable for security practitioners who understand hacking but don’t use Metasploit every day. If you want to learn Metasploit and grow into the advanced features, Armitage can help you. Armitage Changelog 14/Feb/12 - Added ports 5631 (pc anywhere) and 902 (vmauthd) to the MSF Scans feature. - Several cosmetic tweaks to the spacing in Armitage tables. - Moved table render code from Sleep to Java to avoid potential lock conflicts - Added support for vba-exe payload output type. - Payload generation dialog now sets more appropriate default options for the vba output type when it is selected. - Meterp command shell "read more stuff?" heuristic now accounts for Yes/No/All - Fixed ExitOnSession ...
China-Linked Hackers Adopt Two-Stage Infection Tactic to Deploy Deuterbear RAT

China-Linked Hackers Adopt Two-Stage Infection Tactic to Deploy Deuterbear RAT

May 17, 2024 Malware / Artificial Intelligence
Cybersecurity researchers have shed more light on a remote access trojan (RAT) known as Deuterbear used by the China-linked  BlackTech  hacking group as part of a cyber espionage campaign targeting the Asia-Pacific region this year. "Deuterbear, while similar to Waterbear in many ways, shows advancements in capabilities such as including support for shellcode plugins, avoiding handshakes for RAT operation, and using HTTPS for C&C communication," Trend Micro researchers Pierre Lee and Cyris Tseng  said  in a new analysis. "Comparing the two malware variants, Deuterbear uses a shellcode format, possesses anti-memory scanning, and shares a traffic key with its downloader unlike Waterbear." BlackTech , active since at least 2007, is also tracked by the broader cybersecurity community under the monikers Circuit Panda, Earth Hundun, HUAPI, Manga Taurus, Palmerworm, Red Djinn, and Temp.Overboard. Cyber attacks orchestrated by the group have long involved the depl...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources