-->
#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

The Hacker News | #1 Trusted Source for Cybersecurity News — Index Page

Windows Error Crash Reports or Treasure of Zero-Day vulnerabilities for NSA?

Windows Error Crash Reports or Treasure of Zero-Day vulnerabilities for NSA?

Jan 03, 2014
I am sure that you all have been familiar with the above shown annoying Window Operating System error messages that many times pop ups on your screen while working on the system in case of process failure i.e. " The system has recovered from a serious error. A log of this error has been created. Please tell Microsoft about this problem " The message that prompts ask the user to report the problem to Microsoft followed by the options to Send an error report or Not send . Most of the time Gentle users like you and me used to submit these error reports to aware the Microsoft about the problem. But What if these crash reports can be abused to identify the vulnerabilities of your system for Spying? NSA is intercepting wide range of Internet Traffic including many Encrypted connections and naturally unencrypted also and surprisingly, by default Microsoft encrypts its reports, but the messages are transmitted unencrypted or over standard HTTP connections to watson.microsoft.c...
Abusing Network Time Protocol (NTP) to perform massive Reflection DDoS attack

Abusing Network Time Protocol (NTP) to perform massive Reflection DDoS attack

Jan 03, 2014
In 2013, we have seen a significant increase in the use of a specific distributed denial of service (DDoS) methodology known as Distributed Reflection Denial of Service attacks (DrDoS). Open and misconfigured DNS (Domain Name System) can be used by anyone to resolve domain names to IP addresses are increasingly abused to launch powerful DDoS attacks. But not only the DNS servers, Security Researchers at Symantec  have spotted Network Time Protocol (NTP) reflection DDoS attacks being launched by cyber criminals during the Christmas Holidays. ' Network Time Protocol (NTP) ' is a distributed network clock time synchronization protocol that is used to synchronize computer clock times in a network of computers and runs over port 123 UDP. NTP is one of those set-it-and-forget-it protocols that is configured once and most network administrators don't worry about it after that. Unfortunately, that means it is also not a service that is upgraded often, leaving it vulnerable to th...
Hackers stole money from European ATMs using Malware-loaded USB Device

Hackers stole money from European ATMs using Malware-loaded USB Device

Jan 02, 2014
Hacking ATM Machines is nothing new, but it seems that instead of relying on ATM skimmers now some smart hackers in Europe are reportedly targeting ATM Machines using Malware -loaded USB drives to steal money. Most of the world’s ATMs are running on Windows XP operating system, which is highly vulnerable to Malware attacks. Just like your Desktop Laptops, some ATMs also have USB sockets, which is hidden behind the ATM’s fascia. The German security researchers who discovered the hack detailed their findings at the Chaos Computing Congress in Hamburg, Germany recently. They said that the thieves cut holes in the fascia to access a USB port and then uploaded malware to the machines. The malware creates a backdoor that can be accessed on the front panel. " These researchers explained that the malware allowed the thieves to create a unique interface on the ATMs by typing in a 12-digit code. This interface allowed for withdrawal and also showed the criminals the amount of money and e...
cyber security

947 Security Pros Told SANS Where the AI Skills Gap Actually Is

websiteSANS InstituteAI in Cybersecurity
Read the 2026 workforce research, then see the AI security training built around those gaps.
cyber security

Mikko Hyppönen and Enterprise CISOs on What AI-Speed Attacks Actually Change

websitePicus SecurityAI Security / Threat Detection
Join the summit where leading security teams lay out how they prepare for attackers with AI on their side.
DROPOUTJEEP: NSA's Secret program to access any Apple iPhone, including microphone & camera

DROPOUTJEEP: NSA's Secret program to access any Apple iPhone, including microphone & camera

Jan 02, 2014
In the era of Smartphones, Apple’s iPhone is the most popular device that exists, which itself gives the reason to target it. According to leaked documents shared by Security researcher  Jacob Appelbaum , a secret NSA program code named DROPOUTJEEP has nearly total access to the Apple’s iPhones, which uses “ modular mission applications to provide specific SIGINT functionality. ” While giving the presentation at the Chaos Communications Congress (30C3) in Hamburg, Germany on Monday, Appelbaum revealed that NSA reportedly sniffing out every last bit of data from your iPhone. DROPOUTJEEP is a software implant for the Apple iPhone that utilizes modular mission applications to provide specific SIGINT functionality. This functionality includes the ability to remotely push/pull files from the device. SMS retrieval, contact list retrieval, voicemail, geolocation, hot mic, camera capture, cell tower location, etc. Command, control and data exfiltration can occur over SMS messa...
Firmware vulnerability allows man-in-the-middle attack using SD Memory cards

Firmware vulnerability allows man-in-the-middle attack using SD Memory cards

Jan 02, 2014
How is it possible to exploit SD Card, USB stick and other mobile devices for hacking? Another interesting hack was presented at the Chaos Computer Congress (30C3), in Hamburg, Germany. The researchers demonstrated how it is possible to hack the microcontroller inside every SD and MicroSD flash cards that allow arbitrary code execution and can be used to perform a man in the middle attack . The Hardware Hackers  Andrew “ bunnie ” Huang and Sean “xobs”  described the exploitation method on their blog post ," it also enables the possibility for hardware enthusiasts to gain access to a very cheap and ubiquitous source of microcontrollers. " It seems that to reduce SD cards price and increase their storage capability, engineers have to consider a form of internal entropy that could affect data integrity on every Flash drive. Almost every NAND flash memory is affected by defects and presents problems like electron leakage between adjacent cells. " Flash memory is really ...
Skype's Official Twitter, Facebook and Blog Hacked by Syrian Electronic Army

Skype's Official Twitter, Facebook and Blog Hacked by Syrian Electronic Army

Jan 02, 2014
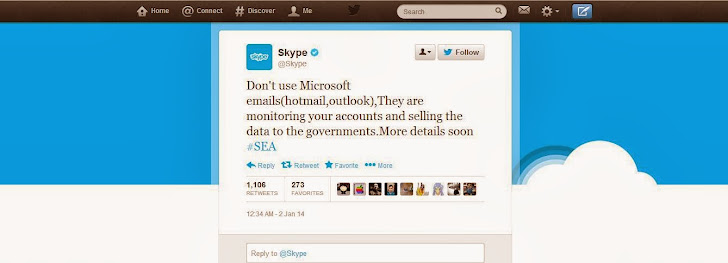
Happy 2014.. We are back with first hacking story of the year - SKYPE " Stop Spying " . Yes Skype Got hacked last night by an infamous hacker group called the Syrian Electronic Army , a group that supports Syria’s president and typically they publish pro-Syrian government messages, but its first time they are taking about PRIVACY . Syrian Hackers posted some messages on Skype’s Twitter account i.e. " Stop Spying on People! via Syrian Electronic Army ," Next tweet reads, " Don't use Microsoft emails (hotmail, outlook), They are monitoring your accounts and selling it to the governments. " Syrian Electronic Army hackers also compromised Skype’s Facebook page and a company blog hosted on Skype’s website. A blog post published on the official Skype blog featured the headline, " Hacked by Syrian Electronic Army.. Stop Spying! ", which now has been deleted by Microsoft. Now it appeared that Skype regained the access to their accounts and dele...
Happy Holidays and Merry Christmas from 'The Hacker News'

Happy Holidays and Merry Christmas from 'The Hacker News'

Dec 25, 2013
The Christmas spirit has finally arrived. It's Christmas Day, a time for family and friends. We have had another wonderful year here at ' The Hacker News ', so we not only want to wish you a Happy Holidays and Merry Christmas, but also thank you for reading our articles, commenting, sending tips and joining us for spreading Cyber awareness. We really appreciate your support and engagement with THN and with same goal i.e. To provide the most up-to-date information on a wide variety of topics that relate to hackers and security experts worldwide, we will return back with new ideas, gifts and stories from 1st January, 2014. Merry Christmas and a Blessed and Happy New Year to you and yours.
RSA denied accusations of inserting secret backdoor for the NSA

RSA denied accusations of inserting secret backdoor for the NSA

Dec 23, 2013
According to media reports in September, documents released by whistleblower Edward Snowden have confirmed the existence of backdoor in some technologies RSA . Last Friday, The Reuters News Agency accused the Security firm RSA for taking a $10 million ‘ bribe ’ from the National Security Agency ( NSA ) in order promote a flawed encryption by including it in its BSAFE product to facilitate NSA spying . Today In a blog post , RSA has categorically denied accusation about any secret partnership with the National Security Agency to insert backdoor. " Recent press coverage has asserted that RSA entered into a “secret contract” with the NSA to incorporate a known flawed random number generator into its BSAFE encryption libraries. We categorically deny this allegation. " " We have never entered into any contract or engaged in any project with the intention of weakening RSA’s products " the company said. The company gave the following reasons for choosing and promoting...
More than 1,400 Financial institutions in 88 Countries targeted by Banking Trojan in 2013

More than 1,400 Financial institutions in 88 Countries targeted by Banking Trojan in 2013

Dec 22, 2013
As the year draws to a close, we have seen the number of emerging threats like advance phishing attacks from the Syrian Electronic Army , financial malware and exploit kits, Cryptolocker ransomware infections, massive  Bitcoin theft, extensive privacy breach from NSA and many more. The financial malware's were the most popular threat this year. Money is always a perfect motivation for attackers and cyber criminals who are continually targeting financial institutions. On Tuesday, Antivirus firm Symantec has released a Threat report, called “ The State of Financial Trojans: 2013 ”, which revealed that over 1,400 financial institutions have been targeted and compromised millions of computers around the globe and the most targeted banks are in the US with 71.5% of all analyzed Trojans. Financial institutions have been fighting against malware for the last ten years to protect their customers and online transactions from threat. Over the time the attackers adapted to these counter...
iOS 7 Untethered Jailbreak released for iPhone, iPad, and iPod devices

iOS 7 Untethered Jailbreak released for iPhone, iPad, and iPod devices

Dec 22, 2013
If you love iPhone you are surely going to love this news. iOS 7 was released in 3 months before and today finally the  evad3rs team has released   an untethered jailbreak  for iPhone , iPad, and iPod devices running  iOS 7.0 through iOS 7.0.4. The evasi0n installer is compatible with Windows, Mac OS X and Linux so no matter what operating system you’re on, you should be able to jailbreak your device. Jailbreaking is the procedure of modifying the iOS of your iPhone to remove the limitations imposed by Apple. This allows a user to access and install a lot of new applications, software and other similar content which otherwise are not made available to iPhone users through the Apple Store. The process is very simple, and within five minutes you can jailbreak your device. According to the instructions, iTunes must be installed if you’re running Windows and the only prerequisite is that the device should be running iOS 7.0.4. Team advice ...
Hacker threatens to sell data of 3.7 Million Israeli Bank Customers, demands extortion money in Bitcoin

Hacker threatens to sell data of 3.7 Million Israeli Bank Customers, demands extortion money in Bitcoin

Dec 21, 2013
Data breaches and security incidents are a constant in the headlines these days. Hackers and cyber criminals   are motivated by status or money and finding new innovative and more creative attacks to achieve this. One of them are, Digital Bank robbery  - where the thieves didn't need masks and guns to pull off the job, all they need are - Hacking Skills, a computer and the Internet. Another way is  Cyber extortion  - threat of attack against an enterprise or a bank, coupled with a demand for money to avert or stop the attack. According to Haaretz news, A Hacker - who is the operator of a biggest botnet malware network in the Israel, has threatens 3 major Israeli banks, i.e. Israel Discount Bank, Bank Yahav and the First International Bank of Israel. " Bank received an e-mail message threatening that unless they handed over a certain sum in Bitcoins by the end of next week, a list of customers' details would be given to hostile elements. " Banks data...
NSA paid $10 Million bribe to RSA Security for Keeping Encryption Weak

NSA paid $10 Million bribe to RSA Security for Keeping Encryption Weak

Dec 21, 2013
If you own a world-renowned Security Product or a Service, National Security Agency (NSA) is ready to pay you 10 Million or more bribe for keeping intentional backdoor for them. According to an exclusive report published by Reuters , there is a secret deal between the NSA and respected encryption company RSA to implement a flawed security standard as the default protocol in its products. Earlier Edward Snowden leaks had revealed that the NSA created a flawed random number generation system (Dual_EC_DRBG), Dual Elliptic Curve , which RSA used in its Bsafe security tool and now Snowden has revealed that RSA received $10 million from NSA for keeping Encryption Weak. So, anyone who knows the right numbers used in Random number generator program, can decipher the resulting cryptotext easily. Recommending bad cryptographic standard is one thing, but accepting 10 million to deliberately implement is something very shameful for a respected Security company. The new ...
'The Washington Post' compromised 3rd time in the last 3 years

'The Washington Post' compromised 3rd time in the last 3 years

Dec 20, 2013
Security experts at Mandiant intelligence firm have discovered a new intrusion into the network of The Washington Post , it is the third time in the last three years. In time I'm writing it is still not clear the extension of the attack neither an estimation of the losses. Mandiant reported the incident to The Washington Post this week, confirming that exposed data include employees' credentials hash. " Hackers broke into The Washington Post’s servers and gained access to employee user names and passwords, marking at least the third intrusion over the past three years, company officials said Wednesday. " a post of the news agency said. Early 2013 the New York Times has announced that during the previous months it was a victim of cyber espionage coordinated by Chinese hacker s, similar attacks was conducted against principal Americans news agencies. The hackers have tried to compromise the email account of journalists to steal sensitive information, they tried ...
World’s largest Bitcoin Poker website hacked, 42000 user passwords leaked

World’s largest Bitcoin Poker website hacked, 42000 user passwords leaked

Dec 20, 2013
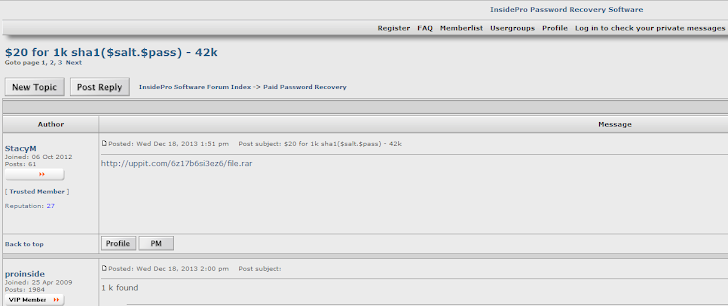
World’s largest Bitcoin poker website ' SealsWithClubs ' has been compromised and around 42,000 users' credentials are at risk. Seals With Club  has issued a  Mandatory Password Reset   warning to their users, according to a statement published on the website. The service admitted their database had been compromised and revealed that the data center used until November was breached, resulting 42,020 hashed password theft. " Passwords were salted and hashed per user, but to be safe every user MUST change their password when they next log in. Please do so at your earliest opportunity. If your Seals password was used for any other purpose you should reset those passwords too as a precaution. " and " Transfers may be disabled for a short period of time.". Seals With Clubs used SHA1 hash functions to encrypt the passwords, but SHA1 is outdated and easy to crack if not salted. ' StacyM ', a user then posted the hashed passwords on a web forum o...
Acoustic Cryptanalysis: Extracting RSA Key From GnuPG by capturing Computer Sound

Acoustic Cryptanalysis: Extracting RSA Key From GnuPG by capturing Computer Sound

Dec 20, 2013
' RSA Key Extraction via Low-Bandwidth Acoustic Cryptanalysis ', is an interesting paper recently published by Three Israeli Security Researchers at Tel Aviv University . They claimed that, they have successfully broken one of the most secure encryption algorithms, 4096-bit RSA , just by capturing Computer's CPU Sound while it runs decryption routines. Daniel Genkin, Adi Shamir (who co-invented RSA), and Eran Tromer , uses a side channel attack and through a process called “ acoustic cryptanalysis ”, they successfully extracted 4096-bit RSA key From GnuPG. " We experimentally demonstrate that such attacks can be carried out, using either a plain mobile phone placed next to the computer, or a more sensitive microphone placed 4 meters away, ” The paper specifies some possible implementations of this attack. Some email-client softwares i.e. Enigmail can automatically decrypt incoming e-mail (for notification purposes) using GnuPG. An attacker can e-mail suitably-...
Your MacBook Camera could Spy on You without lighting up the warning light

Your MacBook Camera could Spy on You without lighting up the warning light

Dec 20, 2013
If you own Apple's MacBook, you should cover up it's webcam, because there’s a possibility someone could be watching you. Like most webcams, the MacBook also has a tiny green light lets you know that the webcam is active, but it's possible for malware to disable this important privacy feature on older Mac computers ( models released before 2008 ). Matthew Brocker and Stephen Checkoway , students from Johns Hopkins University created a proof-of-concept app called “ iSeeYou ” that confirmed that MacBook iSight webcams can spy on their users without the warning light being activated. A young man recently pleaded guilty in court to extortion after he performed a remote hack on Miss Teen USA’s webcam to secretly collect nude photos. It was revealed through court papers that the FBI has the ability to do the same thing with a variety of current laptops including Apple products. To make it possible, they created a modified version of the iSight firmware and t...
40 Million Credit Card accounts affected in massive data breach at 'Target' Stores during Black Friday

40 Million Credit Card accounts affected in massive data breach at 'Target' Stores during Black Friday

Dec 19, 2013
If you have shopped something during the Black Friday weekend from Target's U.S based Retailer stores, then please pay serious attention - Your Credit and Debit card account may have been at Risk. There are more than 1,500 Target stores throughout the U.S and 40 Million credit and debit card accounts of Target's customers may have been stolen during the height of the holiday shopping season, according to a statement  published by the company. Somehow thieves allegedly gained access to personal data in stores when customers swiped their cards at the register. That information is then typically sold to buyers who then make bogus debit or credit cards with it. So the customers who made purchases by swiping their cards at terminals in its U.S. Stores between November 27 and December 15 may have been exposed.  Krebs who broke the story reports that the breach does not impact shoppers who purchased items online. Target has not disclosed exactly how t...
Researchers spotted 'Chewbacca', a new Tor-based Banking Trojan

Researchers spotted 'Chewbacca', a new Tor-based Banking Trojan

Dec 18, 2013
Cyber Criminal activity associated with the financial Trojan programs has increased rapidly during the past few months. However, the Tor -based architecture is the favorite one with online criminals, to hide their bots and the botnet's Command-and-Control real location from the security researchers. Security Researchers at anti-virus firm  Kaspersky Lab have discovered a new Tor-based  banking trojan , dubbed " ChewBacca " (" Trojan . Win32 . Fsysna . fej ")  , that steal banking credentials and hosted on a Tor . onion domain. This protects the location of a server as well as the identity of the owner in most cases. Still there are drawbacks preventing many criminals from hosting their servers within Tor. Due to the overlay and structure, Tor is slower and timeouts are possible. Massive botnet activity may influence the whole network, as seen with Mevade, and therefore let researchers spot them more easily. ChewBacca   malware is not first that adopt To...
Judge Ruled - NSA Telephone Metadata Collection violates the Fourth Amendment

Judge Ruled - NSA Telephone Metadata Collection violates the Fourth Amendment

Dec 17, 2013
Big and Good news for all of us. A federal court judge ' Richard J. Leon ' said that he believes, US National Security Agency’s (NSA) controversial practice of routinely collecting the telephone records of millions of Americans likely violates the 4th Amendment and is unconstitutional, even though the FISA court approved it. Earlier in 2013, a conservative Legal Activist Larry Klayman filed a lawsuit against the US government, alleging that NSA’s massive telephone surveillance program violates the " reasonable expectation of privacy, free speech and association, right to be free of unreasonable searches and seizures and due process rights. " NYTimes reported that last Monday in the decision, Judge has ordered [  Case:  Klayman v. Obama (13-851)  PDF File  ] the NSA to stop collecting U.S. Citizen’s Telephone records, and to destroy the files it already holds. This was the first major court ruling about NSA' so-called metadata counter terrorism p...
Russian hackers stole Personal details of 54 million Turkish Citizens

Russian hackers stole Personal details of 54 million Turkish Citizens

Dec 17, 2013
The Publicized Hacks, Cyber attacks and Data breaches continue to increase, and the majority of attacks are from outsiders. Recently, Some unknown Russian hackers have reportedly stolen Personal details of nearly 54 million Turkish citizens, about 70% of the whole Turkish population. According to a report published by ' Hurriyet News ', Researchers from  KONDA  Security firm revealed that the hackers have stolen data from a political party's  vulnerable  system that include Name, ID numbers and address of 54 million voters across the Nation. Researchers claimed that the hacked system (being used for Database and website Management) did not have any antivirus product installed and voter information was also uploaded online on a vulnerable website. This was really a bad idea, and they mentioned that “ in two hours hackers downloaded all the information. ” In another statement, they mentioned that some government instituti...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources