-->
#1 Trusted Cybersecurity News Platform
Followed by 5.80+ million
The Hacker News Logo
Get Updates
cybersecurity

The Hacker News | #1 Trusted Source for Cybersecurity News — Index Page

98% of SSL enabled websites still using SHA-1 based weak Digital Certificates

98% of SSL enabled websites still using SHA-1 based weak Digital Certificates

Feb 06, 2014
The National Institute of Standards and Technology (NIST) had published a document on Jan 2011 that the SHA-1 algorithm will be risky and should be disallowed after year 2013, but it was recently noticed by Netcraft experts that NIST.gov website itself were using 2014 dated SSL certificate with SHA-1 hashes. " From January 1, 2011 through December 31, 2013, the use of SHA-1 is deprecated for digital signature generation. The user must accept risk when SHA-1 is used, particularly when approaching the December 31, 2013 upper limit. SHA-1 shall not be used for digital signature generation after December 31, 2013. " NIST in the document. Digital signatures facilitate the safe exchange of electronic documents by providing a way to test both the authenticity and the integrity of information exchanged digitally. Authenticity means when you sign data with a digital signature, someone else can verify the signature, and can confirm that the data originated from you and was not...
British Intelligence Agency DDoSed Anonymous Chatrooms to disrupt communication

British Intelligence Agency DDoSed Anonymous Chatrooms to disrupt communication

Feb 06, 2014
Since 2011, the collective hacking group, Anonymous and LulzSec were targeting both Government and law-enforcement websites of U.S and UK, by their own DDoS attack tactics which they used to communicate and plan on Chat rooms known as IRCs, but British intelligence agency GCHQ used their own weapon against them. According to the recent Edward Snowden document, a division of Government Communications Headquarters (GCHQ), which is also very well known as the British counterpart of the NSA, had shut down communications among Anonymous hacktivists by launching a “ denial of service ” (DDOS) attacks, making the British government the first western government known to have conducted such an attack, NBC news reports . The same DDoS technique the hackers use to take down government, political and industry websites, including the Central Intelligence Agency (CIA), Federal bureau of Investigation (FBI), the Serious Organized Crime Agency (SOCA), Sony News International and Westbor...
Google adds its Chrome apps and extensions to Bug Bounty Program

Google adds its Chrome apps and extensions to Bug Bounty Program

Feb 06, 2014
Google's Vulnerability Reward Program which started in November 2010, offers a hefty reward to the one who find a good vulnerability in its products.  Now Google is getting a little more serious about the security of its Chrome Browser and has expanded its Bug Bounty Program to include all Chrome apps, extensions developed and branded as " by Google ". The Internet is a platform which has become a necessary medium for performing our daily tasks like reading news, paying bills, playing games, scheduling meetings and everything we perform on this platform is possible only because of the various applications maintained by the service providers. " We think developing Chrome extensions securely is relatively easy, but given that extensions like Hangouts and GMail are widely used, we want to make sure efforts to keep them secure are rewarded accordingly. " Google said in a blog post . Not only this, to improve the security of open-source proje...
cyber security

Incident Response Starter Pack

websiteWizIncident Response / Cloud Security
7 cloud incident response resources in one bundle. Get ready-to-use playbooks to contain, isolate, and defeat cloud threats.
cyber security

SANS 2026 State of ICS/OT Security Report

websiteSANS InstituteICS/OT Security
See what nearly 700 industrial professionals reveal about keeping operations safe during a cyber incident.
Facebook domain hacked by Syrian Electronic Army

Facebook domain hacked by Syrian Electronic Army

Feb 06, 2014
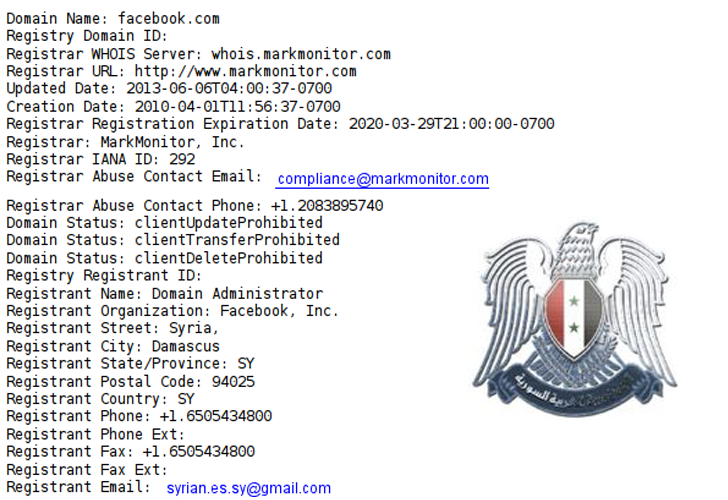
On the 10th Anniversary of Social networking website Facebook, the hacker group ' Syrian Electronic Army ' claimed that they managed to hack into the administrator account of the Facebook's Domain Registrar - MarkMonitor. The hacking group changed the Facebook Domain's contact information to a Syrian email address on the company’s WHOIS domain information page, as shown. " Happy Birthday Mark! http://Facebook.com owned by #SEA " the group tweeted . Hackers also claimed that it had updated the nameserver information to hijack domain, but the process had to be abandoned because it was " taking too much time... " whereas, Facebook spokesperson did confirm that the website's domain record email contact information had been changed. Why SEA Targeted Facebook? Syrian activists and Hackers claimed that Facebook has been deleting pages created by dissidents and removing content as it was violating the social network’s standards, acc...
Adobe issues Emergency Flash Player update to patch critical zero-day threat

Adobe issues Emergency Flash Player update to patch critical zero-day threat

Feb 05, 2014
Adobe is recommending that users update their Flash Players immediately. The company has published an emergency security bulletin today, that addresses vulnerabilities the Flash Player and released a patch to fix a vulnerability which is currently being exploited in a sophisticated cyber espionage campaign. " Adobe is aware of reports that an exploit for this vulnerability exists in the wild, and recommends users apply the updates referenced in the security bulletin. " The vulnerability ( CVE-2014-0497 ), allows an attacker to remotely take control of the targeted system hosting Flash. " These updates address a critical vulnerability that could potentially allow an attacker to remotely take control of the affected system " advisory said. The security hole affects the version 12.0.0.43 and earlier for both Windows and Mac OSs and Adobe Flash Player 11.2.202.335 and earlier versions for Linux. The vulnerability was discovered by two researchers...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources