-->
#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

The Hacker News | #1 Trusted Source for Cybersecurity News — Index Page

Cryptolocker Malware learned to replicate itself through removable USB drives

Cryptolocker Malware learned to replicate itself through removable USB drives

Jan 06, 2014
In the category of Ransomware Malware, a nasty piece of malware called  CRYPTOLOCKER  is on the top, that threatened most of the people around the world, effectively destroying important files of the victims. Cryptolocker, which strongly encrypts victims' hard drives until a ransom is paid, is now again back in action to haunt your digital life with an additional feature. Until now, CryptoLocker has been spread via spam email, with victims tempted to download an attachment or click on a link to a malicious website, but now it can spread itself as a worm through removable USB drives . Security Researchers at Trend Micro have recently reported a new variant of Cryptolocker which is capable of spreading through removable USB drives. As Previously reported by our Security experts at The Hacker News , Cryptolocker is a malware which locks your files and demand a ransom to release it. The files are encrypted so removing the malware from the system doesn’t unlo...
Coca-Cola reserved 16 Million MAC addresses to race in The Internet of Things

Coca-Cola reserved 16 Million MAC addresses to race in The Internet of Things

Jan 06, 2014
Have you seen the Coca-Cola " Freestyle " soda fountain yet? Instead of levers for different sodas, you have got a touchscreen, interface like an iPad and with a Push button you can have 127 Flavors of sodas. There are more than 3,500 such machines are installed inside the world’s Burger Kings and all of them are connected to the internet, so that Coca-Cola can track inventory and making stock decisions. Last week the developer of GNU MACChanger software, Alvaro Lopez Ortega found that Coca-Cola has reserved a huge block of MAC addresses, i.e. 16 Million. These could conceivably be used in the future for tagging physical devices, Freestyle Soda machines or vending machines. Media Access Control address, a hardware address that uniquely identifies each node of a network. Every piece of hardware on your local network has a MAC address in addition to the IP address assigned to it by the local router or a server. IEEE has a Registration Authority called OUI that m...
Yahoo Ad Network abused to redirect users to malicious websites serving Magnitude Exploit Kit

Yahoo Ad Network abused to redirect users to malicious websites serving Magnitude Exploit Kit

Jan 05, 2014
Internet advertisement networks provide hackers with an effective venue for targeting wide range computers through malicious advertisements. Previously it was reported by some security researchers that Yahoo's online advertising Network is one of the top ad networks were being abused to spread malware by cyber criminals . Recent report published by Fox-IT, Hackers are using Yahoo's advertising servers to distribute malware to hundreds of thousands of users since late last month that affecting thousands of users in various countries. " Clients visiting yahoo.com received advertisements served by ads.yahoo.com. Some of the advertisements are malicious ," the firm reported . More than 300,000 users per hour were being redirected to malicious websites serving 'Magnitude Exploit Kit', that exploits vulnerabilities in Java and installs a variety of different malware i.e. ZeuS Andromeda Dorkbot/Ngrbot Advertisement clicking malware Tinba/Zusy Necurs "...
cyber security

AI Security's Greatest Hits

websiteWizAI Security / Cheat Sheet
Get 7 of the most widely used AI security resources in one pack. Each asset provides practical tools for securing AI apps, models, and agents.
cyber security

Free Assessment: Identify Hidden Internal Risk

websiteBitdefenderAttack Surface / Threat Detection
Discover unnecessary user access to risky tools, shadow IT, based on real user behavior.
NSA will not stop spying on us, next move Quantum computer to break strongest Encryption

NSA will not stop spying on us, next move Quantum computer to break strongest Encryption

Jan 04, 2014
Image Credit: The guardian  If I say that  NSA (National Security Agency) will never stop spying on us then it won’t be wrong. After the exposure of the large number of surveillance scandals including PRISM, DROPOUTJEEP, XKeyscore and many many more which are now publicly known as well as unknown, Will NSA ever stop Privacy  breach? Obviously ' NO' . That I can predict from another Snowden leak published by the Washington Post news website recently i.e. US National Security Agency (NSA) is trying to develop a futuristic super computer called ' Quantum computer'  that could be capable of breaking almost every kind of encryption on the computer used to protect banks, medical, business including top-secret information held by government around the world. The Project is specified as “ Penetrating Hard Targets ” in the document and is a part of $79.7 million research program. The Washington Post says that the research is being done at the University of Mar...
Prison Locker Ransomware, an upcoming malware threat in 2014

Prison Locker Ransomware, an upcoming malware threat in 2014

Jan 04, 2014
Ransomware is one of the most blatant and obvious criminal's money making schemes out there. Ransomware malware was mostly known by the people when Cryptolocker comes into play. At the time when readers were getting aware of ransomware, Cryptolocker threat had touched the peak and other money motivated cyber criminals have started developing their own Cryptolocker versions. Two hackers going by the name of ' gyx ' and ' Porphyry ' (admin of maldev.net hacking forum) are advertizing a new ramsomware malware tool-kit called "Prison Locker" on various hacking forums with tutorials. They have developed the Prison Locker a.k.a Power Locker ramsomware toolkit in C/C++ programming language, proving a GUI version with customizable features for customers. The Ransomware is using BlowFish encryption to encrypt all available files on the victim's hard disk and shared drives except . exe , . dll , . sys , other system files. During encryption it will ge...
Hacking Wireless DSL routers via Administrative password Reset Vulnerability

Hacking Wireless DSL routers via Administrative password Reset Vulnerability

Jan 04, 2014
If you want to hack a Netgear and Linkys Wireless Routers , there is a quick backdoor entry available, that allow an attacker to reset the admin panel password to defaults. Eloi Vanderbeken , a hacker and reverse-engineer from France has discovered an administration password Reset vulnerability in many Netgear and Linkys Routers. In a blog post , Eloi said that During Christmas Holidays he forgot the admin interface password of his Linksys WAG200G router and in an effort to gain access back of its administration panel, he first scanned the Router and found a suspicious open TCP port i.e. 32764. To do further research on this port service, he downloaded a copy Linksys firmware and reverse-engineered it. He found was a secret backdoor interface that allowed him to send commands to the router from a command-line shell without being authenticated as the administrator. Then he blindly tested commands, but doing so flips the router's configuration back ...
Windows Error Crash Reports or Treasure of Zero-Day vulnerabilities for NSA?

Windows Error Crash Reports or Treasure of Zero-Day vulnerabilities for NSA?

Jan 03, 2014
I am sure that you all have been familiar with the above shown annoying Window Operating System error messages that many times pop ups on your screen while working on the system in case of process failure i.e. " The system has recovered from a serious error. A log of this error has been created. Please tell Microsoft about this problem " The message that prompts ask the user to report the problem to Microsoft followed by the options to Send an error report or Not send . Most of the time Gentle users like you and me used to submit these error reports to aware the Microsoft about the problem. But What if these crash reports can be abused to identify the vulnerabilities of your system for Spying? NSA is intercepting wide range of Internet Traffic including many Encrypted connections and naturally unencrypted also and surprisingly, by default Microsoft encrypts its reports, but the messages are transmitted unencrypted or over standard HTTP connections to watson.microsoft.c...
Abusing Network Time Protocol (NTP) to perform massive Reflection DDoS attack

Abusing Network Time Protocol (NTP) to perform massive Reflection DDoS attack

Jan 03, 2014
In 2013, we have seen a significant increase in the use of a specific distributed denial of service (DDoS) methodology known as Distributed Reflection Denial of Service attacks (DrDoS). Open and misconfigured DNS (Domain Name System) can be used by anyone to resolve domain names to IP addresses are increasingly abused to launch powerful DDoS attacks. But not only the DNS servers, Security Researchers at Symantec  have spotted Network Time Protocol (NTP) reflection DDoS attacks being launched by cyber criminals during the Christmas Holidays. ' Network Time Protocol (NTP) ' is a distributed network clock time synchronization protocol that is used to synchronize computer clock times in a network of computers and runs over port 123 UDP. NTP is one of those set-it-and-forget-it protocols that is configured once and most network administrators don't worry about it after that. Unfortunately, that means it is also not a service that is upgraded often, leaving it vulnerable to th...
Hackers stole money from European ATMs using Malware-loaded USB Device

Hackers stole money from European ATMs using Malware-loaded USB Device

Jan 02, 2014
Hacking ATM Machines is nothing new, but it seems that instead of relying on ATM skimmers now some smart hackers in Europe are reportedly targeting ATM Machines using Malware -loaded USB drives to steal money. Most of the world’s ATMs are running on Windows XP operating system, which is highly vulnerable to Malware attacks. Just like your Desktop Laptops, some ATMs also have USB sockets, which is hidden behind the ATM’s fascia. The German security researchers who discovered the hack detailed their findings at the Chaos Computing Congress in Hamburg, Germany recently. They said that the thieves cut holes in the fascia to access a USB port and then uploaded malware to the machines. The malware creates a backdoor that can be accessed on the front panel. " These researchers explained that the malware allowed the thieves to create a unique interface on the ATMs by typing in a 12-digit code. This interface allowed for withdrawal and also showed the criminals the amount of money and e...
DROPOUTJEEP: NSA's Secret program to access any Apple iPhone, including microphone & camera

DROPOUTJEEP: NSA's Secret program to access any Apple iPhone, including microphone & camera

Jan 02, 2014
In the era of Smartphones, Apple’s iPhone is the most popular device that exists, which itself gives the reason to target it. According to leaked documents shared by Security researcher  Jacob Appelbaum , a secret NSA program code named DROPOUTJEEP has nearly total access to the Apple’s iPhones, which uses “ modular mission applications to provide specific SIGINT functionality. ” While giving the presentation at the Chaos Communications Congress (30C3) in Hamburg, Germany on Monday, Appelbaum revealed that NSA reportedly sniffing out every last bit of data from your iPhone. DROPOUTJEEP is a software implant for the Apple iPhone that utilizes modular mission applications to provide specific SIGINT functionality. This functionality includes the ability to remotely push/pull files from the device. SMS retrieval, contact list retrieval, voicemail, geolocation, hot mic, camera capture, cell tower location, etc. Command, control and data exfiltration can occur over SMS messa...
Firmware vulnerability allows man-in-the-middle attack using SD Memory cards

Firmware vulnerability allows man-in-the-middle attack using SD Memory cards

Jan 02, 2014
How is it possible to exploit SD Card, USB stick and other mobile devices for hacking? Another interesting hack was presented at the Chaos Computer Congress (30C3), in Hamburg, Germany. The researchers demonstrated how it is possible to hack the microcontroller inside every SD and MicroSD flash cards that allow arbitrary code execution and can be used to perform a man in the middle attack . The Hardware Hackers  Andrew “ bunnie ” Huang and Sean “xobs”  described the exploitation method on their blog post ," it also enables the possibility for hardware enthusiasts to gain access to a very cheap and ubiquitous source of microcontrollers. " It seems that to reduce SD cards price and increase their storage capability, engineers have to consider a form of internal entropy that could affect data integrity on every Flash drive. Almost every NAND flash memory is affected by defects and presents problems like electron leakage between adjacent cells. " Flash memory is really ...
Skype's Official Twitter, Facebook and Blog Hacked by Syrian Electronic Army

Skype's Official Twitter, Facebook and Blog Hacked by Syrian Electronic Army

Jan 02, 2014
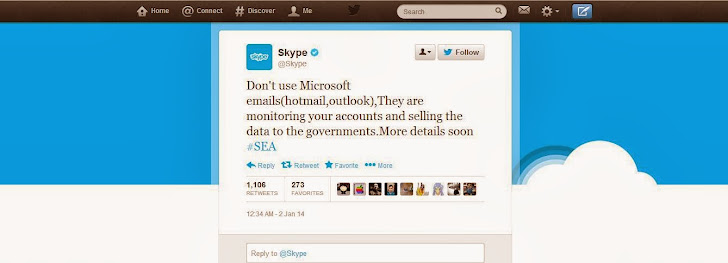
Happy 2014.. We are back with first hacking story of the year - SKYPE " Stop Spying " . Yes Skype Got hacked last night by an infamous hacker group called the Syrian Electronic Army , a group that supports Syria’s president and typically they publish pro-Syrian government messages, but its first time they are taking about PRIVACY . Syrian Hackers posted some messages on Skype’s Twitter account i.e. " Stop Spying on People! via Syrian Electronic Army ," Next tweet reads, " Don't use Microsoft emails (hotmail, outlook), They are monitoring your accounts and selling it to the governments. " Syrian Electronic Army hackers also compromised Skype’s Facebook page and a company blog hosted on Skype’s website. A blog post published on the official Skype blog featured the headline, " Hacked by Syrian Electronic Army.. Stop Spying! ", which now has been deleted by Microsoft. Now it appeared that Skype regained the access to their accounts and dele...
Happy Holidays and Merry Christmas from 'The Hacker News'

Happy Holidays and Merry Christmas from 'The Hacker News'

Dec 25, 2013
The Christmas spirit has finally arrived. It's Christmas Day, a time for family and friends. We have had another wonderful year here at ' The Hacker News ', so we not only want to wish you a Happy Holidays and Merry Christmas, but also thank you for reading our articles, commenting, sending tips and joining us for spreading Cyber awareness. We really appreciate your support and engagement with THN and with same goal i.e. To provide the most up-to-date information on a wide variety of topics that relate to hackers and security experts worldwide, we will return back with new ideas, gifts and stories from 1st January, 2014. Merry Christmas and a Blessed and Happy New Year to you and yours.
RSA denied accusations of inserting secret backdoor for the NSA

RSA denied accusations of inserting secret backdoor for the NSA

Dec 23, 2013
According to media reports in September, documents released by whistleblower Edward Snowden have confirmed the existence of backdoor in some technologies RSA . Last Friday, The Reuters News Agency accused the Security firm RSA for taking a $10 million ‘ bribe ’ from the National Security Agency ( NSA ) in order promote a flawed encryption by including it in its BSAFE product to facilitate NSA spying . Today In a blog post , RSA has categorically denied accusation about any secret partnership with the National Security Agency to insert backdoor. " Recent press coverage has asserted that RSA entered into a “secret contract” with the NSA to incorporate a known flawed random number generator into its BSAFE encryption libraries. We categorically deny this allegation. " " We have never entered into any contract or engaged in any project with the intention of weakening RSA’s products " the company said. The company gave the following reasons for choosing and promoting...
More than 1,400 Financial institutions in 88 Countries targeted by Banking Trojan in 2013

More than 1,400 Financial institutions in 88 Countries targeted by Banking Trojan in 2013

Dec 22, 2013
As the year draws to a close, we have seen the number of emerging threats like advance phishing attacks from the Syrian Electronic Army , financial malware and exploit kits, Cryptolocker ransomware infections, massive  Bitcoin theft, extensive privacy breach from NSA and many more. The financial malware's were the most popular threat this year. Money is always a perfect motivation for attackers and cyber criminals who are continually targeting financial institutions. On Tuesday, Antivirus firm Symantec has released a Threat report, called “ The State of Financial Trojans: 2013 ”, which revealed that over 1,400 financial institutions have been targeted and compromised millions of computers around the globe and the most targeted banks are in the US with 71.5% of all analyzed Trojans. Financial institutions have been fighting against malware for the last ten years to protect their customers and online transactions from threat. Over the time the attackers adapted to these counter...
iOS 7 Untethered Jailbreak released for iPhone, iPad, and iPod devices

iOS 7 Untethered Jailbreak released for iPhone, iPad, and iPod devices

Dec 22, 2013
If you love iPhone you are surely going to love this news. iOS 7 was released in 3 months before and today finally the  evad3rs team has released   an untethered jailbreak  for iPhone , iPad, and iPod devices running  iOS 7.0 through iOS 7.0.4. The evasi0n installer is compatible with Windows, Mac OS X and Linux so no matter what operating system you’re on, you should be able to jailbreak your device. Jailbreaking is the procedure of modifying the iOS of your iPhone to remove the limitations imposed by Apple. This allows a user to access and install a lot of new applications, software and other similar content which otherwise are not made available to iPhone users through the Apple Store. The process is very simple, and within five minutes you can jailbreak your device. According to the instructions, iTunes must be installed if you’re running Windows and the only prerequisite is that the device should be running iOS 7.0.4. Team advice ...
Hacker threatens to sell data of 3.7 Million Israeli Bank Customers, demands extortion money in Bitcoin

Hacker threatens to sell data of 3.7 Million Israeli Bank Customers, demands extortion money in Bitcoin

Dec 21, 2013
Data breaches and security incidents are a constant in the headlines these days. Hackers and cyber criminals   are motivated by status or money and finding new innovative and more creative attacks to achieve this. One of them are, Digital Bank robbery  - where the thieves didn't need masks and guns to pull off the job, all they need are - Hacking Skills, a computer and the Internet. Another way is  Cyber extortion  - threat of attack against an enterprise or a bank, coupled with a demand for money to avert or stop the attack. According to Haaretz news, A Hacker - who is the operator of a biggest botnet malware network in the Israel, has threatens 3 major Israeli banks, i.e. Israel Discount Bank, Bank Yahav and the First International Bank of Israel. " Bank received an e-mail message threatening that unless they handed over a certain sum in Bitcoins by the end of next week, a list of customers' details would be given to hostile elements. " Banks data...
NSA paid $10 Million bribe to RSA Security for Keeping Encryption Weak

NSA paid $10 Million bribe to RSA Security for Keeping Encryption Weak

Dec 21, 2013
If you own a world-renowned Security Product or a Service, National Security Agency (NSA) is ready to pay you 10 Million or more bribe for keeping intentional backdoor for them. According to an exclusive report published by Reuters , there is a secret deal between the NSA and respected encryption company RSA to implement a flawed security standard as the default protocol in its products. Earlier Edward Snowden leaks had revealed that the NSA created a flawed random number generation system (Dual_EC_DRBG), Dual Elliptic Curve , which RSA used in its Bsafe security tool and now Snowden has revealed that RSA received $10 million from NSA for keeping Encryption Weak. So, anyone who knows the right numbers used in Random number generator program, can decipher the resulting cryptotext easily. Recommending bad cryptographic standard is one thing, but accepting 10 million to deliberately implement is something very shameful for a respected Security company. The new ...
'The Washington Post' compromised 3rd time in the last 3 years

'The Washington Post' compromised 3rd time in the last 3 years

Dec 20, 2013
Security experts at Mandiant intelligence firm have discovered a new intrusion into the network of The Washington Post , it is the third time in the last three years. In time I'm writing it is still not clear the extension of the attack neither an estimation of the losses. Mandiant reported the incident to The Washington Post this week, confirming that exposed data include employees' credentials hash. " Hackers broke into The Washington Post’s servers and gained access to employee user names and passwords, marking at least the third intrusion over the past three years, company officials said Wednesday. " a post of the news agency said. Early 2013 the New York Times has announced that during the previous months it was a victim of cyber espionage coordinated by Chinese hacker s, similar attacks was conducted against principal Americans news agencies. The hackers have tried to compromise the email account of journalists to steal sensitive information, they tried ...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources