#1 Trusted Cybersecurity News Platform
Followed by 5.80+ million
The Hacker News Logo
Get Updates
cybersecurity

Search results for watering hole | Breaking Cybersecurity News | The Hacker News

Iran-Linked Imperial Kitten Cyber Group Targeting Middle East's Tech Sectors

Iran-Linked Imperial Kitten Cyber Group Targeting Middle East's Tech Sectors

Nov 10, 2023 Cyber Attack / Cyber Threat
A group with links to Iran targeted transportation, logistics, and technology sectors in the Middle East, including Israel, in October 2023 amid a surge in Iranian cyber activity since the onset of the Israel-Hamas war. The attacks have been attributed by CrowdStrike to a threat actor it tracks under the name  Imperial Kitten , and which is also known as Crimson Sandstorm (previously Curium), TA456, Tortoiseshell, and Yellow Liderc. The latest findings from the company build on prior reports from  Mandiant ,  ClearSky , and  PwC , the latter of which also detailed instances of strategic web compromises (aka watering hole attacks) leading to the deployment of IMAPLoader on infected systems. “The adversary, active since at least 2017, likely fulfills Iranian strategic intelligence requirements associated with IRGC operations,” CrowdStrike  said  in a technical report. “Its activity is characterized by its use of social engineering, particularly job recrui...
Candiru Spyware Caught Exploiting Google Chrome Zero-Day to Target Journalists

Candiru Spyware Caught Exploiting Google Chrome Zero-Day to Target Journalists

Jul 22, 2022
The actively exploited but now-fixed Google Chrome zero-day flaw that came to light at the start of this month was weaponized by an Israeli spyware company and used in attacks targeting journalists in the Middle East. Czech cybersecurity firm Avast linked the exploitation to  Candiru  (aka Saito Tech), which has a history of  leveraging previously unknown flaws  to deploy a Windows malware dubbed DevilsTongue , a modular implant with  Pegasus -like capabilities. Candiru, along with NSO Group, Computer Security Initiative Consultancy PTE. LTD., and Positive Technologies, were  added to the entity list  by the U.S. Commerce Department in November 2021 for engaging in "malicious cyber activities." "Specifically, a large portion of the attacks took place in Lebanon, where journalists were among the targeted parties," security researcher Jan Vojtěšek, who reported the discovery of the flaw,  said  in a write-up. "We believe the attacks were hi...
Latest Internet Explorer zero-day linked to Elderwood Project

Latest Internet Explorer zero-day linked to Elderwood Project

Jan 06, 2013
Last week we have seen ongoing attacks was exploiting a vulnerability in Internet Explorer 6, Internet Explorer 7, and Internet Explorer 8 that came to light after the Council on Foreign Relations website was hacked and was hosting the code. Symantec has linked exploits to the group responsible for a spate of recent espionage attacks Dubbed the " Elderwood Project ". In May 2012, Amnesty International’s Hong Kong website was compromised & used to serve up a malicious SWF file that exploited CVE-2012-1875, a vulnerability affecting Internet Explorer. A few months later in Sep 2012, the same group behind that attack was responsible for using another IE zero-day CVE-2012-4969. Microsoft issued a temporary Fix-it patch for the vulnerability but now researchers are claiming that they have bypassed the patch and were able to compromise a fully patched system. Name comes from a source code variable used by the attackers. In the past, the group has used a mix o...
cyber security

AI Security Training for the Job You Already Have

websiteSANS InstituteAI Security / Training
SOC, DFIR, pentest, app security: see the six GIAC AI certifications and the labs behind each.
cyber security

Know Your Enemy: The Attacker Toolkits Getting Past Security Controls

websitePush SecurityPhishing / Enterprise Security
Find out which toolkits bypass controls to reach your users most often. Join the webinar, Dec 2nd.
From Watering Hole to Spyware: EvilBamboo Targets Tibetans, Uyghurs, and Taiwanese

From Watering Hole to Spyware: EvilBamboo Targets Tibetans, Uyghurs, and Taiwanese

Sep 25, 2023 Spyware / Cyber Espionage
Tibetan, Uyghur, and Taiwanese individuals and organizations are the targets of a persistent campaign orchestrated by a threat actor codenamed  EvilBamboo  to gather sensitive information. "The attacker has created fake Tibetan websites, along with social media profiles, likely used to deploy browser-based exploits against targeted users," Volexity security researchers Callum Roxan, Paul Rascagneres, and Thomas Lancaster said in a report published last week. "Partly through impersonating existing popular communities, the attacker has built communities on online platforms, such as Telegram, to aid in distribution of their malware." EvilBamboo, formerly tracked by the cybersecurity firm under the name Evil Eye, has been linked to multiple attack waves  since at least 2019 , with the threat actor leveraging watering hole attacks to deliver spyware targeting Android and iOS devices. It's also known as Earth Empusa and POISON CARP. The intrusions directed agai...
Russian APT28 Breaches NATO Naval Shipbuilder in NATO Country, Deploys New Reflective Loader

Russian APT28 Breaches NATO Naval Shipbuilder in NATO Country, Deploys New Reflective Loader

Oct 20, 2026 Cyber Espionage / Cyber Attack
The Russia-linked state-sponsored threat actor tracked as APT28 (aka BlueDelta, Fancy Bear, and Forest Blizzard) has been attributed to attacks targeting two member states of the North Atlantic Treaty Organization (NATO). The Symantec Threat Hunter Team, which is tracking the activity cluster under the moniker Swallowtail , involved the use of a backdoor called HOOKEDGE and a previously undocumented loader that is designed to decrypt and run an encrypted payload in memory by using a cryptographic key that's supplied at runtime. Targets of the activity included a law enforcement agency, a naval shipbuilder, and a manufacturer of military aircraft engines – entities that hold information that could be of use to a foreign intelligence agency, the Broadcom-owned threat intelligence unit said. "During one attack against the naval shipbuilder, operators returned to a compromised host repeatedly over the course of a week in what appeared to be hands-on-keyboard activity,...
Coruna iOS Kit Reuses 2023 Triangulation Exploit Code in Recent Mass Attacks

Coruna iOS Kit Reuses 2023 Triangulation Exploit Code in Recent Mass Attacks

Mar 26, 2026 Malware / Mobile Security
The kernel exploit for two security vulnerabilities used in the recently uncovered Apple iOS exploit kit known as Coruna is an updated version of the same exploit that was used in the Operation Triangulation campaign back in 2023, according to new findings from Kaspersky. "When Coruna was first reported, the public evidence wasn't sufficient to link its code to Triangulation — shared vulnerabilities alone don't prove shared authorship," Boris Larin, principal security researcher at Kaspersky GReAT, told The Hacker News in a statement. "Coruna is not a patchwork of public exploits; it is a continuously maintained evolution of the original Operation Triangulation framework. The inclusion of checks for recent processors like the M3 and newer iOS builds shows that the original developers have actively expanded this codebase. What began as a precision espionage tool is now deployed indiscriminately." Coruna was first documented by Google and iVerify earli...
Silver Fox Exploits Microsoft-Signed WatchDog Driver to Deploy ValleyRAT Malware

Silver Fox Exploits Microsoft-Signed WatchDog Driver to Deploy ValleyRAT Malware

Sep 02, 2025 Financial Fraud / Endpoint Protection
The threat actor known as Silver Fox has been attributed to abuse of a previously unknown vulnerable driver associated with WatchDog Anti-malware as part of a Bring Your Own Vulnerable Driver ( BYOVD ) attack aimed at disarming security solutions installed on compromised hosts. The vulnerable driver in question is "amsdk.sys" (version 1.0.600), a 64-bit, validly signed Windows kernel device driver that's assessed to be built upon Zemana Anti-Malware SDK. "This driver, built on the Zemana Anti-Malware SDK, was Microsoft-signed, not listed in the Microsoft Vulnerable Driver Blocklist , and not detected by community projects like LOLDrivers," Check Point said in an analysis. The attack is characterized by a dual-driver strategy, where a known vulnerable Zemana driver ("zam.exe") is used for Windows 7 machines, and the undetected WatchDog driver for systems that run on Windows 10 or 11. The WatchDog Anti-malware driver has been found to contain mu...
Gunra Ransomware Exploits Fortinet FortiOS, FortiProxy Flaws to Breach Networks

Gunra Ransomware Exploits Fortinet FortiOS, FortiProxy Flaws to Breach Networks

Aug 11, 2026 Ransomware / Threat Intelligence
Cybersecurity and intelligence agencies from South Korea and the U.S. warned of Gunra ransomware attacks targeting critical infrastructure sectors and organizations across the world. Targets of these attacks include healthcare and public health, financial services, government services and facilities, and professional and nonprofit services. "Gunra is another variant in the ongoing trend of ransomware attacks causing disruption and harm to U.S. and international organizations," CISA Acting Executive Assistant Director for Cybersecurity, Chris Butera, said. Attacks deploying the ransomware have leveraged security flaws in internet-facing Fortinet FortiOS and FortiProxy ( CVE-2024-55591  and CVE-2025-24472 ) appliances to obtain initial access, and then deploy the Gunra ransomware as part of a double extortion model that combines data exfiltration and data encryption for maximum impact. Victims who refuse to pay up within five to seven days have their data published ...
LuckyMouse Hackers Target Banks, Companies and Governments in 2020

LuckyMouse Hackers Target Banks, Companies and Governments in 2020

Apr 29, 2021
An adversary known for its  watering hole attacks  against government entities has been linked to a slew of newly detected intrusions targeting various organizations in Central Asia and the Middle East. The malicious activity, collectively named "EmissarySoldier," has been attributed to a threat actor called LuckyMouse, and is said to have happened in 2020 with the goal of obtaining geopolitical insights in the region. The attacks involved deploying a toolkit dubbed SysUpdate (aka Soldier) in a number of breached organizations, including government and diplomatic agencies, telecom providers, a TV media company, and a commercial bank. LuckyMouse , also referred to as APT27 and Emissary Panda, is a sophisticated cyberespionage group that has a history of breaching multiple government networks in Central Asia and the Middle East. The actor has also been linked to cyberattacks aimed at transnational organizations such as the International Civil Aviation Organization ( ICAO )...
Cyber Espionage Group Earth Kitsune Deploys WhiskerSpy Backdoor in Latest Attacks

Cyber Espionage Group Earth Kitsune Deploys WhiskerSpy Backdoor in Latest Attacks

Feb 20, 2023 Cyber Threat / Cyber Espionage
The cyber espionage threat actor tracked as  Earth Kitsune  has been observed deploying a new backdoor called WhiskerSpy as part of a social engineering campaign. Earth Kitsune, active since at least 2019, is  known  to primarily target individuals interested in North Korea with self-developed malware such as dneSpy and agfSpy. Previously documented intrusions have entailed the use of watering holes that leverage browser exploits in Google Chrome and Internet Explorer to activate the infection chain. The differentiating factor in the latest attacks is a shift toward social engineering to trick users into visiting compromised websites related to North Korea, according to a new report from Trend Micro released last week. The cybersecurity company said the website of an unnamed pro-North Korean organization was hacked and modified to distribute the WhiskerSpy implant. The compromise was discovered at the end of last year. "When a targeted visitor tries to watch vi...
APT Hackers Distributed Android Trojan via Syrian e-Government Portal

APT Hackers Distributed Android Trojan via Syrian e-Government Portal

Jul 22, 2021
An advanced persistent threat (APT) actor has been tracked in a new campaign deploying Android malware via the Syrian e-Government Web Portal, indicating an upgraded arsenal designed to compromise victims. "To the best of our knowledge, this is the first time that the group has been publicly observed using malicious Android applications as part of its attacks," Trend Micro researchers Zhengyu Dong, Fyodor Yarochkin, and Steven Du  said  in a technical write-up published Wednesday. StrongPity , also codenamed  Promethium  by Microsoft, is believed to have been active since 2012 and has typically focused on targets across Turkey and Syria. In June 2020, the espionage threat actor was  connected  to a wave of activities that banked on watering hole attacks and tampered installers, which abuse the popularity of legitimate applications, to infect targets with malware. "Promethium has been resilient over the years," Cisco Talos  disclosed  last yea...
Dragon Breath APT Group Using Double-Clean-App Technique to Target Gambling Industry

Dragon Breath APT Group Using Double-Clean-App Technique to Target Gambling Industry

May 06, 2023 Advanced Persistent Threat
An advanced persistent threat (APT) actor known as  Dragon Breath  has been observed adding new layers of complexity to its attacks by adopting a novel  DLL side-loading  mechanism. "The attack is based on a classic side-loading attack, consisting of a clean application, a malicious loader, and an encrypted payload, with various modifications made to these components over time," Sophos researcher Gabor Szappanos  said . "The latest campaigns add a twist in which a first-stage clean application 'side'-loads a second clean application and auto-executes it. The second clean application side-loads the malicious loader DLL. After that, the malicious loader DLL executes the final payload." Operation Dragon Breath, also tracked under the names APT-Q-27 and Golden Eye, was  first   documented  by QiAnXin in 2020, detailing a watering hole campaign designed to trick users into downloading a trojanized Windows installer for Telegram. A  subsequen...
Experts Warn of Browser Extensions Spying On Users via Cloud9 Chrome Botnet Network

Experts Warn of Browser Extensions Spying On Users via Cloud9 Chrome Botnet Network

Nov 09, 2022
The Keksec threat actor has been linked to a previously undocumented malware strain, which has been observed in the wild masquerading as an extension for Chromium-based web browsers to enslave compromised machines into a botnet. Called  Cloud9  by security firm Zimperium, the malicious browser add-on comes with a wide range of features that enables it to siphon cookies, log keystrokes, inject arbitrary JavaScript code, mine crypto, and even enlist the host to carry out DDoS attacks. The extension "not only steals the information available during the browser session but can also install malware on a user's device and subsequently assume control of the entire device," Zimperium researcher Nipun Gupta  said  in a new report. The JavaScript botnet isn't distributed via Chrome Web Store or Microsoft Edge Add-ons, but rather through fake executables and rogue websites disguised as Adobe Flash Player updates. Once installed, the extension is designed to inject a JavaSc...
Researchers Link DragonEgg Android Spyware to LightSpy iOS Surveillanceware

Researchers Link DragonEgg Android Spyware to LightSpy iOS Surveillanceware

Oct 04, 2023 Mobile Security / Spyware
New findings have identified connections between an Android spyware called DragonEgg and another sophisticated modular iOS surveillanceware tool named LightSpy . DragonEgg , alongside WyrmSpy (aka AndroidControl), was  first disclosed  by Lookout in July 2023 as a strain of malware capable of gathering sensitive data from Android devices. It was attributed to the Chinese nation-state group APT41. On the other hand, details about LightSpy came to light in March 2020 as part of a campaign dubbed  Operation Poisoned News  in which Apple iPhone users in Hong Kong were targeted with watering hole attacks to install the spyware. Now, according to Dutch mobile security firm ThreatFabric, DragonEgg attack chains involve the use of a trojanized Telegram app that's designed to download a second-stage payload (smallmload.jar), which, in turn, is configured to download a third component codenamed Core. Further analysis of the artifacts has revealed that the Android varian...
WARNING: A New Android Zero-Day Vulnerability Is Under Active Attack

WARNING: A New Android Zero-Day Vulnerability Is Under Active Attack

Mar 23, 2021
Google has disclosed that a now-patched vulnerability affecting Android devices that use Qualcomm chipsets is being weaponized by adversaries to launch targeted attacks. Tracked as CVE-2020-11261 (CVSS score 8.4), the flaw concerns an "improper input validation" issue in Qualcomm's Graphics component that could be exploited to trigger memory corruption when an attacker-engineered app requests access to a huge chunk of the device's memory. "There are indications that CVE-2020-11261 may be under limited, targeted exploitation," the search giant said in an updated January security bulletin on March 18. CVE-2020-11261 was discovered and reported to Qualcomm by Google's Android Security team on July 20, 2020, after which it was fixed in January 2021. It's worth noting that the access vector for the vulnerability is "local," meaning that exploitation requires local access to the device. In other words, to launch a successful attack, the...
Microsoft Warns of North Korean Attacks Exploiting JetBrains TeamCity Flaw

Microsoft Warns of North Korean Attacks Exploiting JetBrains TeamCity Flaw

Oct 19, 2023
North Korean threat actors are actively exploiting a critical security flaw in JetBrains TeamCity to opportunistically breach vulnerable servers, according to Microsoft. The attacks, which entail the exploitation of  CVE-2023-42793  (CVSS score: 9.8), have been  attributed  to Diamond Sleet (aka Labyrinth Chollima) and Onyx Sleet (aka Andariel or Silent Chollima). It's worth noting that both the threat activity clusters are part of the infamous North Korean nation-state actor known as  Lazarus Group . In one of the two attack paths employed by Diamond Sleet, a successful compromise of TeamCity servers is followed by the deployment of a known implant called  ForestTiger  from legitimate infrastructure previously compromised by the threat actor. A second variant of the attacks leverages the initial foothold to retrieve a malicious DLL (DSROLE.dll aka RollSling or Version.dll or FeedLoad) that's loaded by means of a technique referred to as DLL searc...
CVE-2014-0322: Internet Explorer zero-day exploit targets US Military Intelligence

CVE-2014-0322: Internet Explorer zero-day exploit targets US Military Intelligence

Feb 15, 2014
Hackers are using a zero day vulnerability in Microsoft's Internet Explorer (IE) web browser and targeting US military personnels in an active attack campaign, dubbed as ' Operation Snowman' . FireEye Researchers have discovered that a U.S. veterans website was compromised to serve a zero day exploit, known as CVE-2014-0322 , which typically involves the compromise of a specific website in order to target a group of visitors known to frequent it. FireEye identified drive-by-download attack which has altered HTML code of the website and introduced JavaScript which creates malicious iFrame. “ A zero-day exploit (CVE-2014-0322) being served up from the U.S. Veterans of Foreign Wars’ website (VFW[.]org). We believe the attack is a strategic Web compromise targeting American military personnel, amid a paralyzing snowstorm at the U.S. ” According to FireEye, the zero day CVE-2014-0322 ' vulnerability is a previously unknown use-after-free bug in Microsof...
North Korean Hackers Found Behind a Range of Credential Theft Campaigns

North Korean Hackers Found Behind a Range of Credential Theft Campaigns

Nov 20, 2021
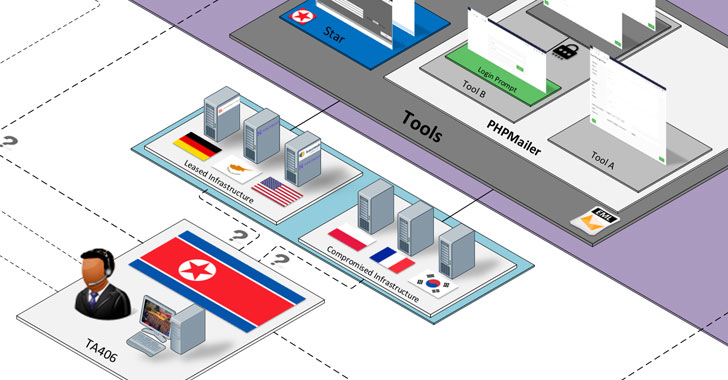
A threat actor with ties to North Korea has been linked to a prolific wave of credential theft campaigns targeting research, education, government, media and other organizations, with two of the attacks also attempting to distribute malware that could be used for intelligence gathering. Enterprise security firm Proofpoint  attributed  the infiltrations to a group it tracks as  TA406 , and by the wider threat intelligence community under the monikers  Kimsuky  ( Kaspersky ), Velvet Chollima ( CrowdStrike ), Thallium ( Microsoft ), Black Banshee ( PwC ), ITG16 ( IBM ), and the Konni Group ( Cisco Talos ). Policy experts, journalists and nongovernmental organizations (NGOs) were targeted as part of weekly campaigns observed between from January through June 2021, Proofpoint researchers Darien Huss and Selena Larson disclosed in a technical report detailing the actor's tactics, techniques, and procedures (TTPs), with the attacks spread across North America, Russi...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources