#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

Search results for distributed-denial-of-service | Breaking Cybersecurity News | The Hacker News

Cloudflare mitigated one of the largest DDoS attack involving 17.2 million rps

Cloudflare mitigated one of the largest DDoS attack involving 17.2 million rps

Aug 20, 2021
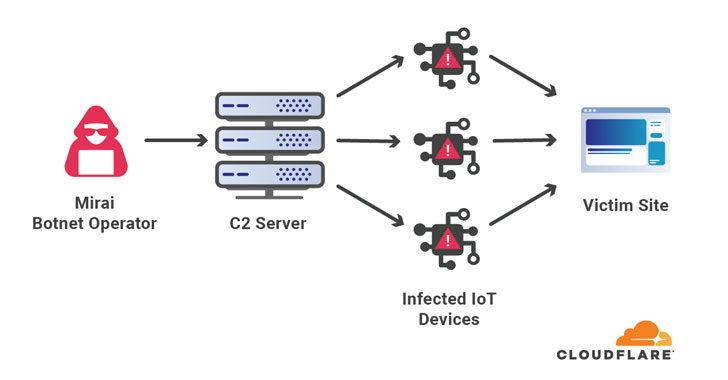
Web infrastructure and website security company Cloudflare on Thursday disclosed that it mitigated the largest ever volumetric distributed denial of service (DDoS) attack recorded to date. The attack, launched via a Mirai botnet, is said to have targeted an unnamed customer in the financial industry last month. "Within seconds, the botnet bombarded the Cloudflare edge with over 330 million attack requests," the company  noted , at one point reaching a record high of 17.2 million requests-per-second (rps), making it three times bigger than previously reported HTTP DDoS attacks. Volumetric DDoS attacks are designed to target a specific network with an intention to overwhelm its bandwidth capacity and often utilize  reflective amplification techniques  to scale their attack and cause as much operational disruption as possible. They also typically originate from a network of malware-infected systems — consisting of computers, servers, and IoT devices — enabling threat ac...
FBI Charges 6, Seizes 48 Domains Linked to DDoS-for-Hire Service Platforms

FBI Charges 6, Seizes 48 Domains Linked to DDoS-for-Hire Service Platforms

Dec 15, 2022 Cyber Attack / DDoS-for-Hire
The U.S. Department of Justice (DoJ) on Wednesday announced the seizure of 48 domains that offered services to conduct distributed denial-of-service (DDoS) attacks on behalf of other threat actors, effectively lowering the barrier to entry for malicious activity. It also charged six suspects – Jeremiah Sam Evans Miller (23), Angel Manuel Colon Jr. (37), Shamar Shattock (19), Cory Anthony Palmer (22), John M. Dobbs (32), and Joshua Laing (32) – for their alleged ownership in the operation. The websites "allowed paying users to launch powerful distributed denial-of-service, or DDoS, attacks that flood targeted computers with information and prevent them from being able to access the internet," the DoJ said in a press statement. The six defendants have been charged with running various booter (or stresser) services, including RoyalStresser[.]com, SecurityTeam[.]io, Astrostress[.]com, Booter[.]sx, IPStresser[.]com, and TrueSecurityServices[.]io. They have also been accused ...
New Cache Poisoning Attack Lets Attackers Target CDN Protected Sites

New Cache Poisoning Attack Lets Attackers Target CDN Protected Sites

Oct 23, 2019
A team of German cybersecurity researchers has discovered a new cache poisoning attack against web caching systems that could be used by an attacker to force a targeted website into delivering error pages to most of its visitors instead of legitimate content or resources. The issue could affect sites running behind reverse proxy cache systems like Varnish and some widely-used Content Distribution Networks (CDNs) services, including Amazon CloudFront, Cloudflare, Fastly, Akamai, and CDN77. In brief, a Content Distribution Network (CDN) is a geographically distributed group of servers that sit between the origin server of a website and its visitors to optimize the performance of the website. A CDN service simply stores/caches static files—including HTML pages, JavaScript files, stylesheets, images, and videos—from the origin server and delivers them to visitors more quickly without going back to the originating server again and again. Each of the geographically distributed CDN se...
cyber security

New Priorities for Critical Infrastructure: A Nation-State Threat Roundtable

websiteSANSCritical Infrastructure / Cybersecurity
Experts from SANS Institute, FirstEnergy, MITRE and Dragos unpack what leaders should prioritize next.
cyber security

AI adoption is outpacing IT visibility

website1PasswordSaaS Security / AI Governance
Individual dashboards only show part of the story. Learn how IT can get a unified view of AI spend and usage.
Europol Dismantles Criminal Messaging Service MATRIX in Major Global Takedown

Europol Dismantles Criminal Messaging Service MATRIX in Major Global Takedown

Dec 04, 2024 Encryption / Cybercrime
Europol on Tuesday announced the takedown of an invite-only encrypted messaging service called MATRIX that's created by criminals for criminal purposes. The joint operation, conducted by French and Dutch authorities under the moniker Passionflower , comes in the aftermath of an investigation that was launched in 2021 after the messaging service was discovered on the phone of a criminal convicted for the murder of a Dutch journalist Peter R. de Vries . This allowed authorities to intercept messages being sent via the service for a period of three months, amassing a total of more than 2.3 million messages in 33 languages. The messages, Europol said, are associated with serious crimes such as international drug trafficking, arms trafficking, and money laundering.  It's worth noting at this stage that MATRIX is different from the open-source, decentralized messaging app of the same name ("matrix[.]org"). Also known by other names such as Mactrix, Totalsec, X-quantum...
Imperva Thwarts 2.5 Million RPS Ransom DDoS Extortion Attacks

Imperva Thwarts 2.5 Million RPS Ransom DDoS Extortion Attacks

Mar 05, 2022
Cybersecurity company Imperva on Friday said it recently mitigated a ransom distributed denial-of-service (DDoS) attack targeting an unnamed website that peaked at 2.5 million requests per second (RPS). "While ransom DDoS attacks are not new, they appear to be evolving and becoming more interesting with time and with each new phase," Nelli Klepfish, security analyst at Imperva,  said . "For example, we've seen instances where the ransom note is included in the attack itself embedded into a URL request." The top sources of the attacks came from Indonesia, followed by the U.S., China, Brazil, India, Colombia, Russia, Thailand, Mexico, and Argentina. Distributed denial-of-service (DDoS) attacks are a subcategory of denial-of-service (DoS) attacks in which an army of connected online devices, known as a botnet, is used to overwhelm a target website with fake traffic in an attempt to render it unavailable to legitimate users. The California-headquartered firm s...
Muhstik Botnet Exploiting Apache RocketMQ Flaw to Expand DDoS Attacks

Muhstik Botnet Exploiting Apache RocketMQ Flaw to Expand DDoS Attacks

Jun 06, 2024 Botnet / DDoS Attack
Muhstik botnet exploits a critical Apache RocketMQ flaw (CVE-2023-33246) for remote code execution , targeting Linux servers and IoT devices for DDoS attacks and cryptocurrency mining . Infection involves executing a shell script from a remote IP, downloading the Muhstik malware binary ("pty3") , and ensuring persistence by copying to multiple directories and editing system files. With over 5,000 vulnerable Apache RocketMQ instances still exposed, organizations must update to the latest version to mitigate risks, while securing MS-SQL servers against brute-force attacks and ensuring regular password changes. The distributed denial-of-service (DDoS) botnet known as Muhstik has been observed leveraging a now-patched security flaw impacting Apache RocketMQ to co-opt susceptible servers and expand its scale. "Muhstik is a well-known threat targeting IoT devices and Linux-based servers, notorious for its ability to infect devices and utilize the...
Microsoft Fended Off a Record 2.4 Tbps DDoS Attack Targeting Azure Customers

Microsoft Fended Off a Record 2.4 Tbps DDoS Attack Targeting Azure Customers

Oct 12, 2021
Microsoft on Monday revealed that its Azure cloud platform mitigated a 2.4 Tbps distributed denial-of-service (DDoS) attack in the last week of August targeting an unnamed customer in Europe, surpassing a  2.3 Tbps attack  stopped by Amazon Web Services in February 2020. "This is 140 percent higher than  2020's 1 Tbps attack  and higher than any network volumetric event previously detected on Azure," Amir Dahan, senior program manager for Azure Networking,  said  in a post, calling it a " UDP reflection " lasting for about 10 minutes. Reflected amplification attacks are a type of denial of service attacks wherein a threat actor takes advantage of the connectionless nature of UDP protocol with spoofed requests so as to overwhelm a target server or network with a flood of packets, causing disruption or rendering the server and its surrounding infrastructure unavailable. The attack is said to have originated from a botnet of approximately 70,000 compromi...
Anti-DDoS Services Abused to Carry Out DDoS Attack with 1.5 Billion Requests/Minute

Anti-DDoS Services Abused to Carry Out DDoS Attack with 1.5 Billion Requests/Minute

May 12, 2014
Till Now the Internet was encountering the traditional Distributed Denial of Service (DDoS) attacks , where a large number of compromised systems use to flood servers with tremendous amount of bandwidth; but in past few months we have noticed massive change in the techniques of DDoS attack. Hackers are using creative, but evil DDoS techniques such as NTP and DNS Amplification DDoS attacks. Last month we have seen that how cybercriminals abused a vulnerability in one of the biggest Chinese video hosting website Sohu.com to convert their millions of visitors to participate into the Layer 7 (Application Layer) DDoS attack with 20 Million requests. According to the new report released by a US based security solutions provider Incapsula , another interesting DDoS attack activities have been noticed by the researchers in which an attacker abused two major anti-DDoS Service providers to perform massive DDoS attack on other websites. Its really EPIC that the services who should...
Largest Ever 400Gbps DDoS attack hits Europe uses NTP Amplification

Largest Ever 400Gbps DDoS attack hits Europe uses NTP Amplification

Feb 12, 2014
The Distributed Denial of Service (DDoS) attack is the one of favourite weapon for the hackers to temporarily suspend services of a host connected to the Internet and till now nearly every big site had been a victim of this attack. Since 2013, Hackers have adopted new tactics to boost Distributed Denial of Service attack sizes, which is known as ‘ Amplification Attack ’, that provide the benefits of obscuring the source of the attack, while enabling the bandwidth to be used to multiply the size of the attack. Just yesterday, hackers have succeeded in reaching new heights of the massive DDoS attack targeting content-delivery and anti-DDoS protection firm CloudFlare , reaching more than 400Gbps at its peak of traffic, striking at the company’s data servers in Europe. “ Very big NTP reflection attack hitting us right now. Appears to be bigger than the #Spamhaus attack from last year. Mitigating ,” CloudFlare CEO Matthew Price said in a tweet. “ Someone’s got a big, new...
Massive 167Gbps DDoS attacks against Banking and Financial Institutions

Massive 167Gbps DDoS attacks against Banking and Financial Institutions

May 31, 2013
DDoS attackers attempted to bring down an Banking services earlier this week using one of the largest Distributed denial of service attack using DNS reflection technique. Prolexic, the global leader in Distributed Denial of Service (DDoS) protection services, announced  that it has successfully mitigated the largest DNS reflection attack ever recorded, which peaked at 167 Gigabits per second (Gbps). The company did not name the target of the digital assault. DNS-reflection was the attack method used in Operation Stophaus , an attack waged in March by The Spamhaus Project, a Geneva-based not-for-profit organization dedicated to fighting Internet spam . When Spamhaus was assaulted by a vast 300Gbps peak DNS reflection attack, it engaged the help of a content delivery network (CDN) called CloudFlare to help defend itself. The DNS Reflection Denial of Service (DrDoS) technique exploits security weaknesses in the Domain Name System (DNS) Internet protocol. Using Inte...
Radware’s Attack Mitigation System Delivers the First Fully Integrated Solution to Fight Cyber Attacks in Real Time

Radware’s Attack Mitigation System Delivers the First Fully Integrated Solution to Fight Cyber Attacks in Real Time

Sep 21, 2011
Radware’s Attack Mitigation System Delivers the First Fully Integrated Solution to Fight Cyber Attacks in Real Time The solution blocks the new breed of sophisticated attacks that target Multiple layers of the IT infrastructure .  Today's point security tools for IT infrastructures are not enough to protect against the new wave of sophisticated cyber attacks. That's why  Radware  (NASDAQ: RDWR), a leading provider of  application delivery  and  application security  solutions for virtual and cloud data centers, today announced Radware Attack Mitigation System (AMS), the industry's first fully integrated IT security strategy and portfolio that protects the application infrastructure in real time against network and application downtime, application vulnerability exploitation, malware spread, information theft, Web service attacks and Web defacement. Additional Resources   ·            ...
DDoSia Attack Tool Evolves with Encryption, Targeting Multiple Sectors

DDoSia Attack Tool Evolves with Encryption, Targeting Multiple Sectors

Jul 04, 2023 Malware / Cyber Attack
The threat actors behind the  DDoSia  attack tool have come up with a new version that incorporates a new mechanism to retrieve the list of targets to be bombarded with junk HTTP requests in an attempt to bring them down. The updated variant, written in Golang, "implements an additional security mechanism to conceal the list of targets, which is transmitted from the [command-and-control] to the users," cybersecurity company Sekoia  said  in a technical write-up. DDoSia is attributed to a pro-Russian hacker group called  NoName(057)16 . Launched in 2022 and a successor of the  Bobik botnet , the attack tool is  designed  for staging distributed denial-of-service (DDoS) attacks against targets primarily located in Europe as well as Australia, Canada, and Japan. Lithuania, Ukraine, Poland, Italy, Czechia, Denmark, Latvia, France, the U.K., and Switzerland have emerged as the most targeted countries over a period ranging from May 8 to June 26, 202...
BitTorrent Fixes Reflective DDoS Attack Security Flaw

BitTorrent Fixes Reflective DDoS Attack Security Flaw

Aug 28, 2015
Two weeks ago, we reported how a serious flaw in the popular peer-to-peer BitTorrent file sharing protocols could be exploited to carry out a devastating distributed denial of service (DDoS) attack, allowing lone hackers with limited resources to take down large websites. Good news is that the developers of BitTorrent have fixed the security issue in its service that is being used by hundreds of Millions of users worldwide. In a blog post published Thursday, BitTorrent announced that the flaw was resided in a reference implementation of the Micro Transport Protocol (uTP) called libuTP , which is used by many widely used BitTorrent clients such as μTorrent , Vuze and Mainline . The San Francisco company also announced that it has rolled out a patch for its libuTP software that will stop miscreants from abusing the p2p protocol to conduct Distributed Reflective Denial-of-Service (DRDoS) attacks. DRDoS attack is a more sophisticated form of conventional DDoS att...
U.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS Attacks

U.S. Seizes NightmareStresser Domains Linked to Hundreds of Thousands of DDoS Attacks

Sep 17, 2026 Cybercrime / DDoS-for-Hire
The U.S. Department of Justice (DoJ) on Tuesday announced the court-authorized seizure of internet domains associated with a distributed denial-of-service (DDoS)-for-hire service known as NightmareStresser. The domains in question are: nightmare-stresser[.]com and nightmarestresser[.]org. Visitors to the sites are now greeted by a seizure banner that states - "This domain has been seized by the Federal Bureau of Investigation in accordance with a seizure warrant pursuant to 18 U.S.C. §§ 981(a)(1)(A) and (b), 982(b)(1), and 1030(i) (1)(A); and 21 U.S.C. § 853 issued by the United States District Court for the District of Alaska as part of a joint international law enforcement operation and action by: United States Attorney's Office for the District of Alaska, Federal Bureau of Investigation (FBI) Anchorage Field Office, [and] Royal Canadian Mounted Police (RCMP)." These so-called booter services are usually advertised as stress testing utilities but have been used t...
Gene Simmons v. Anonymous : FBI raids Gig Harbor home in search of hacker who targeted Kiss frontman

Gene Simmons v. Anonymous : FBI raids Gig Harbor home in search of hacker who targeted Kiss frontman

May 07, 2011
Gene Simmons v. Anonymous : FBI raids Gig Harbor home in search of hacker who targeted Kiss frontman The FBI has raided the Gig Harbor home of an alleged hacker suspected in a cyber attack against Kiss bassist Gene Simmons. The October attack purportedly conducted by Anonymous – the same hacker group Sony claims crashed the Playstation Network – left the 61-year-old glam rocker’s websites down for about a week after he spoke at an anti-online piracy conference. Now, an FBI cyber crime squad has traced the attack to a Gig Harbor home where agents seized computer equipment late last month. In court documents filed with the U.S. District Court in Tacoma, a Los Angeles-based FBI special agent alleged the perpetrator of the attack was “most likely” someone living at the Gig Harbor residence. Writing the court, though, the agent, a member of the Bureau cyber crime unit, stopped short of saying so with certainty. “I believe that someone with access to the computer at the subject r...
DOJ Charges 22-Year-Old for Running RapperBot Botnet Behind 370,000 DDoS Attacks

DOJ Charges 22-Year-Old for Running RapperBot Botnet Behind 370,000 DDoS Attacks

Aug 20, 2025 Botnet / Cybercrime
A 22-year-old man from the U.S. state of Oregon has been charged with allegedly developing and overseeing a distributed denial-of-service (DDoS)-for-hire botnet called RapperBot . Ethan Foltz of Eugene, Oregon, has been identified as the administrator of the service, the U.S. Department of Justice (DoJ) said. The botnet has been used to carry out large-scale DDoS-for-hire attacks targeting victims in over 80 countries since at least 2021. Foltz has been charged with one count of aiding and abetting computer intrusions. If convicted, he faces a maximum penalty of 10 years in prison. In addition, law enforcement authorities conducted a search of Foltz's residence on August 6, 2025, seizing administrative control of the botnet infrastructure. "RapperBot, aka 'Eleven Eleven Botnet' and 'CowBot,' is a Botnet that primarily compromises devices like Digital Video Recorders (DVRS) or Wi-Fi routers at scale by infecting those devices with specialized malware,"...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources