#1 Trusted Cybersecurity News Platform
Followed by 5.70+ million
The Hacker News Logo
Get the Latest News
cybersecurity

session hijacking | Breaking Cybersecurity News | The Hacker News

Category — session hijacking
Alibaba Marketplace Vulnerability Puts Millions Of Shoppers at Risk

Alibaba Marketplace Vulnerability Puts Millions Of Shoppers at Risk

Dec 12, 2014
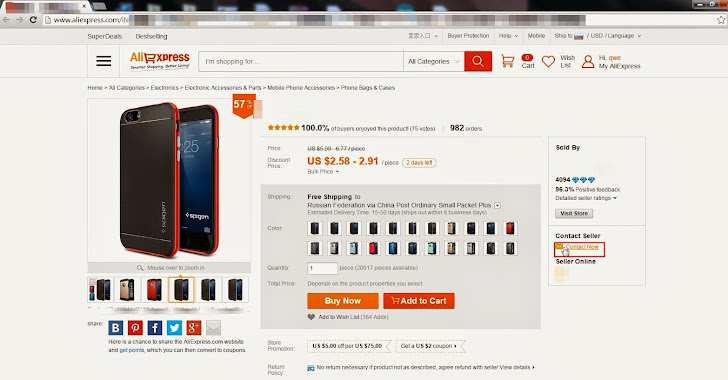
Alibaba Group has patched a major security vulnerability in one of its e-commerce portals that exposed account details of tens of millions of Merchants and shoppers to cyber criminals. An Israeli application security firm, AppSec Labs, found a Cross site scripting (XSS) vulnerability in AliExpress, the company’s English language e-commerce site that was found vulnerable to similar flaw a week ago that compromised personal information of Alibaba customers. The flaw was fixed shortly after Cybermoon security firm disclosed it to Alibaba. AliExpress is an online marketplace owned by Chinese E-Commerce giant Alibaba.com, also known as Google of China. The company serves more than 300 Million active users from more than 200 countries including the U.S., Russia and Brazil. But the critical vulnerability found by the researcher could allow an attacker to hijack merchant’s account. Using AliExpress XSS vulnerability an attacker can inject any malicious payload script as v...
LinkedIn Boosts Security With New Session Alert and Privacy Control Tools

LinkedIn Boosts Security With New Session Alert and Privacy Control Tools

Sep 04, 2014
With a need to give more controls in users’ hands, LinkedIn has introduced a few new security features that the company says will help users of the social network for professionals keep their accounts and data more secure. SESSION ALERTS Just like Google, Facebook, Yahoo and other online services, LinkedIn has added a new option within the settings tab that allows users to see where and on what devices they are logged into their account. From there, users can sign out of various sessions with one click. This will include details about the users’ current sessions, the browser name, operating system, carrier and IP address, which is used to give an approximate location of the device through which the session is occurring. Just like the Facebook feature, LinkedIn lets people to approve the devices to be used, and if somebody accesses a user’s LinkedIn account from an unapproved device it will alert user. PASSWORD ALERTS LinkedIn has also introduced its password c...
Instagram Mobile App Issue Leads to Account Hijacking Vulnerability

Instagram Mobile App Issue Leads to Account Hijacking Vulnerability

Jul 28, 2014
In the era of Government surveillance, ensuring the security and safety of our private communications regardless of platform – email, VOIP, message, even cookies stored – should be the top priority of the Internet industry. Some industry came together to offer Encryption as the protection against government surveillance, but some left security holes that may expose your personal data. A critical issue on Instagram’s Android Application has been disclosed by a security researcher that could allow an attacker to hijack users’ account and successfully access private photos, delete victim's photos, edit comments and also post new images. Instagram , acquired by Facebook in April 2012 for approximately US$1 billion, is an online mobile photo-sharing, video-sharing and social networking service that enables its users to take pictures and videos, apply digital filters, and share them on a variety of social networking services, such as Facebook, Twitter, Tumblr and Flickr. ...
cyber security

How to Discover Shadow AI - What's Working For Modern Teams

websiteNudge SecuritySaaS Security / AI Security
Find the AI apps, accounts, agents, and integrations your employees have introduced. No surveys, no guesswork, no waiting for someone to self-report.
cyber security

10 Hours vs. 50 Seconds: An MDR Response Gap

websiteProphet SecurityAI SOC / Cybersecurity
Here are 4 things your MDR isn’t telling you and 5 questions to bring to your renewal conversation.
Facebook SDK Vulnerability Puts Millions of Smartphone Users' Accounts at Risk

Facebook SDK Vulnerability Puts Millions of Smartphone Users' Accounts at Risk

Jul 03, 2014
Security researchers from MetaIntell, the leader in intelligent led Mobile Risk Management (MRM), have discovered a major security vulnerability in the latest version of Facebook SDK that put millions of Facebook user's Authentication Tokens at risk. Facebook SDK for Android and iOS is the easiest way to integrate mobile apps with Facebook platform, which provides support for Login with Facebook authentication, reading and writing to Facebook APIs and many more. Facebook OAuth authentication or ‘ Login as Facebook ’ mechanism is a personalized and secure way for users to sign into 3rd party apps without sharing their passwords. After the user approves the permissions as requested by the application, the Facebook SDK implements the OAuth 2.0 User-Agent flow to retrieve the secret user’s access token required by the apps to call Facebook APIs to read, modify or write user's Facebook data on their behalf. ACCESSING UNENCRYPTED ACCESS TOKEN It is important that ...
Thousands of websites based on Ruby on Rails vulnerable to Cookie Handling flaw

Thousands of websites based on Ruby on Rails vulnerable to Cookie Handling flaw

Nov 29, 2013
Ruby on Rails contains a flaw in its design that may allow attackers to more easily access applications. Websites that rely on Ruby on Rails’s default cookie storage mechanism   CookieStore  are at risk. The vulnerability was actually reported two months ago, but still thousands of website are running a vulnerable version of Ruby on Rails that allows a malicious attacker to gain unauthorized access again and again without password, if someone manages to steal users' cookies via via cross site scripting or session sidejacking or with physical access.  More than 10,000 websites are vulnerable to Ruby on Rails's cookie storage mechanism flaw, but this vulnerability requires your user's session cookies to be compromised in the first place. Security researcher G.S. McNamara provided the details of the vulnerability in a blog post , he analyzed nearly 90,000 sites running specialized scripts and discovered 1,897 sites based on old versions of Ruby on Rails ( versi...
Vulnerability in HTC website allow attacker to hijack accounts

Vulnerability in HTC website allow attacker to hijack accounts

Dec 28, 2012
Thamatam Deepak (Mr.47™) reported a Cross site scripting (XSS) Vulnerability and cookie handling in HTC website, that allow an attacker to HTC website hijack accounts. Mr. Deepak is a 16 years old whitehat hacker, listed in Apple Hall of Fame with 'The Hacker News' researcher Mohit Kumar this month. Cross-Site Scripting attacks are a type of injection problem, in which malicious scripts are injected into the otherwise benign and trusted web sites. The malicious script can access any cookies, session tokens, or other sensitive information retained by your browser. This vulnerability may be used by attackers to bypass access controls such as the same origin policy. Cross site scripting is very common web application vulnerability, Yesterday our security researcher, Christy Philip Mathew reported about multiple xss in official latest versions of cPanel and WHM . As reported by Whitehat hacker Deepak, there are multiple xss in HTC website, that a...
Exclusive : Hacking Hotmail and Outlook accounts using Cookie reuse vulnerability

Exclusive : Hacking Hotmail and Outlook accounts using Cookie reuse vulnerability

Dec 14, 2012
This Friday I was working with my co-security researcher " Christy Philip Mathew " in +The Hacker News  Lab for testing the Cookie Handling Vulnerabilities in the most famous email services i.e Hotmail and Outlook. Well, both are merged now and part of the same parent company - Microsoft, the software giant.  Vulnerability allows an attacker to Hijack accounts in a very simple way, by just exporting & importing cookies of an user account from one system to attacker's system, and our results shows that even after logout by victim, the attacker is still able to reuse cookies at his end. There are different way of stealing cookies, that we will discuss below. In May 2012, another Indian security researcher Rishi Narang claimed similar vulnerability in Linkedin website. Vulnerability Details Many websites including Microsoft services uses cookies to store the session information in the user's web browser. Cookies are responsible for main...
Expert Insights Articles Videos
Cybersecurity Resources