#1 Trusted Cybersecurity News Platform
Followed by 5.80+ million
The Hacker News Logo
Get Updates
cybersecurity

Edward Snowden | Breaking Cybersecurity News | The Hacker News

Category — Edward Snowden
Mozilla recommends the use of Open Source Browsers against State Surveillance

Mozilla recommends the use of Open Source Browsers against State Surveillance

Jan 14, 2014
After the revelations from NSA internal documents leaked by Edward Snowden, the world knows the NSA as the Real Techie Gangster of this 21st Century, with the ability to brutally infiltrate every kind of electronic device, the Internet, and global communications.  " It is becoming increasingly difficult to trust the privacy properties of software and services we rely on to use the Internet. Governments, companies, groups and individuals may be surveilling us without our knowledge. " The Inventor of JavaScript & current CTO of Mozilla, Mr. Brendan Eich said in a blog post NSA is not just focused on high-tech exploits, but also specialize in inserting secret backdoor to legitimate products. Its Tailored Access Operations (TAO) unit works with the CIA and FBI to intercept shipments of hardware to insert spyware into the devices. This way NSA is able to keep an eye on all levels of our digital lives, from computing centers to individual computers, and from laptops to mobi...
Yahoo Mail turns on HTTPS encryption by default to protect users

Yahoo Mail turns on HTTPS encryption by default to protect users

Jan 09, 2014
After the release of NSA Secret spying over Internet communications, I am expecting from all tech companies to make surveillance significantly harder. Yahoo has HTTPS encryption support since late 2012, but users had to opt in to use the feature. Documents revealed by the Edward Snowden shows that the NSA secretly accessed data from several tech giants, including Yahoo, by intercepting unencrypted Internet traffic in a program called Muscular. As promised back in October 2013,  Yahoo  has finally enabled the HTTPS connections by default for their users, that will now automatically encrypts the connections between users and its email service. Jeff Bonforte , senior vice-president of communication products at Yahoo announced  in a blog post: It is 100% encrypted by default and protected with 2,048 bit certificates. This encryption extends to your emails, attachments, contacts, as well as Calendar and Messenger in Mail. HTTPS by default is really a good news fo...
What Is PGP Encryption And How To Encrypt Your Emails

What Is PGP Encryption And How To Encrypt Your Emails

Jan 08, 2014
Now that we have enough details about how the NSA's Surveillance program, running for a long time against almost each country of this planet.  Hundreds of top-secret NSA documents provided by whistleblower Edward Snowden already exposed that Spying projects like PRISM and MUSCULAR are tapping directly into Google and Yahoo internal networks to access our Emails. NSA's tactics are even capable to defeat the SSL encryption, so unsecured email can easily be monitored and even altered as it travels through the Internet. One major point on which all of us are worrying is about the privacy of communication among each other and If you're looking for a little personal privacy in your communications you will need to encrypt your messages. To avoid privacy breaches; rather I should say to make it more difficult for the NSA or British GCHQ surveillance program to read our communication, we should use PGP encryption (Pretty Good Privacy). Why we should Enc...
cyber security

OAuth review checklist: 4 steps to assess risk [Free Guide

websiteNudge SecurityMCP Security / SaaS Security
Uncover risky OAuth grants and MCP server connections to protect your org from supply-chain attacks.
cyber security

Put Your First Email Security Agent to Work Uncovering Hidden Threats.

websiteAdaptive SecurityEmail Security
Find phishing, BEC, and invoice fraud with Adaptive's 14-day read-only email scan. No MX changes required.
Kali Linux introducing Emergency Self Destruct feature to Full Disk Encryption

Kali Linux introducing Emergency Self Destruct feature to Full Disk Encryption

Jan 08, 2014
Full disk encryption is expected to be the top security technology to be adopted this year. Take a moment to think about the information that is present on your personal computer, i.e. Photo s , passwords, emails, Important documents from work or  Financial data and  trade secrets. Many of us from the Security Industry obviously have enough confidential and important data regarding our work, source codes, or researches stored in our laptops or systems. What if your computer is stolen or seized by any Law enforcement agency at the Airport? Best example to explain the situation is as follows: We all know  Guardian journalist ' Glenn Greenwald ', who  has written a series of stories in July 2013 revealing the NSA's secret surveillance programs, leaked by whistleblower Edward Snowden . In August 2013,  The partner of the Guardian journalist ' Glenn Greenwald ', was returning from a trip to Berlin when he was stopped by officers at the Airpor...
NSA will not stop spying on us, next move Quantum computer to break strongest Encryption

NSA will not stop spying on us, next move Quantum computer to break strongest Encryption

Jan 04, 2014
Image Credit: The guardian  If I say that  NSA (National Security Agency) will never stop spying on us then it won’t be wrong. After the exposure of the large number of surveillance scandals including PRISM, DROPOUTJEEP, XKeyscore and many many more which are now publicly known as well as unknown, Will NSA ever stop Privacy  breach? Obviously ' NO' . That I can predict from another Snowden leak published by the Washington Post news website recently i.e. US National Security Agency (NSA) is trying to develop a futuristic super computer called ' Quantum computer'  that could be capable of breaking almost every kind of encryption on the computer used to protect banks, medical, business including top-secret information held by government around the world. The Project is specified as “ Penetrating Hard Targets ” in the document and is a part of $79.7 million research program. The Washington Post says that the research is being done at the University of Mar...
Skype's Official Twitter, Facebook and Blog Hacked by Syrian Electronic Army

Skype's Official Twitter, Facebook and Blog Hacked by Syrian Electronic Army

Jan 02, 2014
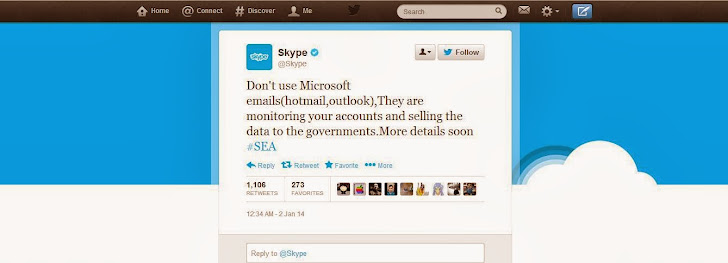
Happy 2014.. We are back with first hacking story of the year - SKYPE " Stop Spying " . Yes Skype Got hacked last night by an infamous hacker group called the Syrian Electronic Army , a group that supports Syria’s president and typically they publish pro-Syrian government messages, but its first time they are taking about PRIVACY . Syrian Hackers posted some messages on Skype’s Twitter account i.e. " Stop Spying on People! via Syrian Electronic Army ," Next tweet reads, " Don't use Microsoft emails (hotmail, outlook), They are monitoring your accounts and selling it to the governments. " Syrian Electronic Army hackers also compromised Skype’s Facebook page and a company blog hosted on Skype’s website. A blog post published on the official Skype blog featured the headline, " Hacked by Syrian Electronic Army.. Stop Spying! ", which now has been deleted by Microsoft. Now it appeared that Skype regained the access to their accounts and dele...
RSA denied accusations of inserting secret backdoor for the NSA

RSA denied accusations of inserting secret backdoor for the NSA

Dec 23, 2013
According to media reports in September, documents released by whistleblower Edward Snowden have confirmed the existence of backdoor in some technologies RSA . Last Friday, The Reuters News Agency accused the Security firm RSA for taking a $10 million ‘ bribe ’ from the National Security Agency ( NSA ) in order promote a flawed encryption by including it in its BSAFE product to facilitate NSA spying . Today In a blog post , RSA has categorically denied accusation about any secret partnership with the National Security Agency to insert backdoor. " Recent press coverage has asserted that RSA entered into a “secret contract” with the NSA to incorporate a known flawed random number generator into its BSAFE encryption libraries. We categorically deny this allegation. " " We have never entered into any contract or engaged in any project with the intention of weakening RSA’s products " the company said. The company gave the following reasons for choosing and promoting...
NSA paid $10 Million bribe to RSA Security for Keeping Encryption Weak

NSA paid $10 Million bribe to RSA Security for Keeping Encryption Weak

Dec 21, 2013
If you own a world-renowned Security Product or a Service, National Security Agency (NSA) is ready to pay you 10 Million or more bribe for keeping intentional backdoor for them. According to an exclusive report published by Reuters , there is a secret deal between the NSA and respected encryption company RSA to implement a flawed security standard as the default protocol in its products. Earlier Edward Snowden leaks had revealed that the NSA created a flawed random number generation system (Dual_EC_DRBG), Dual Elliptic Curve , which RSA used in its Bsafe security tool and now Snowden has revealed that RSA received $10 million from NSA for keeping Encryption Weak. So, anyone who knows the right numbers used in Random number generator program, can decipher the resulting cryptotext easily. Recommending bad cryptographic standard is one thing, but accepting 10 million to deliberately implement is something very shameful for a respected Security company. The new ...
Judge Ruled - NSA Telephone Metadata Collection violates the Fourth Amendment

Judge Ruled - NSA Telephone Metadata Collection violates the Fourth Amendment

Dec 17, 2013
Big and Good news for all of us. A federal court judge ' Richard J. Leon ' said that he believes, US National Security Agency’s (NSA) controversial practice of routinely collecting the telephone records of millions of Americans likely violates the 4th Amendment and is unconstitutional, even though the FISA court approved it. Earlier in 2013, a conservative Legal Activist Larry Klayman filed a lawsuit against the US government, alleging that NSA’s massive telephone surveillance program violates the " reasonable expectation of privacy, free speech and association, right to be free of unreasonable searches and seizures and due process rights. " NYTimes reported that last Monday in the decision, Judge has ordered [  Case:  Klayman v. Obama (13-851)  PDF File  ] the NSA to stop collecting U.S. Citizen’s Telephone records, and to destroy the files it already holds. This was the first major court ruling about NSA' so-called metadata counter terrorism p...
BIOS Malware that can remotely destroy any computer, NSA claimed

BIOS Malware that can remotely destroy any computer, NSA claimed

Dec 16, 2013
During a CBS Interview show " 60 Minutes ", The National Security Agency (NSA) officials claimed that China has developed a BIOS based malware that can remotely destroy any computer. Obviously NSA is struggling to repair its image and in an effort to justify their extensive Surveillance programs, The NSA Director General Keith Alexander and Information Assurance Director Debora Plunkett made a number of claims. During that interview NSA officials said that they had foiled a malware attack that could have taken down the U.S. economy. " One of our analysts actually saw that the nation state had the intention to develop and to deliver, to actually use this capability to destroy computers ," Plunkett said. They have mentioned that this malware was distributed via social engineering and targeted emails, although the NSA director mentioned that their researchers worked with computer manufacturers and able to close the respective vulnerability . " This ...
CloudFlare's Red October Crypto app with two-man rule style Encryption and Decryption

CloudFlare's Red October Crypto app with two-man rule style Encryption and Decryption

Dec 06, 2013
It is always important to secure our system against outside threats i.e. Hackers, but it also required to protect against insider threats. The potential of damage from an Insider threat can be estimated from the example of Edward Snowden who had worked at the NSA , and had authorized access to thousands of NSA's Secret Documents, networks and systems. ' According to a recent Verizon report, insider threats account for around 14% of data breaches in 2013." Mostly, securing data involves just encryption in the cloud and keeping encryption keys out of the hands of rogue employees, but it is not enough where rogue employees should have access to encryption keys as part of their work. To prevent such risk of rogue employees misusing sensitive data, CloudFlare has released an open source encryption software " Red October ," with " two-man rule " style file encryption and decryption. " Two-man rule ", a control mechanism designed to achieve a hi...
CO-TRAVELER : NSA’s Cellphone Location Tracking Tool gathering 5 Billion records a day

CO-TRAVELER : NSA’s Cellphone Location Tracking Tool gathering 5 Billion records a day

Dec 05, 2013
Believe it or not, but the National Security Agency (NSA) is gathering nearly 5 billion records a day on mobile phone locations around the world. Snowden released documents that show that the NSA is tracking cell phone locations the world over as well as map the relationships of the mobile phone user and of course the purpose of this program is to identify terrorists and their networks overseas.  " Sophisticated mathematical techniques enable NSA analysts to map cell phone owners’ relationships by correlating their patterns of movement over time with thousands or millions of other phone users who cross their paths. " The Washington Post wrote. According to the WP, the NSA’s tracking tool is known as CO-TRAVELER , that tracks the locations of cell phones abroad as well as domestic cell phones that place calls abroad and capable of tracking cell phones even when they're not being used. ' U.S. Officials said the programs that collect and analyze location data are...
Super 'Stuxnet' Malware development in progress to destroy Iran’s nuclear program

Super 'Stuxnet' Malware development in progress to destroy Iran’s nuclear program

Dec 03, 2013
Saudi Arabia and Israel’s Mossad intelligence division are reportedly collaborating to develop a computer worm more destructive than the Stuxnet malware to spy on and destroy the software structure of Iran’s nuclear program. The Iranian Fars news agency has reported : “ Saudi spy chief Prince Bandar bin Sultan bin Abdulaziz Al Saud and director of Israel’s Mossad intelligence agency Tamir Bardo sent their representatives to a meeting in Vienna on November 24 to increase the two sides’ cooperation in intelligence and sabotage operations against Iran’s nuclear program. ”  “ One of the proposals raised in the meeting was the production of a malware worse than the Stuxnet to spy on and destroy the software structure of Iran’s nuclear program ,” But Why ? The report claims that Saudi Arabia and Israel were not particularly happy with the deal between between Iran and the Group 5+1 (the US, Russia, China, France and Britain plus Germany) and Israel has dubbed the deal as “ historic m...
NSA infected more than 50,000 computer networks with Malware

NSA infected more than 50,000 computer networks with Malware

Nov 23, 2013
The NSA has the ability to trace “ anyone, anywhere, anytime ”. In September we reported that how NSA and GCHQ planted malware via LinkedIn and Slashdot traffic to hack largest telecom company Belgacom's Engineers. Yesterday, a  Dutch newspaper has   published a new secret NSA document provided by former intelligence employee  Edward Snowden . According to the newly exposed slide, NSA has infected more than 50,000 computer networks worldwide with software designed to steal sensitive information i.e. Malware . The slide from the NSA's 2012 management presentation, shows a world map with more than 50,000 targeted locations, uses a procedure called ‘ Computer Network Exploitation ’ (CNE) that can secretly install malware in computer systems. The malware can be controlled remotely and be turned on and off at will. From the NSA website we found that, CNE includes enabling actions and intelligence collection via computer networks that exploit data gathere...
Snowden reveals, GCHQ planted malware via LinkedIn and Slashdot traffic to hack Belgacom Engineers

Snowden reveals, GCHQ planted malware via LinkedIn and Slashdot traffic to hack Belgacom Engineers

Nov 11, 2013
Edward Snowden , a former contractor at America's National Security Agency (NSA) , has rocked the intelligence world by leaking secret documents which reveal the previously unknown extent of global spying. But looks like the NSA isn't the only one using dirty digital tricks to hack its targets. Back in September, it was reported that the UK's equivalent of the NSA, GCHQ had hacked Belgacom , a leading telecommunications provider in Belgium. Some New analysis of the Snowden papers by German magazine Der Spiegel shows that British intelligence agency GCHQ created fake LinkedIn and Slashdot pages to spy on computers of  Belgacom  network engineers. Communications networks are particularly valuable to spies, because they allow instant access to individual users. Belgacom provides internet access to dozens of key EU institutions based in its capital city Brussels and its global roaming exchange is a hub for connections between various international mobile netwo...
Google engineers over surveillance scandal: 'Fuck you NSA'

Google engineers over surveillance scandal: 'Fuck you NSA'

Nov 06, 2013
On Tuesday, the Washington Post revealed a few more NSA slides released by Edward Snowden, which revealed that the spy agency NSA was infiltrating the private data links between Google and Yahoo data centers as part of a program called MUSCULAR . Chairman and former CEO of Google Eric Schmidt says the company’s executives are shocked by allegations that the National Security Agency has been collecting data from the search engine’s servers. “ It’s really outrageous that the NSA was looking between the Google data centers, if that’s true ,” he said. Overnight, Two Google's Security engineers -  Mike Hearn and   Brandon Downey expressed reasonable anger about the news on Google+, said " Fuck these guys ", where these represent NSA and GCHQ. I've spent the last ten years of my life trying to keep Google's users safe and secure from the many diverse threats Google faces. Fuck You to the people who made these slides. I am not American, I am a...
'Dark Mail Alliance', Future of surveillance proof email technology

'Dark Mail Alliance', Future of surveillance proof email technology

Oct 31, 2013
Yesterday I learned about  ' Dark Mail Alliance ', where  Lavabit , reportedly an email provider for NSA leaker Edward Snowden and Silent Circle comes together to create a surveillance-proof email technology. Ladar Levison at Lavabit and Silent Circle CEO Mike Janke, Founders of two e-mail services that recently shut down amid government efforts to nab encryption keys, as well as the larger revelations regarding the NSA's surveillance efforts. The newly developed technology has been designed to look just like ordinary email, with an interface that includes all the usual folders i.e. inbox, sent mail, and drafts. But where it differs is that it applies peer-to-peer encryption not only to the body of the digital missive, but also to its metadata (To:, From: and Subject fields) that third parties are most likely to collect. The encryption, based on a Silent Circle instant messaging protocol called SCIMP and the secret keys generated to encrypt the commun...
Cryptoseal VPN Service shuts down over legal concerns after Lavabit case

Cryptoseal VPN Service shuts down over legal concerns after Lavabit case

Oct 23, 2013
Yet another American Internet privacy service has bitten the dust, prompted by fears about broad government surveillance demands. CryptoSeal, a Virtual private network (VPN) based in California has decided to shutter its privacy-conscious service rather than hand over its encryption keys to the U.S. Government. VPNs are secure tunnels to the Internet that allow users to mask their location, defeat regional restrictions, stay safe over public Wi-Fi connections, and maintain at least a modicum of privacy online. CryptoSeal is the latest company to voluntarily shut down its service after the U.S. Government's legal action against Lavabit, an email service used by former NSA contractor Edward Snowden. “ With immediate effect as of this notice, CryptoSeal Privacy, our consumer VPN service, is terminated, ” a notice reads on the company's website. “ All cryptographic keys used in the operation of the service have been zerofilled...all records created incidental ...
⚡ Top Stories This Week
Expert Insights Articles Videos
Cybersecurity Resources